- 2026 Release Notes
- October 2026
- September 2026
- August 2026
- July 2026
- Attack Surface Insights
- Automation Management
- Cloud Collectors
- Dashboards
- Log Sources
- Log Stream
- New-Scale Platform
- Outcomes Navigator
- Search
- Site Collectors 2.21
- Threat Center
- Threat Detection Management
- Resolved Issues
- Site Collector 2.21: Resolved Issues
- Site Collector 2.21: Security Vulnerabilities Remediations
- June 2026
- Attack Surface Insights
- Automation Management
- Cloud Collectors
- Context Management
- Correlation Rules
- Dashboards
- Log Stream
- New-Scale Platform
- Outcomes Navigator
- Search
- Service Health and Consumption
- Site Collectors 2.20
- Threat Center
- Threat Detection Management
- Resolved Issues
- Site Collector 2.20: Security Vulnerabilities Remediations
- May 2026
- April 2026
- March 2026
- February 2026
- January 2026
- 2025 Release Notes
- December 2025
- November 2025
- October 2025
- September 2025
- August 2025
- July 2025
- June 2025
- May 2025
- April 2025
- March 2025
- February 2025
- January 2025
- Known Issues
Known Issues
The New-Scale Security Operations Platform includes the following known issues.
Attack Surface Insights
Issue ID | Description | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
ENG-96572 | String-type entity attribute values have a 512 character limit. Values above 512 characters are truncated. Workaround: Ensure event and context data have the most important information in the first 512 characters. | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
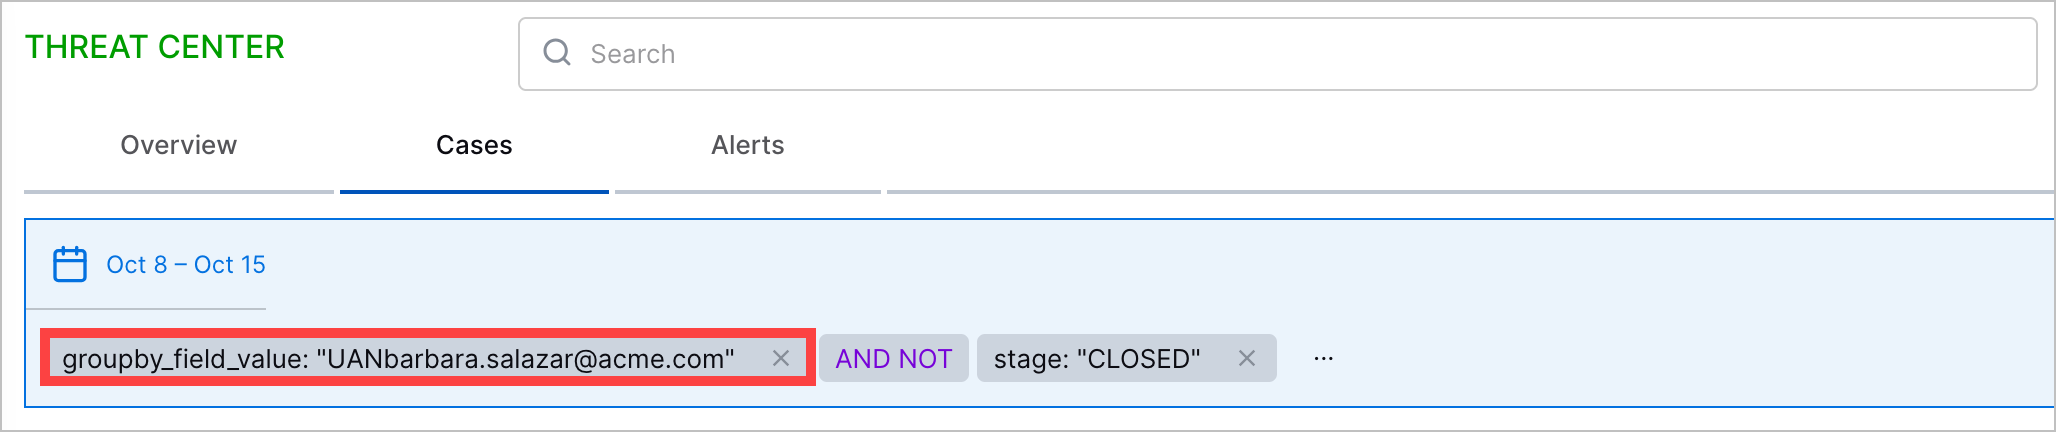
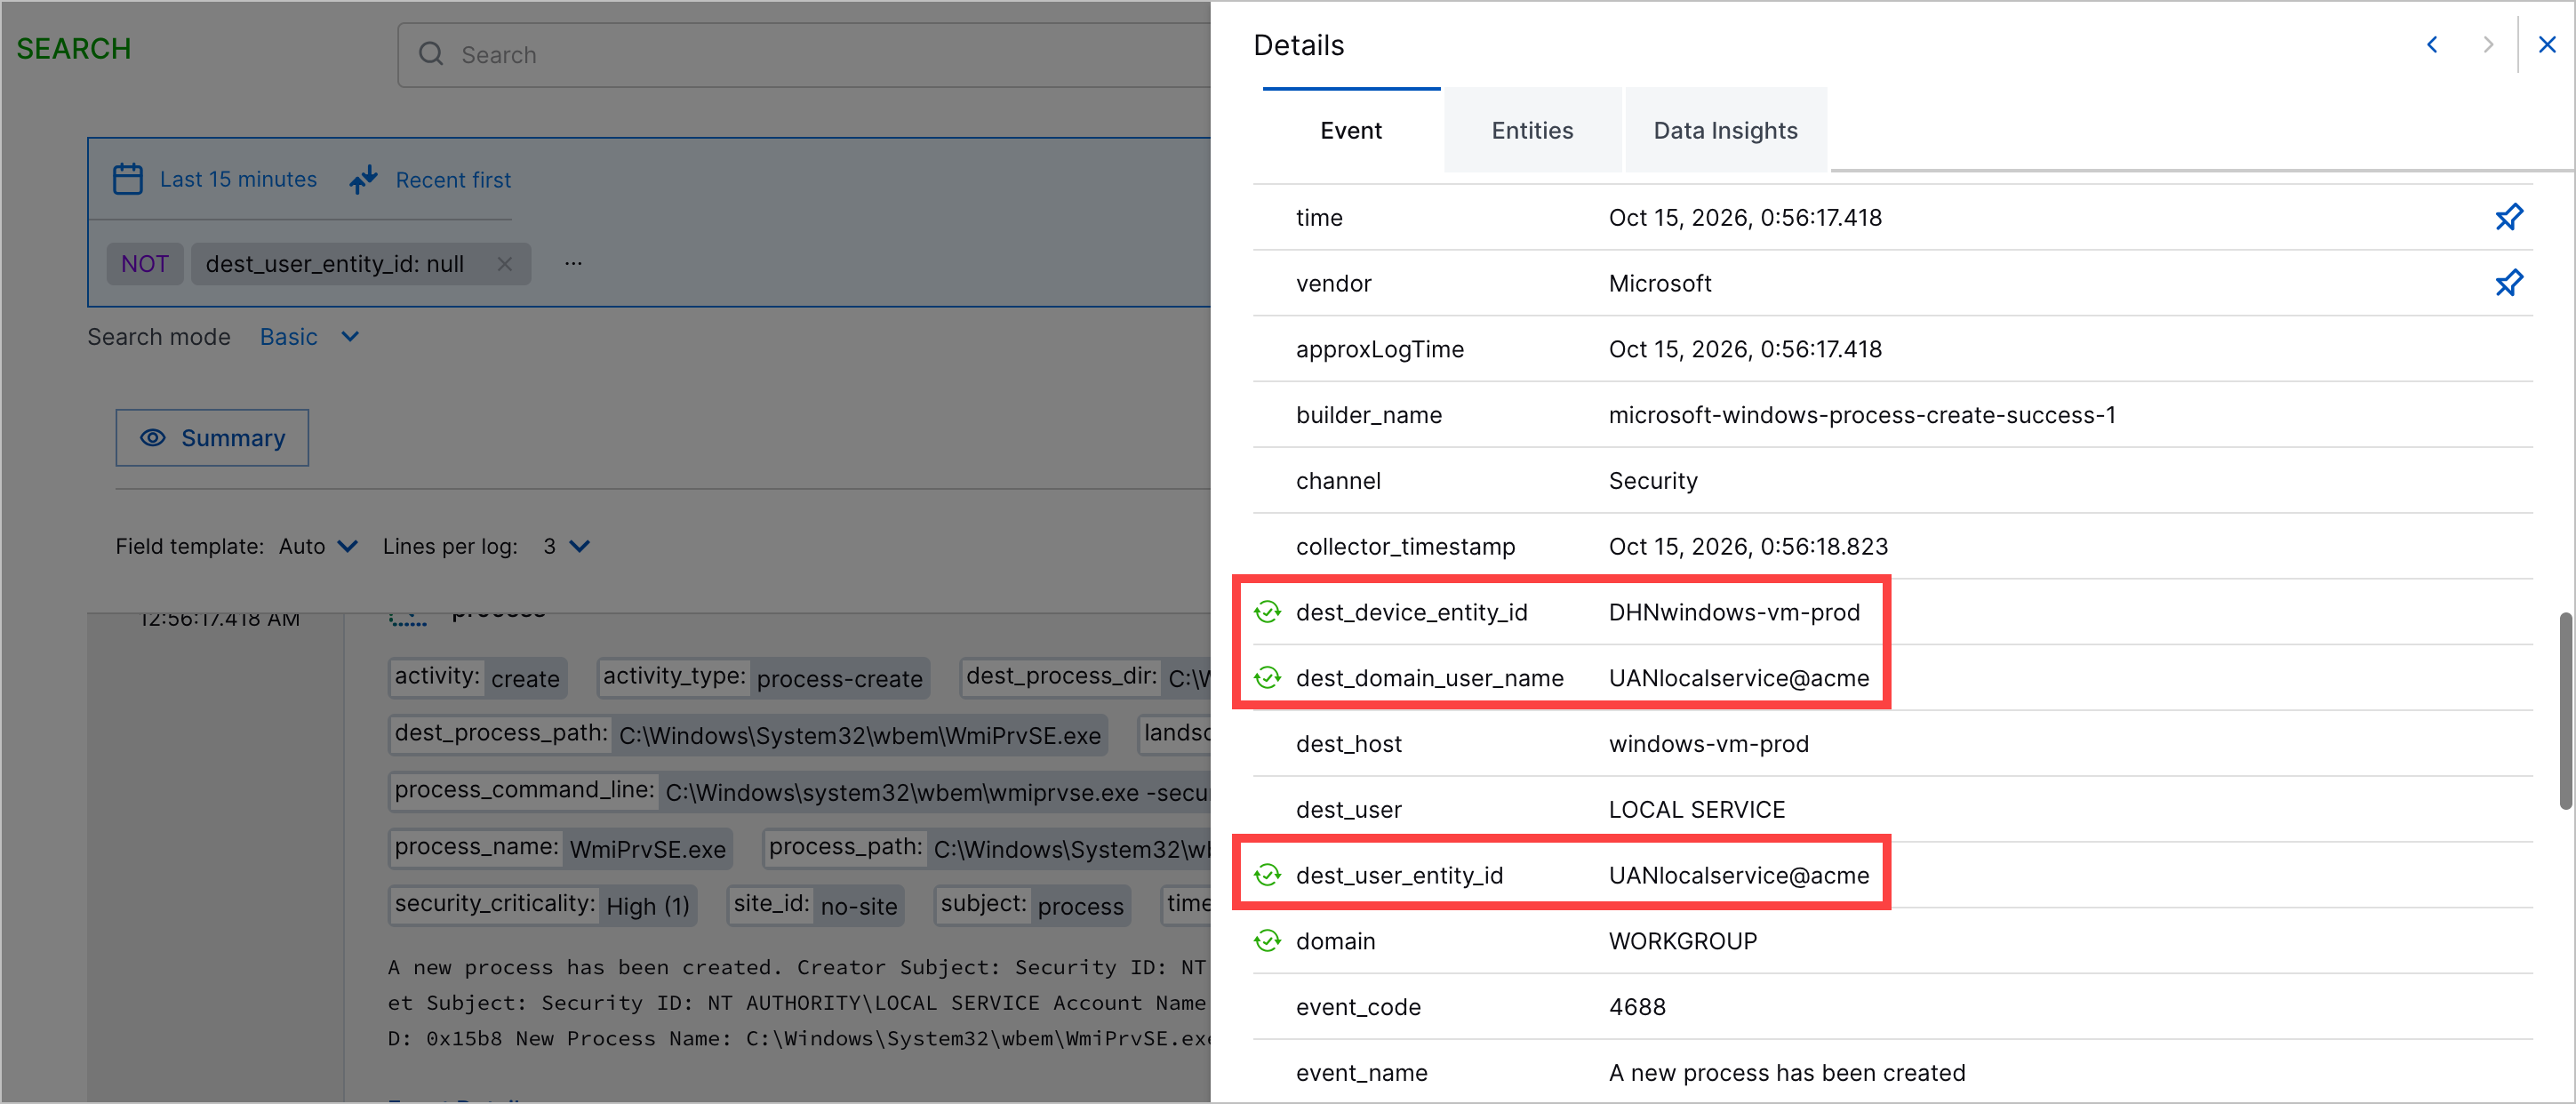
ENG-102318 | In some areas of the New-Scale Security Operations Platform, entity attribute values contain internal prefixes. These prefixes identify an entity attribute and are used internally for parsing and storage. In some cases, you may need to know how prefixes correspond to entity attributes:
You may also encounter internal prefixes in other areas of the platform. Workaround: Find the corresponding prefix for an entity attribute in the following table. Prefixes starting with a U are user entity attributes. Prefixes starting with a D are device entity attributes.
|
Automation Management
There are no known issues in Automation Management.
Cloud Collectors
Issue ID | Description |
|---|---|
NGSCL-88723 | The ChatGPT cloud collector may occasionally show duplicate events because of a technical mismatch in how the system tracks time. The collector requests data in seconds, but the source provides the data in milliseconds. Because of this difference, an event that occurs at the very end of a second might be captured in both the current and the next data update. |
Context Management
There are no known issues in Context Management.
Correlation Rules
ID | Description |
|---|---|
CRB-2368 | If you enter a description containing multiple lines, Case Manager incidents created using Correlation Rules may contain |
CRB-2767 | If a sequence detects the absence of a specific field value and you use the Group by Field functionality on that field, the correlation rule incorrectly triggers on the absence of grouped fields for which the sequence doesn't query. For example, if you use the Group by Field functionality on the |
Dashboards
ID | Description |
|---|---|
NGR-595 | Filters applying the is in the last operator to the Approx Log Time field yield inaccurate results when the time unit is equal to our greater than hours. As a workaround to this issue, express time lengths in seconds or minutes. 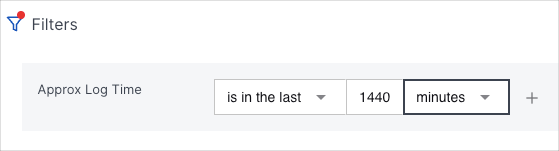 |
Log Sources
There are no known issues for Log Sources.
Log Stream
There are no known issues in Log Stream.
New-Scale Platform
There are no known issues in New-Scale Platform.
Outcomes Navigator
ID | Description |
|---|---|
NGCM-309 | Outcomes Navigator doesn't properly calculate coverage for Advanced Analytics rules whose rule expressions include session-end or sequence-end events. Affected Advanced Analytics rules include:
|
Search
ID | Description |
|---|---|
ENG-81372 | Currently, the option to select a sort order when exporting search results is not available. Exported search results are unordered. |
ENG-75846 | When using Exabeam Query Language (EQL) in advance search mode, usage of a For example, although the following EQL syntax is invalid, it is unintentionally successful: 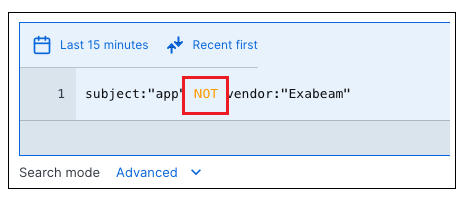 When this issue is resolved, searches that use this invalid syntax will stop working. Therefore, it is highly recommended to always use the explicit operators: |
NGS-4325 | Occasionally, when using advanced query language operators in Search to generate results in the Table view, the generated table is displayed with a misalignment. The header row is displayed to the left of the column data. This issue appears to be intermittent and has not been reliably reproduced for analysis and resolution. If you encounter this table misalignment issue, and can provide consistent steps to reproduce it, please contact your Exabeam account manager. |
NGS-3376 | Some users are experiencing the interface freezing and becoming unresponsive if they have their “Rows per view” setting set to 100. |
NGS-1104 | When using Safari, the field summary initial event count is inconsistent. |
Service Health and Consumption
ID | Description |
|---|---|
CC-1350 | Legacy cloud collector names are incorrectly displaying as unknown and unspecified on consumption details charts. Example: 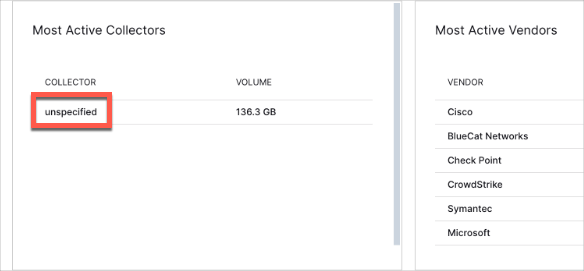 |
N/A | Service Health and Consumption dashboards are only available at this time for customers with Exabeam Security Operations Portfolio Licenses |
Site Collectors
Issue ID | Description |
|---|---|
NGSCL-1517 | Site Collector installation fails on RHEL 9 because of lack of network support for TLS v1.3 more secured ciphers, without a clear warning. |
NGSCL-1558 | A Site Collector instance occasionally produces an |
NGSCL-2447 | The search filters on the Site Collectors Overview page are case sensitive. Currently, search results are not displayed if you do not match the case with the collector instance name for the key words that you use for searching for collector instances. |
NGSCL-2569 | While editing a Site Collector instance, in Advanced Settings, the Timezone field after initial configuration displays the first city name of the time zone such as UTC/PST on the user interface instead of the exact city name which you selected. |
NGSCL-3674 | While upgrading a Site Collector instance to its latest version, the Windows Event Log agent collector pulls duplicate logs when historic log fetch is enabled. |
NGSCL-3961 | After upgrading a Site Collector instance from version 1.x to 2.x, the server side collectors Splunk, Oracle, MySQL, MSSQL, QRadar, and EStreamer start to fetch historical data based on an old start fetch timestamp. Workaround – If you are using Site Collector version 1.x with the server side collectors installed, and want to upgrade to 2.x version, ensure that you update the Start Fetch Date for the Splunk collector and Iterator column initial value for Oracle, MSSQL, and MySQL collectors to the current time or to the value based on the iterator you defined. Alternatively, you can choose to wait to upgrade the Site Collector instance from 1.x to 2.x version until this issue is fixed. |
Threat Center
ID | Description |
|---|---|
ENG-97163 | If you restart the Advanced Analytics Analytics Engine multiple times in rapid succession, Threat Center may create duplicate cases and alerts or split related detections across multiple cases and alerts. When the Advanced Analytics Analytics Engine is restarted multiple times, the system tries to terminate the previous reprocessing job before starting a new one. If the previous reprocessing job isn't terminated within five retries, the system starts a new processing job, even if the previous reprocessing job wasn't terminated. When concurrent jobs reprocess the same historical data, they may conflict and cause Threat Center cases and alerts to be unexpectedly duplicated or split. Workaround: Do not restart the Advanced Analytics Analytics Engine multiple times in rapid succession. Allow the previous reprocessing job to complete or terminate cleanly before starting another reprocessing job. |
Threat Detection Management
ID | Description |
|---|---|
ENG-105710 | contextFeature analytics rules may evaluate events they are not intended to evaluate because the analytics engine doesn't process the Workaround: Use |