
- Get Started with Threat Detection Management
- Analytics Rules
- Analytics Rule Classifications
- Create an Analytics Rule
- Manage Analytics Rules
- Tune Analytics Rules
- Find Analytics Rules
- Share Analytics Rules
- Troubleshoot Analytics Rules
- Analytics Rules Syntax
- Advanced Analytics Rule Syntax vs. Analytics Rule Syntax
- Logical Expressions in Analytics Rule Syntax'
- String Operations Using Analytics Rule Syntax
- Integer Operations Using Analytics Rule Syntax
- Time Operations Using Analytics Rule Syntax
- Network Operations Using Analytics Rule Syntax
- Context Operations Using Analytics Rule Syntax
- Entity Operations Using Analytics Rule Syntax
- Correlation Rule Operations Using Analytics Rule Syntax
- Analytics Engine Status
- Correlation Rules
- Correlation Rule Sequences
- Correlation Rules Templates
- Create Correlation Rules
- Create a Correlation Rule Using the Exabeam Nova Rule Creator
- Create a Correlation Rule from Scratch Using the Manual Rule Creator
- Create a Correlation Rule from a Template
- Create a Correlation Rule from Search
- Group by Field in Correlation Rules
- Detect Absent Events or Fields Using Correlation Rules
- Granular Suppression
- Correlation Rule Evaluation Delay
- Manage Correlation Rules
- Find Correlation Rules
- Share Correlation Rules
- View Correlation Rules Metrics
- Threat Scoring
- Get Notified About Threat Detection Management
Correlation Rules Templates
If you don't want to create a correlation rule from scratch, use a pre-built template.
Correlation Rules templates are correlation rules with a predefined search query and condition. You use them as a starting point for creating your own correlation rule.
To view correlation rules templates, in the Threat Detection Management Correlation Rules tab, click Templates.
To find a specific correlation rule template, you can sort and filter the list:
To sort the templates, click a column header. You can sort correlation rule templates by any column except DESCRIPTION.
To filter correlation rule templates by use case or MITRE ATT&CK® tactic, click the filter
 .
To view the details of a template, select a template from the list or click Details for the template. In the template details, you can view:
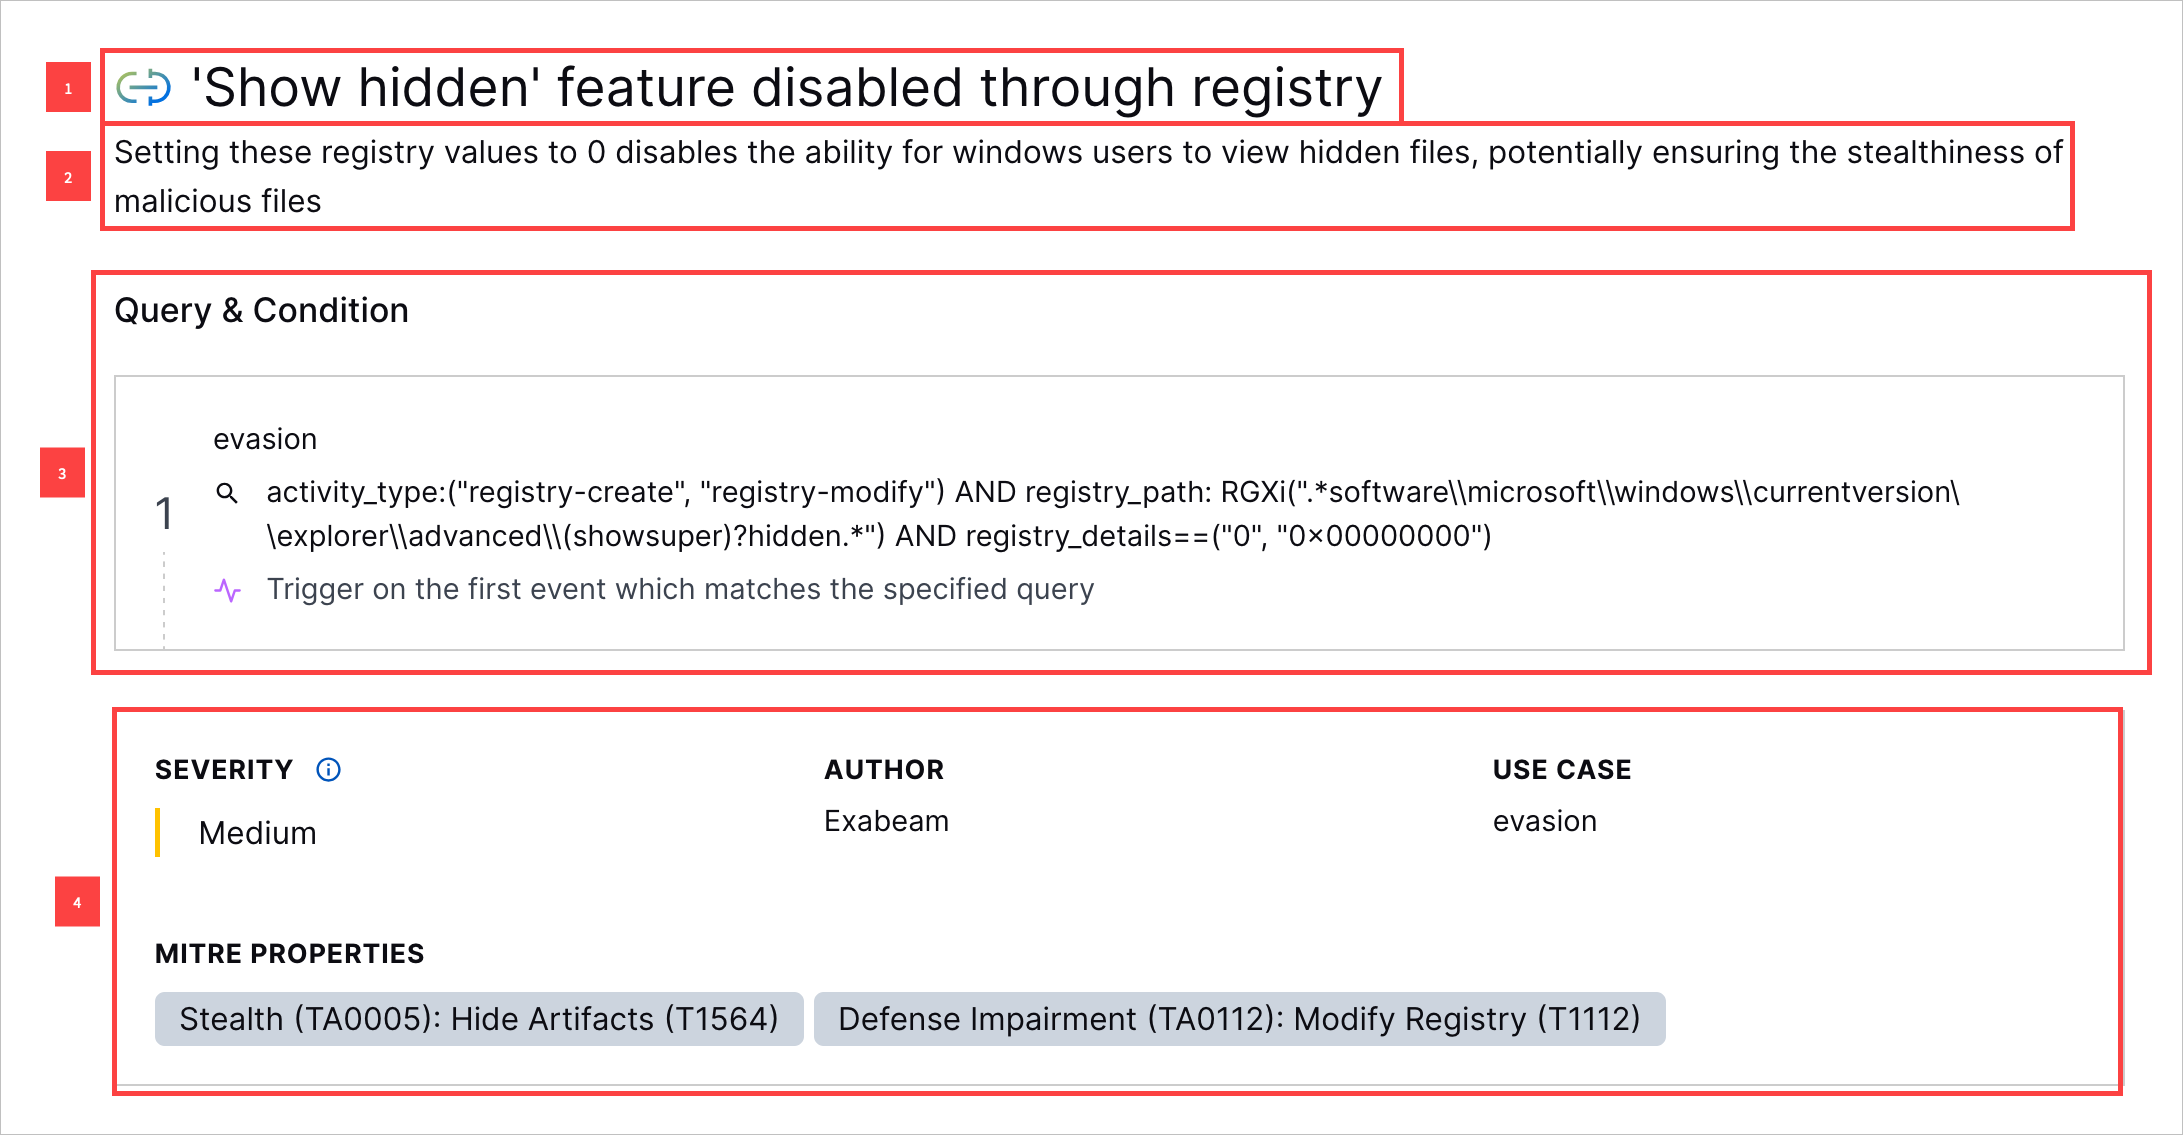
1 The correlation rule template name.
2 The correlation rule template description.
3 The sequences and conditions that must be satisfied for the correlation rule to trigger.
4 The correlation rule template severity, author, associated Exabeam use case, and associated MITRE ATT&CK® tactic and technique. Because it is a pre-configured template, the author is Exabeam.
Some correlation rule templates duplicate existing Advanced Analytics fact-based rules. Find the latest list of Correlation Rule templates in the CIM Library. When you use these templates to create a rule, it's best that you customize the rule. If you enable the rule as is, one event triggers two rules and results in two outcomes: one from Advanced Analytics and another from Correlation Rules.