- Site Collector Overview
- Get Started with Site Collectors
- Install Site Collector
- Set Up Collectors
- Sign Up for the Early Access Program: Site Collectors
- Choose the Right Collector based on Data Sources
- Set Up Archive Windows Collector
- Set Up Archive Linux Collector
- Set Up Direct Access Agent (DAA) Windows Event Log Collector
- Set Up EStreamer Collector
- Set Up Fortinet Collector
- Set Up IBM Security QRadar Collector
- Set Up Kafka Collector
- Set Up Splunk Collector
- Set Up Linux File Collector
- Set Up Microsoft SQL Collector
- Set Up MySQL Collector
- Set Up Oracle Collector
- Set Up Syslog Collector
- Set Up Windows Active Directory Collector
- Set Up Windows Event Log Collector
- Set Up Windows File Collector
- Manage Site Collectors
- Apply Antivirus Exclusions
- Migrate to the New-Scale Site Collectors Service
- Modify Collector Configuration
- Modify a Site Collector Instance
- Manage Templates
- Monitor Log Sources
- Add Filters to Set Egress Log Filtering Conditions
- New Site Collector Management Service NGSCD
- Regenerate Certificates for Collectors
- Automatic Renewal of Security Certificates
- Refresh Certificates via User Interface (Site Collector 2.3.0 or Later)
- Set Auto Certificate Refresh via Maintenance Window (Site Collector 2.22.0 or later)
- Generate TLS Certificate for Site Collector 2.2 and Later
- Generate TLS Certificate for Site Collector 2.16.0 and Later
- Regenerate Security Certificates Using CLI
- Recover Certificates
- Troubleshoot Common Issues
- Upgrade Site Collector
- Upgrade the Site Collector Specifications
- Universal Collector Management Framework
- Run Required Prechecks
- Manage Collectors using Site Collector User Interface
- Manage Collectors using Command Line
- Upgrade Collectors using Site Collector User Interface
- Upgrade Collectors using the Command Line
- Automatic Renewal of Security Certificates
- Manual Security Certificate Update
- Recover Certificates
- Vulnerability Remediation Policy
- Delete a Site Collector Instance
- Site Collector Monitoring
- Troubleshoot the Site Collector
- Pre-checks failed during Site Collector installation and upgrade
- Site Collector UI shows the status INSTALLATION_ERROR
- Download Support Packages for Troubleshooting
- How to reboot the Virtual Machine (VM) successfully to apply security updates?
- What information must be added while creating a support ticket to resolve an issue?
- Site Collector UI is not displaying the heartbeats
- Splunk Collector can't be set up
- Splunk Collector is set up however, logs are not reaching DL/AA
- Only a few of the installed Splunk Collectors are processing logs or EPS has dropped by 50% as compared to last hour
- The Windows Active Directory Collector (formerly known as LDAP Collector) is set up, however, the context data is not reaching DL/AA
- The Windows Active Directory Collector (formerly known as LDAP Collector) is stuck in the ‘Update’ mode after deployment
- Installation is initiated; however, the collector shows the status as ‘Setting Up’ for some time
- Data Lake and Advanced Analytics Does Not Show Context Data
- Context Data from Windows Active Directory Collector is Segmented
- Minifi Permission Denied - Logback.xml File Missing and Config File Update - Failed Error Occurred while Installing the Windows Event Log Collector
- Where should I upload proxy certificates if I am running proxy with TLS interception?
- How to upgrade Linux collector instance?
Regenerate Certificates for Collectors
Site Collector Core (NiFi) secures its communication using TLS certificates—a CA Certificate and a Server Certificate. The CA Certificate is valid for 10 years. A Server Certificate lasts for 100 days in SC version 2.16.0 or later and two years in earlier versions. If the server certificate expires, all TLS-enabled collectors—including Windows Event Log Collector, File Collector, Archive Collector, Linux collector, Syslog, and Fortinet collectors—fail TLS verification and immediately stop sending data.
Refer to the following recommendations about the method of regenerating certificates for specific Site Collector versions.
Site Collector Version | Recommendations |
|---|---|
Site Collector 2.16.0 – 2.21.x | Refresh certificates via user interface, or use the |
Prior to Site Collector version 2.2 | Use legacy script only. |
Site Collector 2.22.0 or later | Refresh certificates via user interface, or maintenance window. |
Site Collector 2.3.0 – 2.15.x (2.3 or later) | Refresh certificates via user interface, or use manual CLI steps as a fallback option. |
Note
If you upgraded from a version older than 2.16.0, the user interface (UI) shows the old two-year expiry until you regenerate the certificates. To switch to the 100-day security policy, regenerate your security certificate using the user interface (UI) as a recommended option or using CLI as a backup—a secondary option.
When troubleshooting on disk within the /opt/exabeam/auth/ssl/ngsc/ directory, refer to
ca.pemas the CA certificate andcert.pemas the server certificate that agent collectors validate against.Ensure that you upgrade the agent collectors to the latest supported version before updating the certificates.
Automatic Renewal of Security Certificates
Collectors use digital security certificates to create safe and encrypted connections with Site Collector. These certificates are subject to expiration and require periodic renewal. Collector security certificates are issued and managed by Site Collector, not by individual collectors. Renewals are performed on the Site Collector via Certificate Rotation on the New-Scale Security Operations Platform or by a Site Collector administrator.
Once the Site Collector acquires new certificates, each individual collector updates automatically by having its management agent check the certificate status every six hours. If the certificates are within seven days of expiration, or have expired, or if the certificate authority changes, the agent automatically downloads the current certificates. The agent then installs these certificates, performs a brief collector restart, and restores the previous certificates automatically if the new ones fail validation. Finally, if the Site Collector is unreachable or has not been renewed, the collector continues to operate with its existing certificates and retries the update periodically.
Refresh Certificates via User Interface (Site Collector 2.3.0 or Later)
The Site Collector version 2.3 enables you to start an automated process for updating the security certificates, hence upgrade the Site Collector instance to version 2.3 or later.
It is recommended to upgrade Windows Event Log Collector, Windows File Collector, and the Windows Archive Collector to version 2.3 or later before starting with the certificate refresh process.
Use the following steps to start the certificate refresh process.
Log in to the New-Scale Security Operations Platform with your registered credentials.
Navigate to Collectors > Site Collectors.
Ensure that Site Collector is installed and in running state.
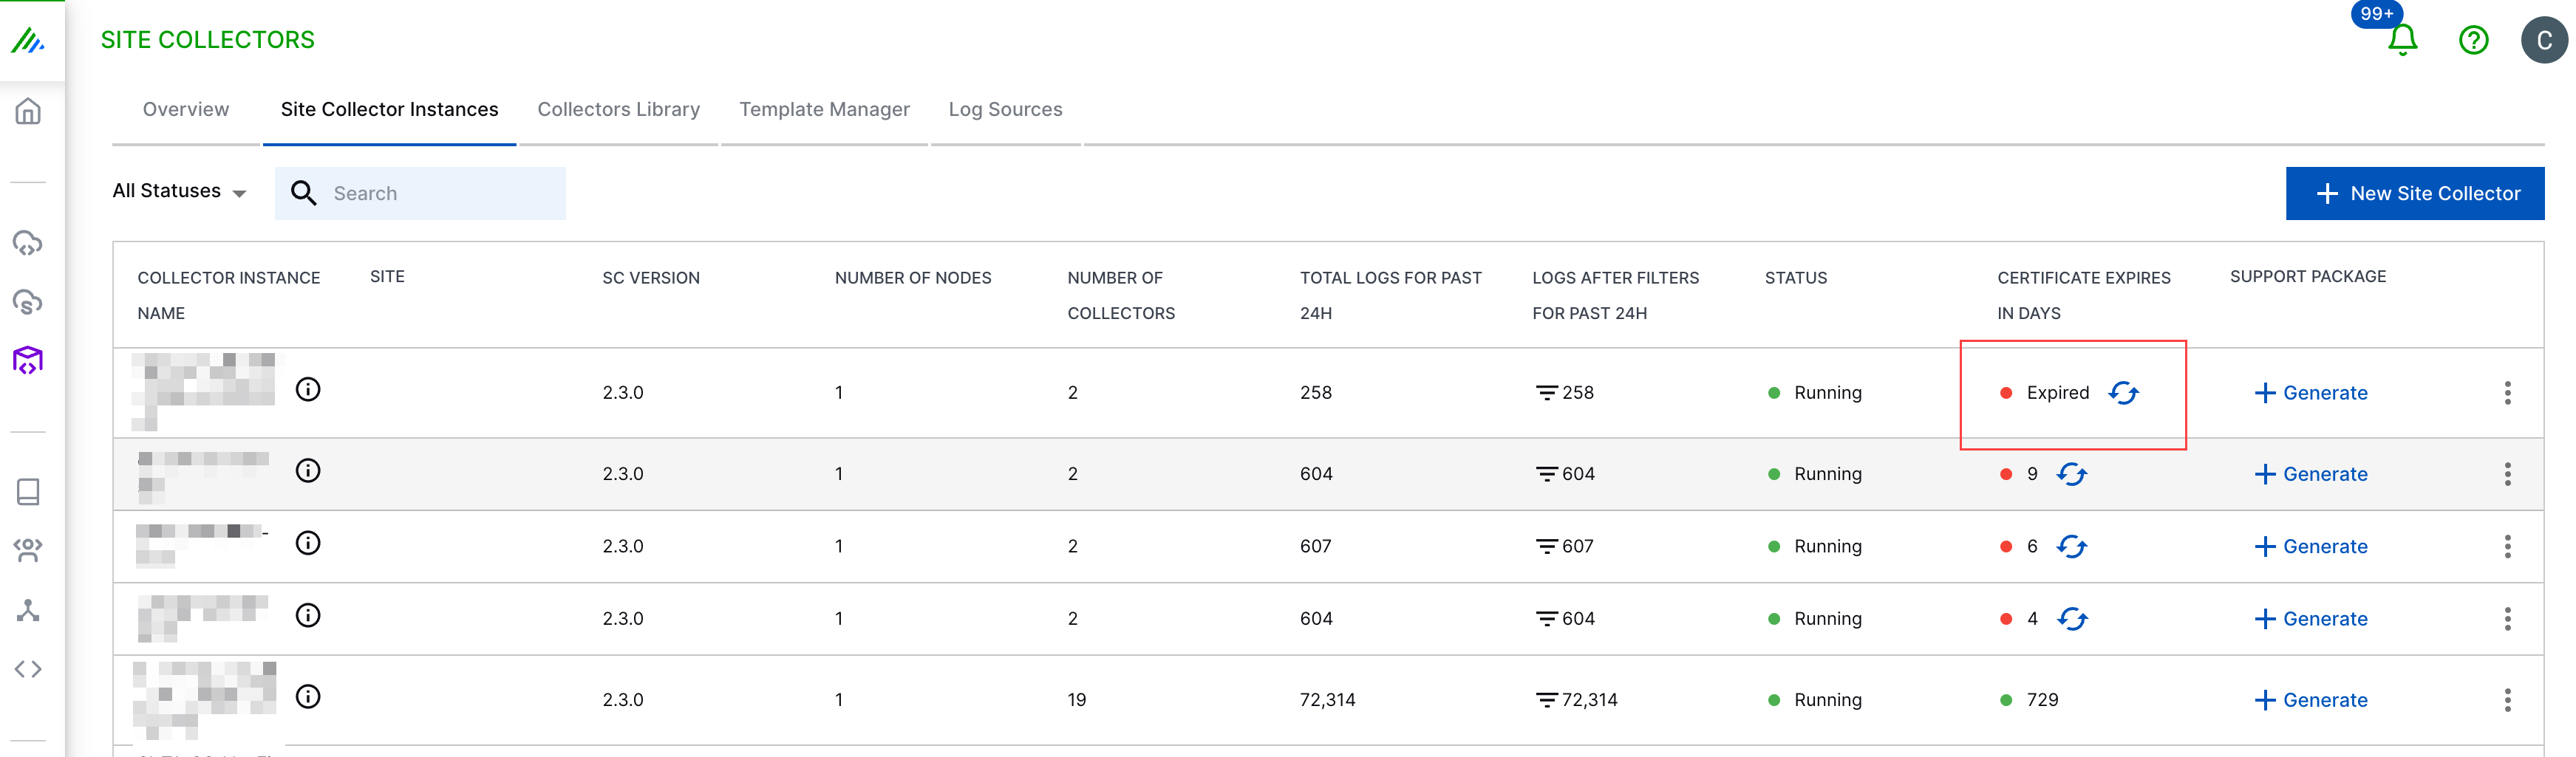
On the Site Collector page, click the Site Collector Instances tab.
In the CERTIFICATE EXPIRES IN DAYS column, click the refresh (↻) button.
Note
The CERTIFICATE EXPIRES IN DAYS column displays the server certificate expiry not the CA certificate expiry in days.
In the confirmation message window, click Confirm.
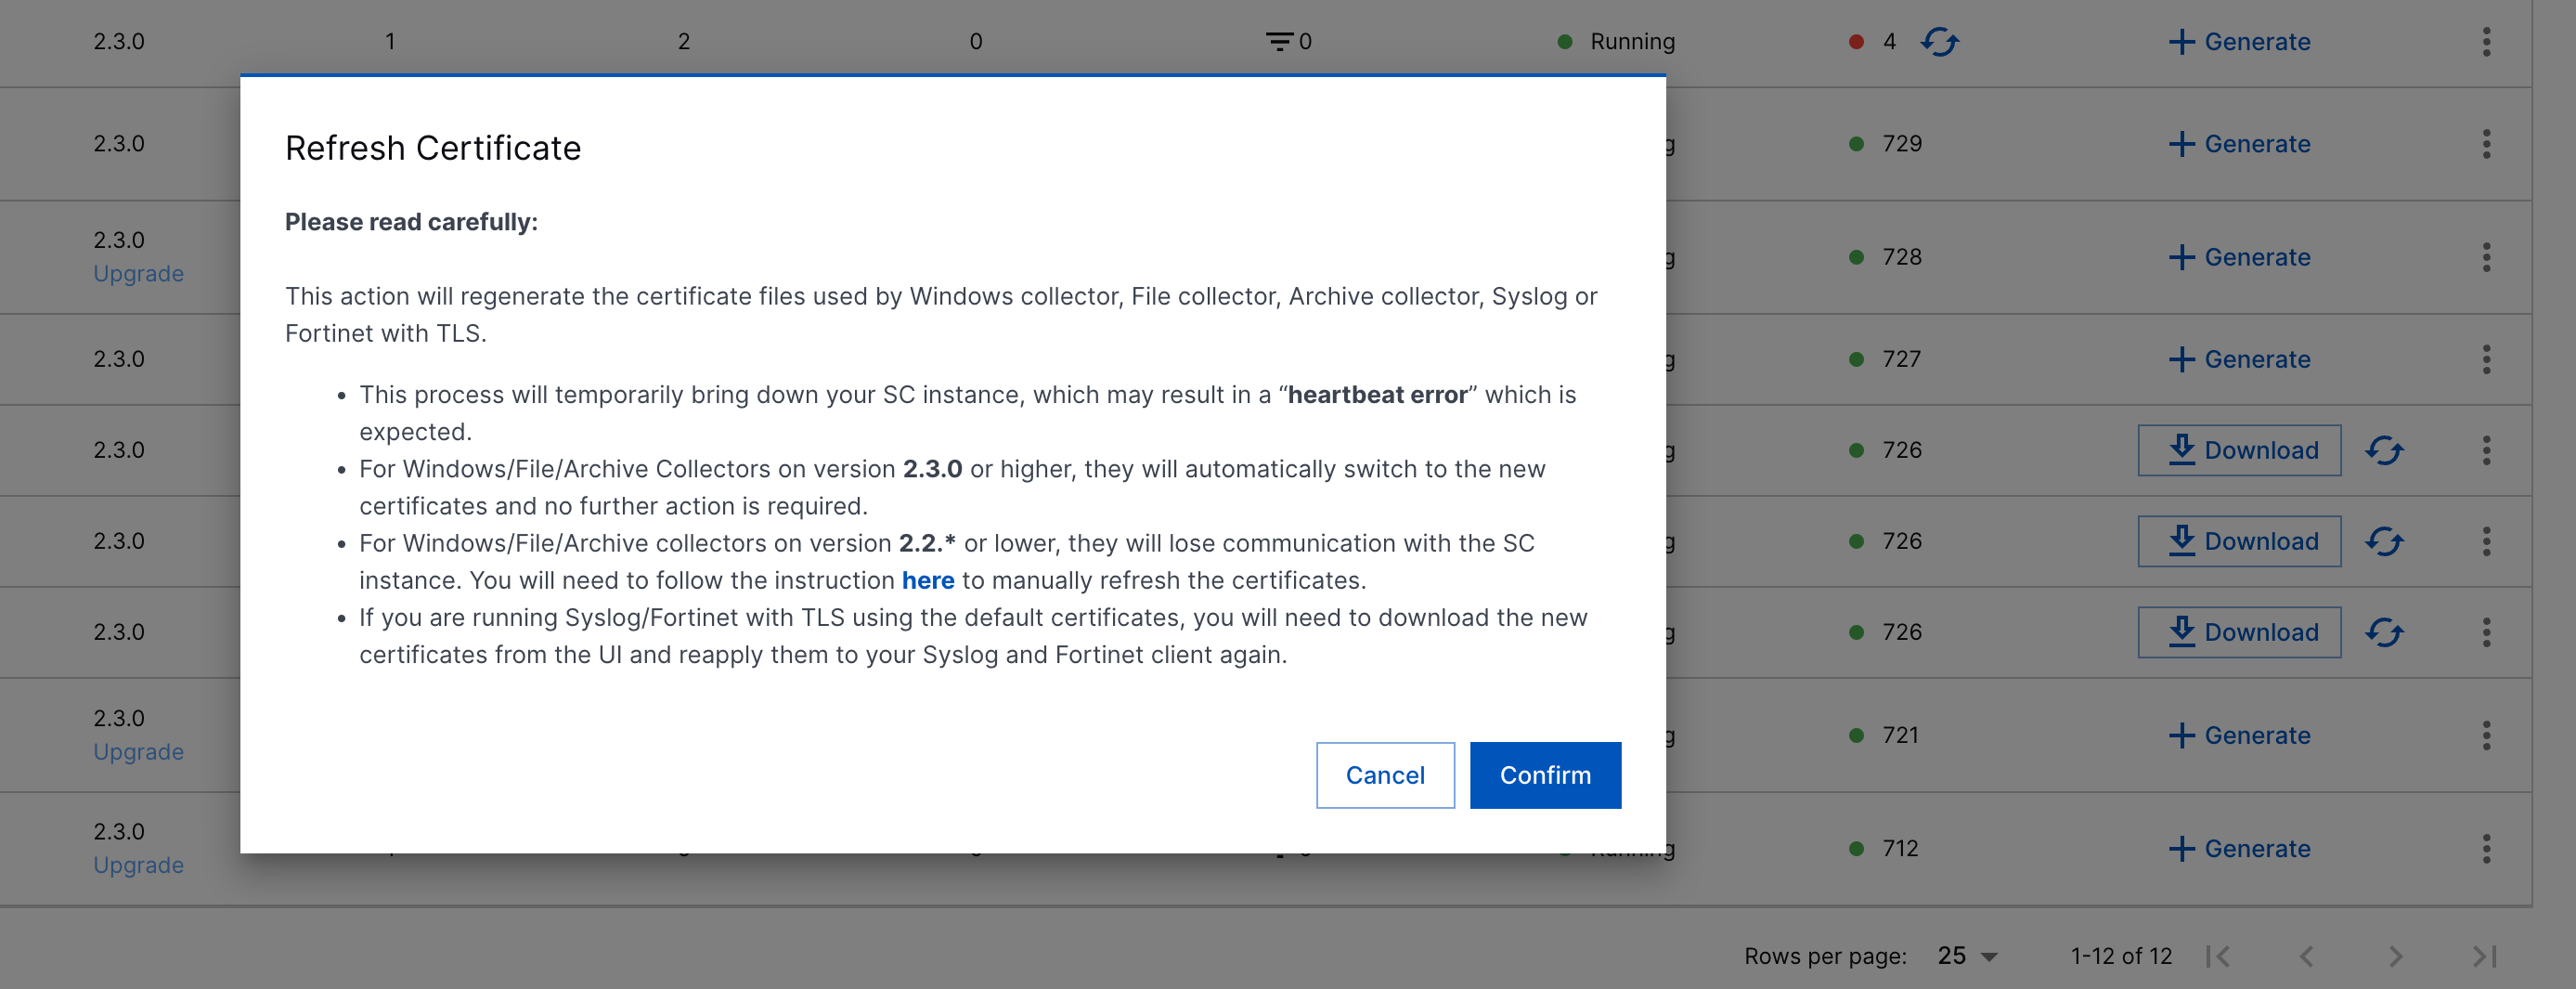
The Site Collector instance generates new security certificates. This may affect the performance and pause the data flow until new certificates are added to the Site Collector's trust store and the Site Collector instance is restarted.
After you click Confirm:
For Site Collector 2.16.0 or later, all Windows and Linux agent collectors automatically detect and apply the new certificate. No further action is required.
For Site Collector 2.15.x or earlier, agent collectors must be updated manually.
For Syslog with TLS / Fortinet with TLS, the certificate refreshes automatically for Site Collectors. However, the new certificate must be manually downloaded and uploaded to the external Syslog/Fortinet server.
For Site Collector 2.18.0 or later, the certificate can be refreshed at any time — there is no minimum expiry window restriction.
For Windows Event Log Collector, Windows File Collector, and Windows Archive Collector instances on Site Collectors 2.12.0 or later, new security certificates are automatically downloaded and applied without any need for user action. For Site Collectors 2.3–2.11.x, agent collectors still require the manual PowerShell script.
The collector instance may show a heartbeat error during the automatic certificate generation process. For the Windows collector instances that are configured on the previous versions of Site Collector such as version 2.2 and earlier, refresh the security certificates using the following command.
powershell.exe -NoLogo -ExecutionPolicy Bypass -Command "Invoke-WebRequest -OutFile 'windows_certificates_update.ps1' -Uri 'http://<SiteCollectorIP>:9875/?filename=windows_certificates_update.ps1'; .\windows_certificates_update.ps1 <SiteCollectorIP> -force"
Note
For Syslog collector with TLS and for the Fortinet collector with TLS, the security certificates are updated when you start with the automatic certificate refresh via the user interface. Edit the configuration for the collector instance and click Download Certificate. Then upload this downloaded certificate to the Syslog or Fortinet server.
Set Auto Certificate Refresh via Maintenance Window (Site Collector 2.22.0 or later)
If you use the Site Collector version 2.2, use the following steps to set auto certificate refresh. Ensure that Site Collector instance status is 'Running'.
Navigate to Collectors > Site Collectors.
On the Site Collector page, click the Site Collector Instances tab.
Click more options (⋮).
Click Maintenance settings.
Configure the schedule — select options Daily, Weekly, Monthly, or Quarterly — and set the start time and the timezone.
Enable the Auto Certificate Refresh option.
Click Save.
Site Collector checks if the certificate is due for rotation within the configured window and rotates it automatically.
Generate TLS Certificate for Site Collector 2.2 and Later
If you use the Site Collector version 2.2, use the following steps to regenerate TLS certificates.
Generate CA Certificate and Server Certificate
To regenerate new certificates for Site Collector and upload the certificates to the Exabeam cloud, use the following steps.
Stop the Site Collector service.
sudo ./ngsccli sitecollector stop
Run the following command to regenerate the certificate.
sudo ./ngsccli certificate regenerate
The existing TLS certificates that Site Collector Core (NiFi) uses to receive data are replaced with the latest certificates.
Start the Site Collector service.
sudo ./ngsccli sitecollector start
Update the all the existing collectors that use certificates to send data.
Note
Ensure that you use the correct commands relevant for the Site Collector version.
Site Collector 2.16.0+: Use the command
certificate orchestrate.Site Collector 2.2 – 2.15.x: Use the flow Stop Site Collector service → regenerate certificates → Start the Site Collector service along with manual hardening.
Generate Server Certificate Only
If you have installed Site Collectors version 2.2 and want to retain the existing CA certificate, and generate only the server certificate, set the --newca flag to false. Refer to the following command.
sudo ./ngsccli certificate regenerate --newca=false
If you want to check the expiration of an existing CA certificate:
Check if the
ca.pemfile is available in /opt/exabeam/auth/ssl/ngsc/.If the
ca.pemfile is not available, it indicates that the Site Collector version is prior to version 2.2 and you must regenerate the CA certificate.To check the expiration of the CA certificate, use the following openssl command.
openssl x509 -in ca.pem -text -noout | grep "Not After"
Set Custom Expiration
The default expiration depends on the Site Collector version. The default expiration for Site Collector 2.16.0 and later for server certificate is 100 days and for CA certificate is 10 years. For the Site Collector versions before 2.16.0, the expiration for server certificate is 2 years. To set custom expiration, use --ca-expiration flag to set certificate expiry in years and --cert-expiration flag to set certificate expiry in days.
Upload Certificates
If the automatic upload of certificates to the Exabeam cloud fails, to manually upload the certificates use the following command.
sudo ./ngsccli certificate upload
Generate TLS Certificate for Site Collector 2.16.0 and Later
Use the following CLI to stop, regenerate, and restart, and automatically disable hardening for 24 hours for agent collectors to pull the new certificate.
sudo ./ngsccli certificate orchestrate
Regenerate Security Certificates Using CLI
Site Collector Core (Nifi) generates security certificates for secure communication. When security certificates expire, all connected agent collectors including Windows Event Log Collector, File, and other log forwarders will fail TLS verification and cease communication with the Site Collector.
To avoid disrupting collector operation, refresh the SSL/TLS certificates by using the following steps.
Note
Always regenerate certificates using the user interface (UI); use the command-line interface (CLI) only as a backup—a secondary option.
Always run
ngscclifrom/opt/exabeam/bin. Never use a binary from the home directory (~/ngsccli) or any other path. Old binaries generate certificates with incorrect validity periods such as two years instead of 100 days.
Upgrade the Site Collector version to 1.19.2 or later.
You can update the Windows certificate for Site Collector version 1.19.1 and later and the Linux certificate for Site Collector version 1.19.2 and later.
Log in to the VM on which Site Collector is installed and use the following command to generate new SSL certificates for Site Collector versions before Site Collector 2.2.
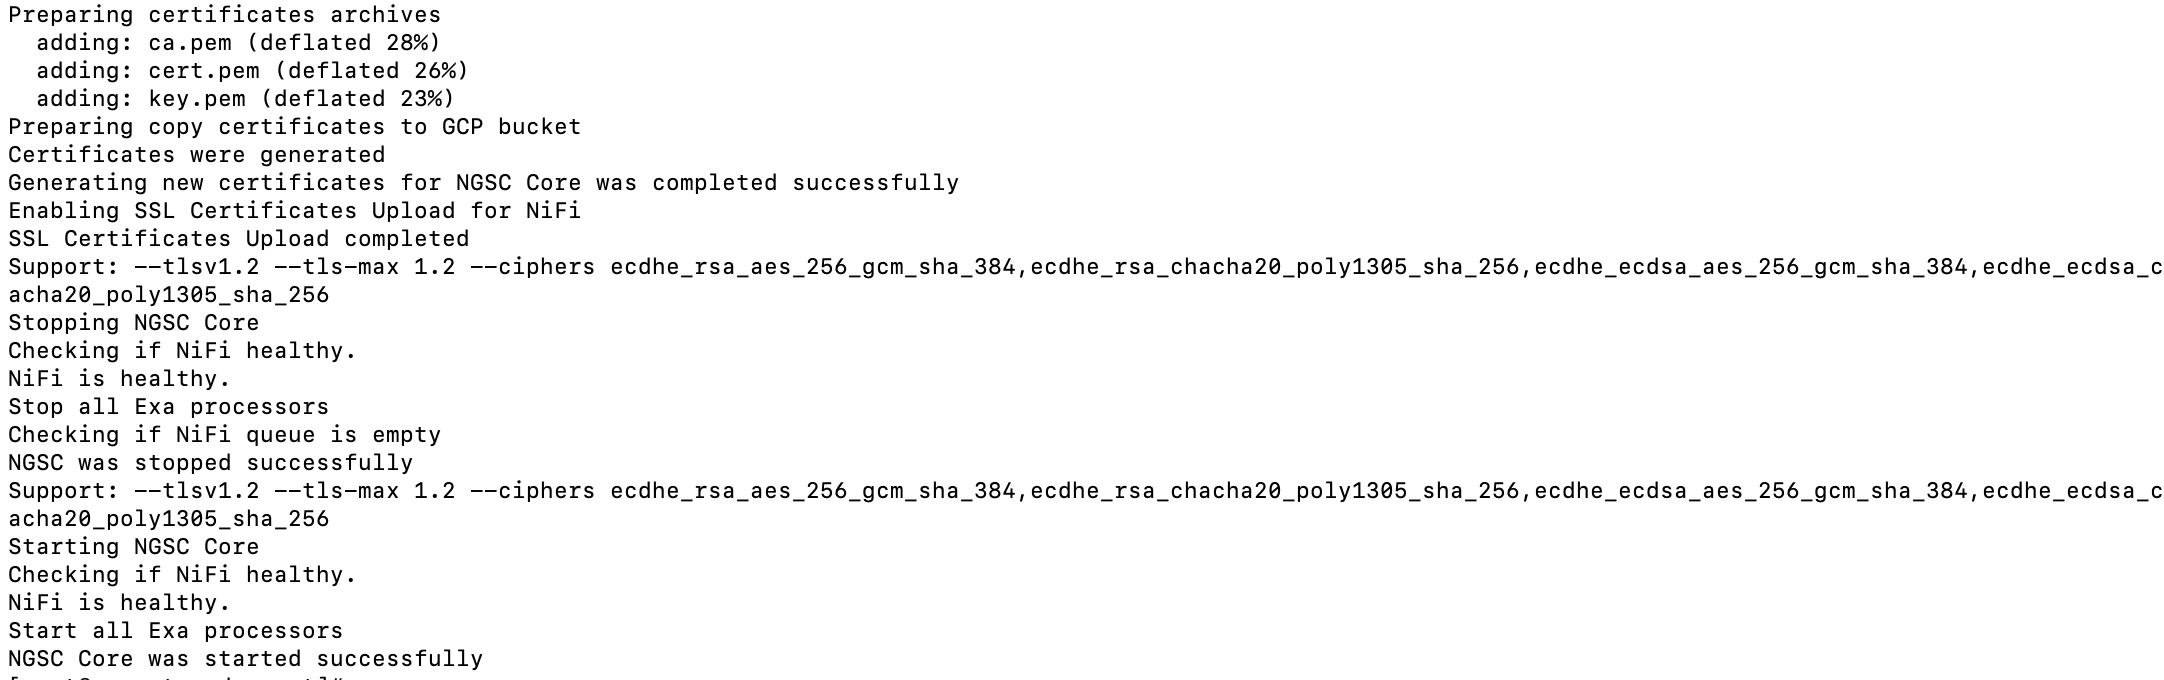
sudo /opt/exabeam/nifi/nifi_scripts/regenerate_certificate.sh
Refer to the following screenshot as an example of how the output may look like.
If you are using Site Collector version 2.2 and later, use the steps mentioned in the Generate TLS Certificate section to refresh the security certificates.
To refresh certificates to resume communication with Site Collector Core (Nifi), for Windows collectors including Windows Event Log collector, Windows File collector, and Windows Archive collector, run the following command in PowerShell on the Windows VM on which the collector is installed.
Note
You must be an administrator to run the command.
powershell.exe -NoLogo -ExecutionPolicy Bypass -Command "Invoke-WebRequest -OutFile 'windows_certificates_update.ps1' -Uri 'http://<SiteCollectorIP>:9875/?filename=windows_certificates_update.ps1'; .\windows_certificates_update.ps1 <SiteCollectorIP> -force"
Replace <SiteCollectorIP> with the private IP of the VM on which the Site Collector is installed.
Refer to the following screenshot as an example of how the output may look like to indicate that certificate update is successful.
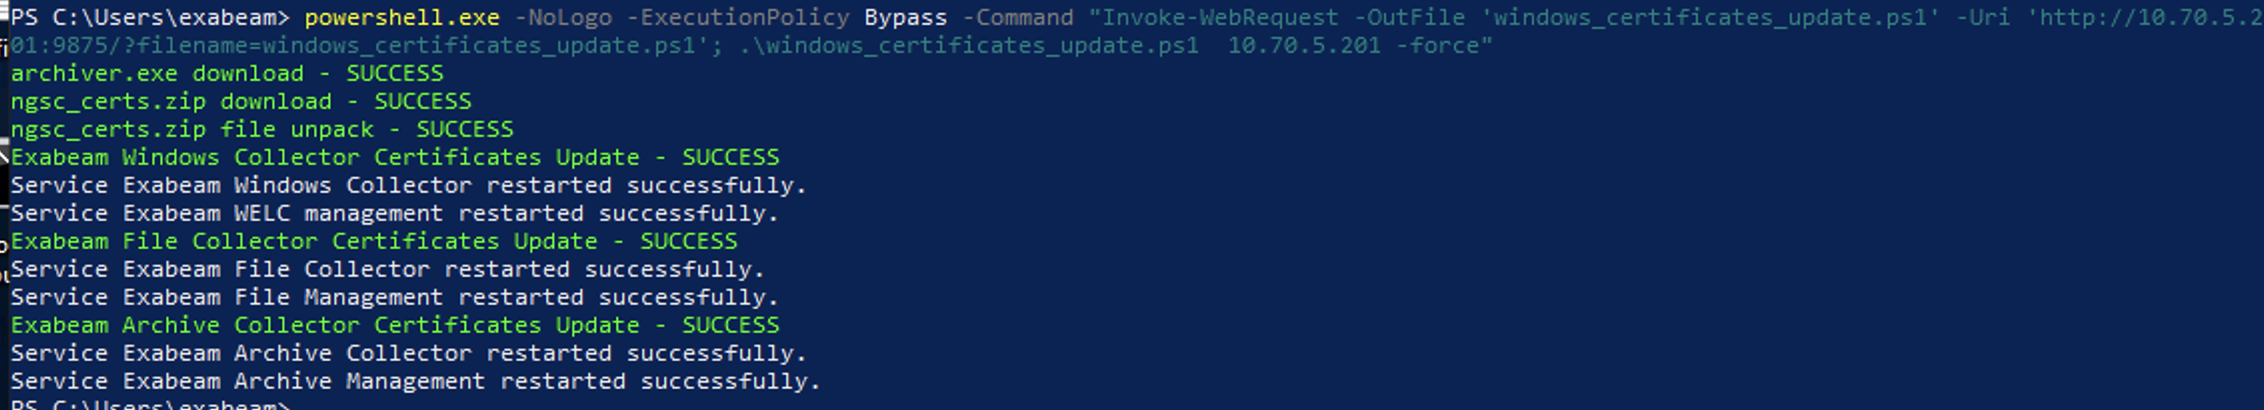
If the above script does not download the certificates directly from the Site Collector instance, download the certificates directly from the user interface and copy them to the Windows server. Then, run the following script in the directory in which the certificates are placed.
powershell.exe -NoLogo -ExecutionPolicy Bypass -Command "Invoke-WebRequest -OutFile 'windows_certificates_update.ps1' -Uri 'http://<SiteCollectorIP>:9875/?filename=windows_certificates_update.ps1'; .\windows_certificates_update.ps1 <SiteCollectorIP> -force"
Replace <SiteCollectorIP> with the private IP of the VM on which the Site Collector is installed.
For the Linux based collectors such as, Linux File collector and Linux Archive collector, run the following command on the Linux machine on which collector is installed.
sudo -- sh -c 'curl -o linux_certifcates_update.sh http://<SiteCollectorIP>:9875/?filename=linux_certifcates_update.sh; chmod +x linux_certifcates_update.sh | bash -s; ./linux_certifcates_update.sh <SiteCollectorIP>'
Replace <SiteCollectorIP> with the private IP of the VM on which the Site Collector is installed.
Refer to the following recommendation for upgrades and certificate rotation.
Action
Recommendation
Site Collector Upgrade
Upgrade using the Site Collector user interface (UI).
Certificate Rotation
Initiate certificate rotation using the Site Collector user interface (UI).
CLI Upgrade (if required)
Download the latest ngsccli before running any upgrade command.
CLI Certificate Rotation (fallback option only)
Use
sudo ./ngsccli certificate orchestratefrom/opt/exabeam/bin.Never use a CLI binary from the home directory or any other location.
Generate Certificates for Older Versions of Site Collector
Refer to the following table for information about CLI commands recommended for each of the old Site Collector versions.
Site Collector Version | CLI Command |
|---|---|
Site Collector 2.16.0 or later | cd /opt/exabeam/bin sudo ./ngsccli certificate orchestrate This command checks CA and server certificate expiry dates, stops Site Collector Core, regenerates certificates, and restarts Site Collector Core. This command also disables hardening for 24 hours so that the agent collectors can pull the new certificate. |
Site Collector 2.2.0 – 2.15.x | cd /opt/exabeam/bin sudo ./ngsccli sitecollector stop sudo ./ngsccli certificate regenerate sudo ./ngsccli sitecollector start After Site Collector core backup is completed, use the following command to temporarily disable hardening for the agents to download the new certificate. sudo /opt/exabeam/bin/ngsccli sitecollector harden --off After all agent collectors display Running status, re-enable hardening using the following command. sudo /opt/exabeam/bin/ngsccli sitecollector harden Do not leave hardening disabled permanently. Re-enable hardening manually with The 24-hour automatic re-enable safety net only applies to the certificate orchestrate workflow for Site Collector 2.16.0+. If you disable hardening and forget to re-enable it, it will stay disabled indefinitely. Ensure that you re-enable hardening using the |
Before Site Collector 2.2 (legacy script) | sudo /opt/exabeam/nifi/nifi_scripts/regenerate_certificate.sh |
Update Security Certificates for Agent Collectors
Refer to the following table for information about steps recommended for agents on various Site Collector versions.
Site Collector Version | Steps to Update Security Certificates for Agent Collectors |
|---|---|
Site Collector 2.16.0 or later | No action is required. All agent collectors automatically detect the updated server certificate and apply it without a restart. |
Site Collector 2.15.x or earlier | After regenerating the Site Collector certificate, update each agent type manually on the agent host.
|
Recover Certificates
The primary and recommended method for certificate recovery is through the user interface. Use the following method only as a fallback option.
The collcli certupdate command retrieves and installs the latest certificates from the Site Collector. This command is aimed at certificate-specific recovery and not at a comprehensive installation validation.
Following are some examples of the collcli certupdate command usage.
# Update certificates for a single collector
collcli certupdate --collector-type lfc

# Update certificates for all installed collectors on a host
collcli certupdate --all

# Force retrieval of a fresh certificate bundle
collcli certupdate --collector-type lfc --refetch-certs
Use the collcli certupdate command in case of the following scenario.
Expired certificates: Run the certupdate command if communication fails due to expired collector certificates.
Certificate validation errors: Use certupdate for errors such as certificate expired, x509: certificate signed by unknown authority, or TLS handshake failed.
Use the collcli certupdate command to complete the following tasks.
Download the latest certificate bundle from the Site Collector
Validate the certificate bundle prior to installation
Back up existing certificates
Install the new certificates
Restart required services
Verify connectivity using the new certificates
Restore previous certificates if validation fails
Troubleshoot Common Issues
Scenario 1: If the regenerate_certificate script at /opt/exabeam/nifi/nifi_scripts/regenerate_certificate.sh fails because of incompatibility of specific CURL versions with Site Collector Core (Nifi) API, modify the script on your VM by updating the generate_nifi_token() function as follows.
generate_nifi_token() {
  NIFI_WEB_UI_TOKEN=$(curl --silent $TLS_FLAG $CIPHERS_FLAG $CURVES_FLAG --fail -XPOST -k "$NIFI_API/access/token" -H "Content-Type: application/x-www-form-urlencoded" -d "username=$SINGLE_USER_CREDENTIALS_USERNAME&password=$SINGLE_USER_CREDENTIALS_PASSWORD" 2>&1)
  NIFI_VERSION="2.0.0-SNAPSHOT"

  return 0
}
Save the changes to generate and upload a new certificate, then restart your Site Collector instance.
Scenario 2: The regenerate_certificate.sh restarts Site Collector core. However if the certificate is already expired, restarting Site Collector core fails. In this case, restart the Nifi service using systemctl restart exabeam-ngsc.