Fact-PCwmic-SCD – The WMIC (WMI Command Line) process has been used to delete a shadow copy. This sigma rule is authored by Florian Roth (Nextron Systems), Michael Haag, Teymur Kheirkhabarov, Daniil Yugoslavskiy, oscd.community, Andreas Hunkeler (@Karneades) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_shadow_copies_deletion.yml
NumCP-VPNlnF-EC-U-30Days – An abnormal number of vpn login failures have been observed for this user in 30 days.
Fact-PCrundll32-PwrshellDll-PCL – rundll32.exe to execute PowerShell related code through DLL loading techniques. This sigma rule is authored by Markus Neis, Nasreddine Bencherchali (Nextron Systems). The content of this repository is released under the [Detection Rule License (DRL) 1.1](https://github.com/SigmaHQ/Detection-Rule-License). Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_powershell_execution_via_dll.yml
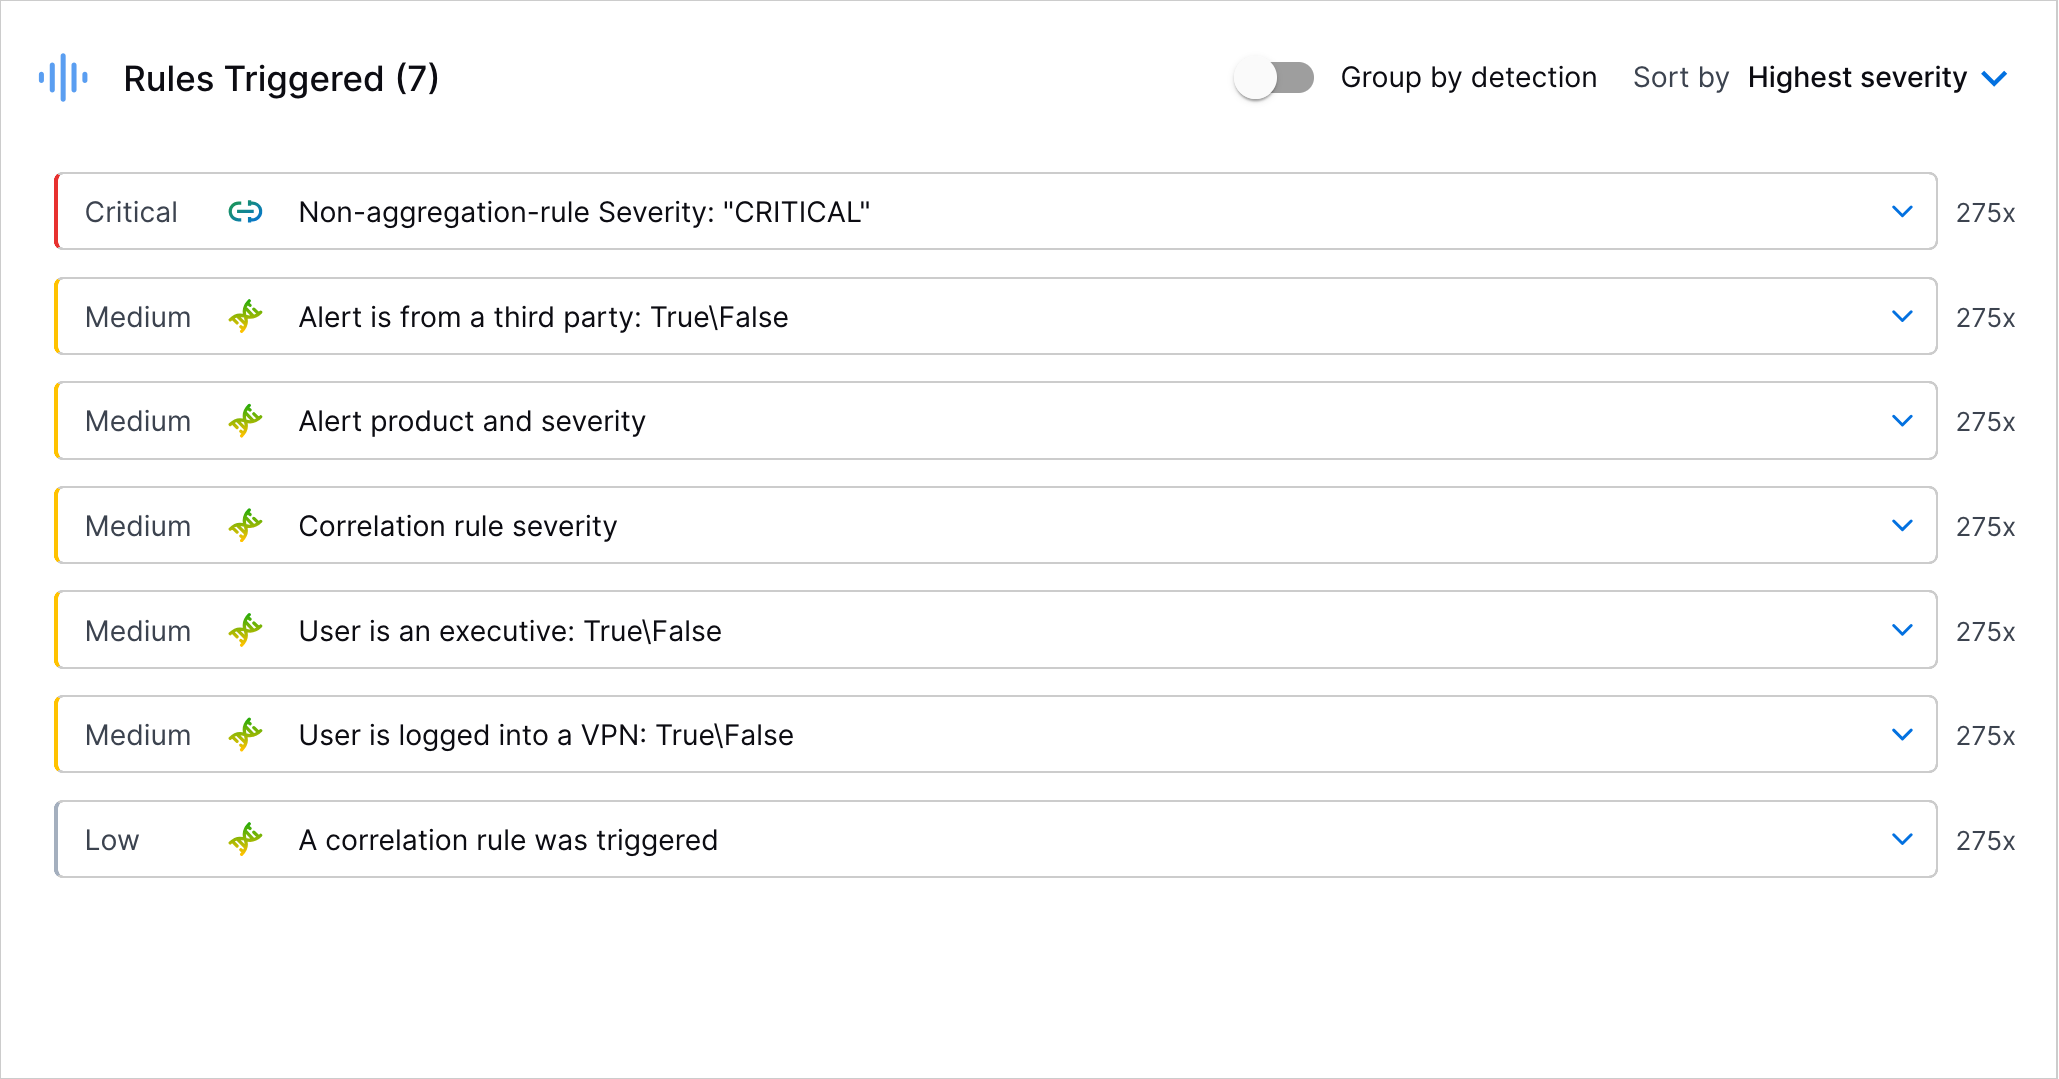
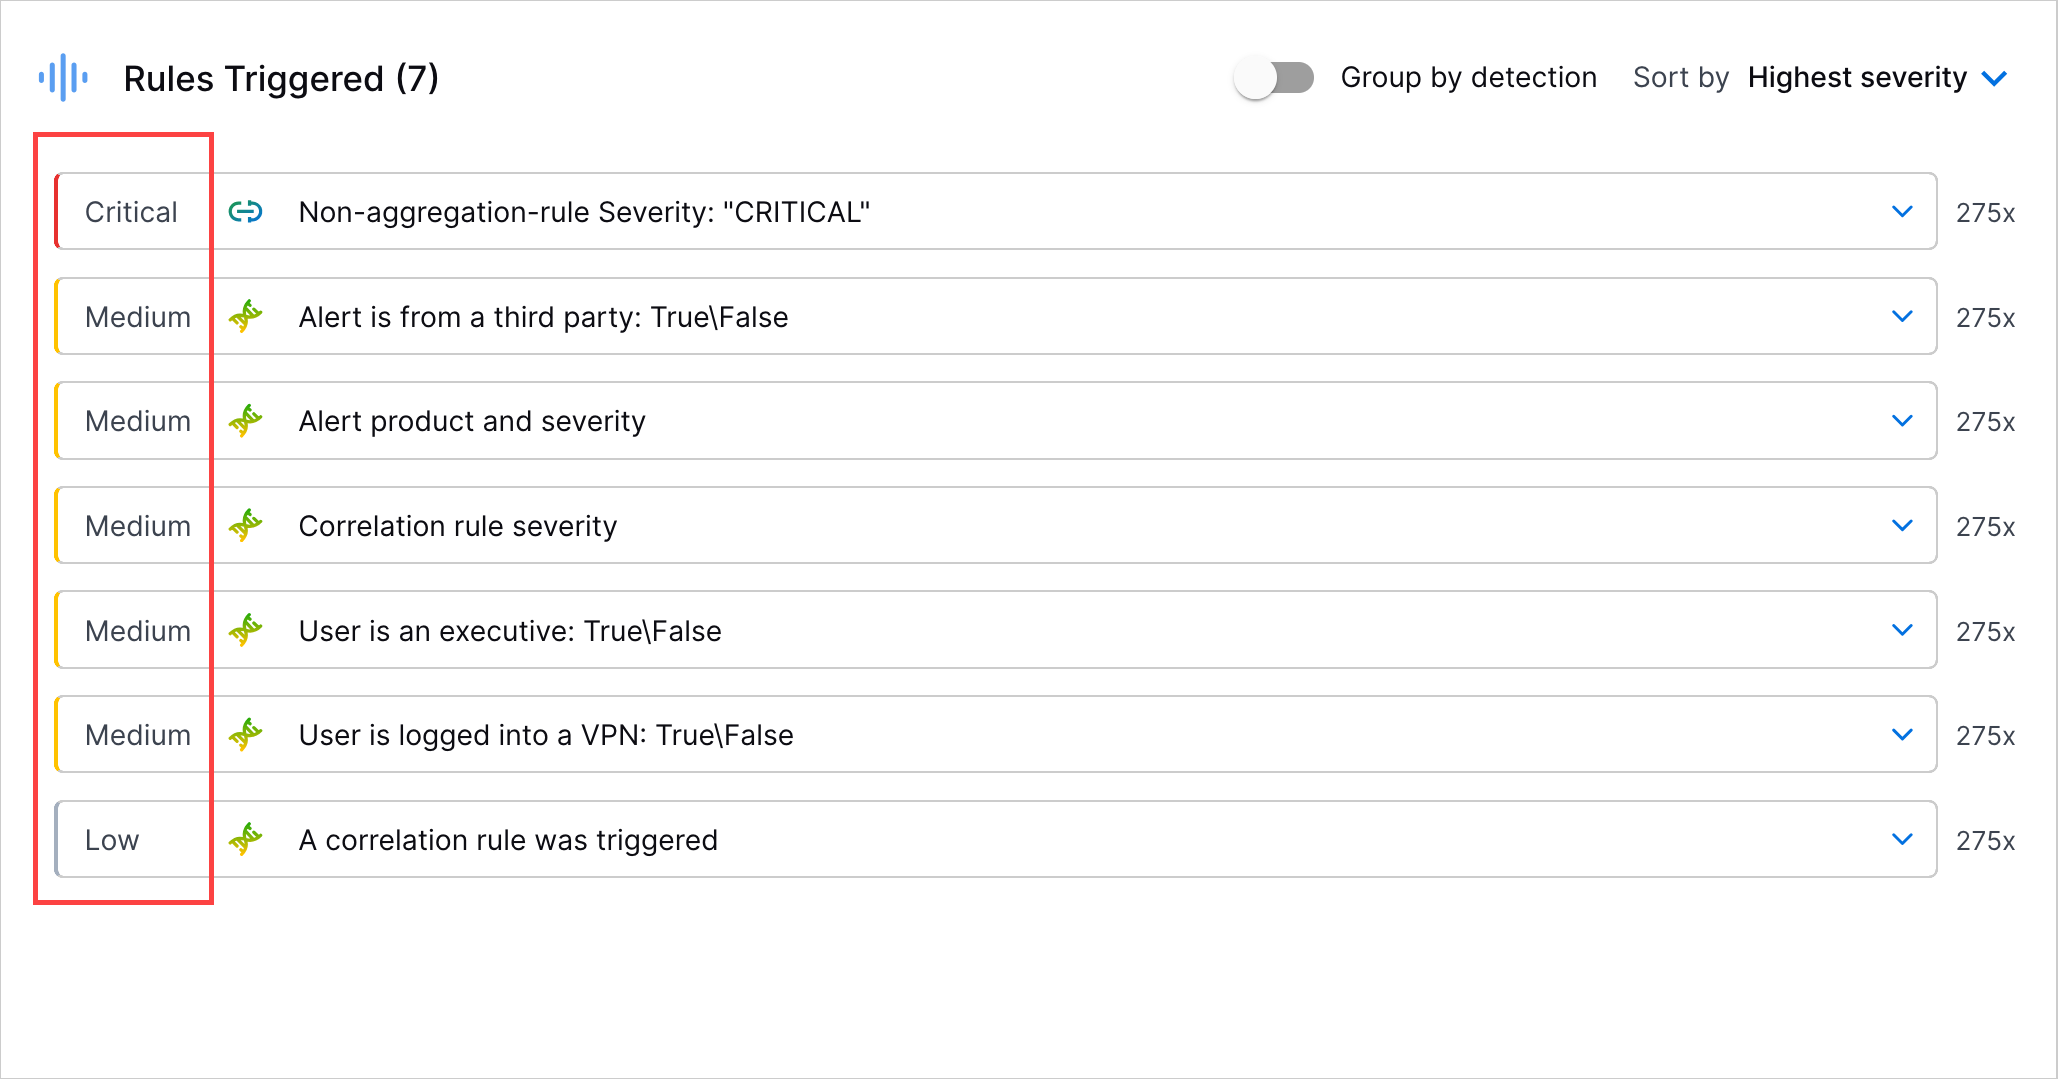
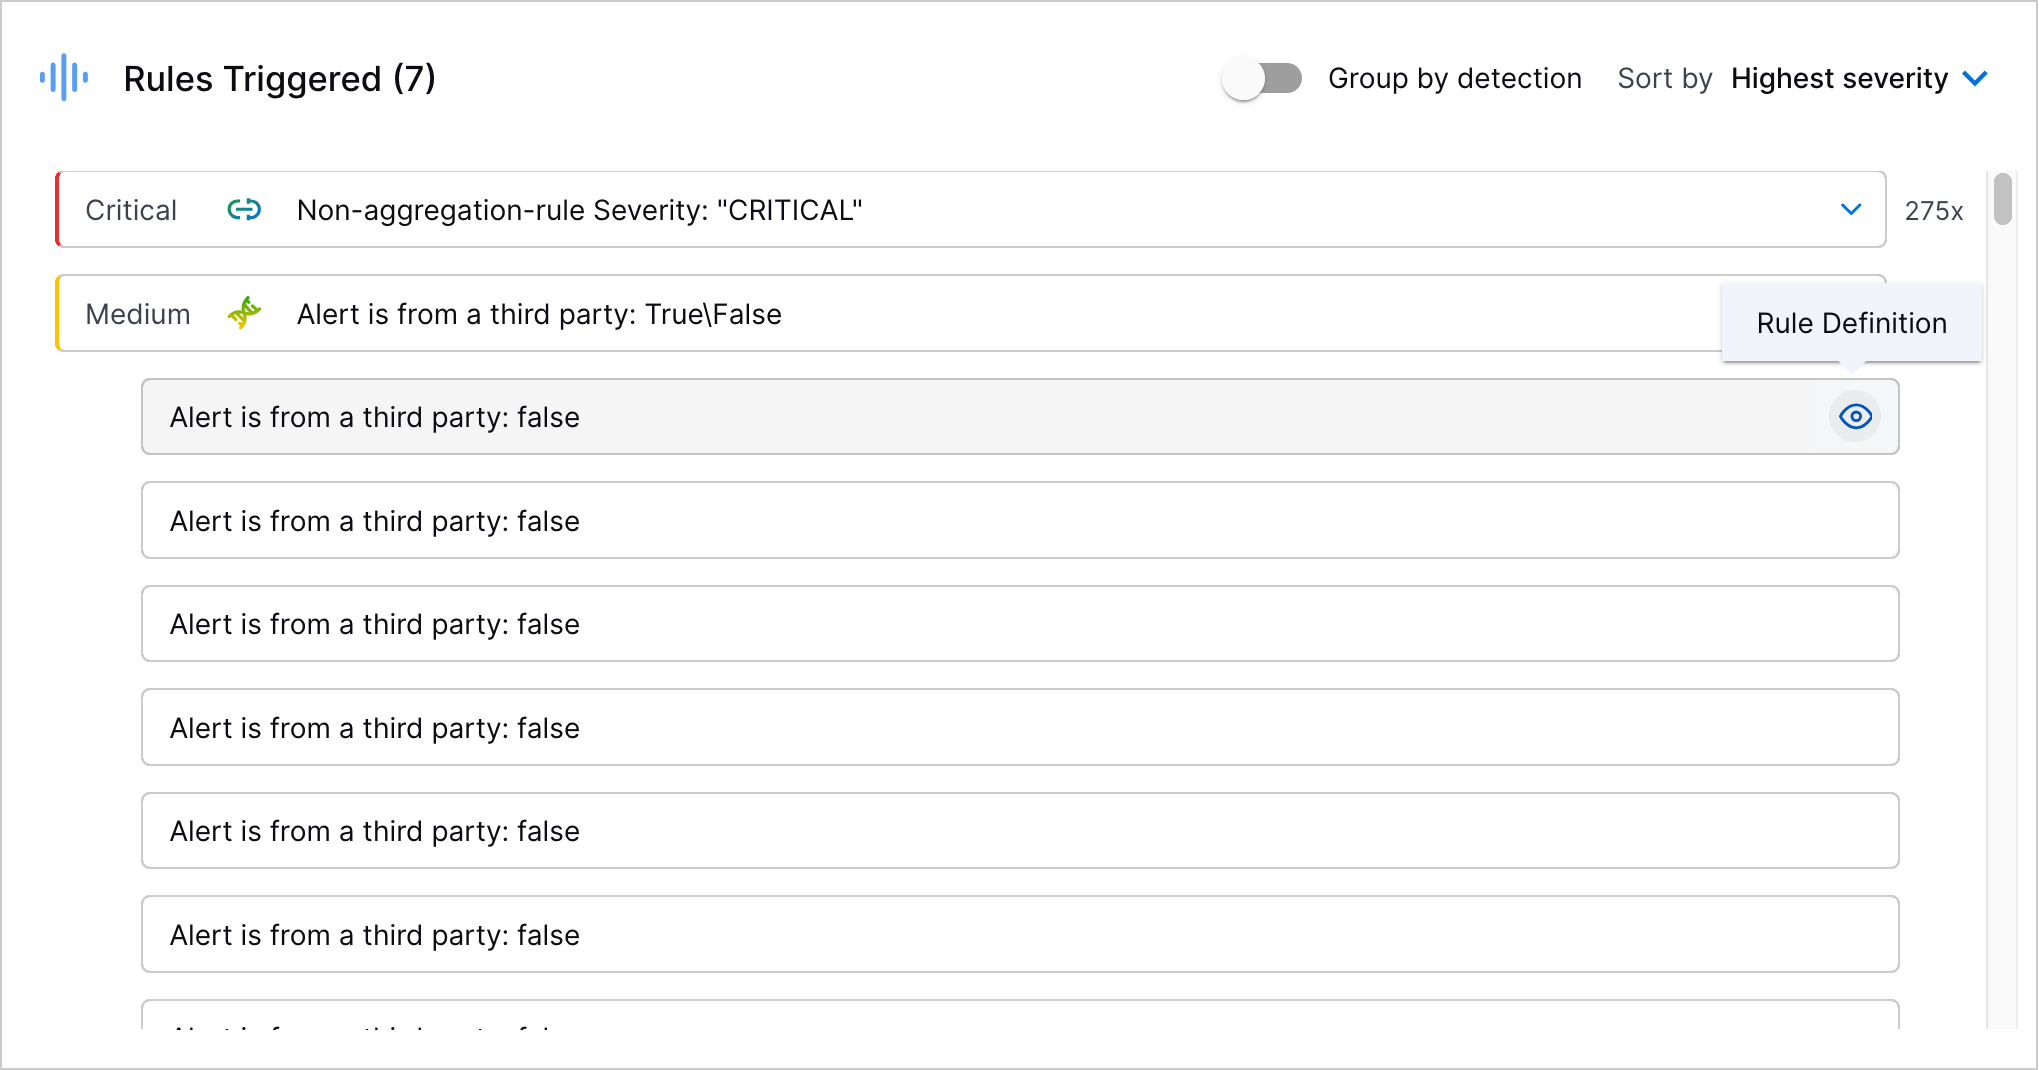
Cntx-Web-UCrit-Exec – User is an executive: True\False
Fact-GA-TITOR – An IP address associated with TOR has been observed.
NumDCP-Login-DZC-UD-DZ – An abnormal number of unique destination network zones have been observed in login events for users in this department. These events may include both failed and successful logins.
Prof-Web-TI-U-WebDom-Malicious – This is the first time an HTTP communication attempt to this malicious web domain has been observed for this user. These events may include both failed and successful traffic.
Fact-SEPwrshell-EnumNetworkAdapter – A PowerShell script that enumerate network adapters using wmi object has been executed.
Fact-PC-OpenClawInstall – OpenClaw has been installed using the command line tool 'curl'. There is nothing inherently malicious about OpenClaw, however, by default it uses insecure practices and may expose significant security flaws.
Prof-RegW-COM-O-CLSID – This is the first time the registry path to a COM class with this CLSID has been modified.
Prof-CPM-DestUT-U-DestUT – This is the first time a member with this user type was successfully granted IAM permissions in a GCP policy. IAM policies determine the roles and permissions granted to users on a resource.
Fact-PCSplashtop-InstalledService – The Splashtop remote desktop access service has been installed.
Cntx-PC-ECrit-CS-DE – Destination endpoint is critical or a Domain Controller: True\False
Prof-CA-IC-O-U – This is the first time this user has created an image. An abnormal image upload could mean the image was created with a malicious intent. A malicious image could be used to trick users to create a VM that will contains a shellcode or a malware implanted in advance by an attacker.
Prof-PC-CmdArgs-Msbuild-O-XMLParam – This is the first time the 'msbuild.exe' process has been used to build a project with this xml file.
Prof-EL-AP-U-AP – This is the first time this user has attempted to perform a remote Windows login or access using this authentication package. These events may include both failed and successful logins.
Prof-SA-PN-U-PN – This is the first time an alert triggered on this process for this user.
Cntx-GA-TIRansomware-DIP – Destination IP is marked as a ransomware by threat intelligence: True\False
Fact-PCpcalua-IC – The PCALUA (Program Compatibility Assistant Service) process has been used to execute an indirect command. This sigma rule is authored by E.M. Anhaus (originally from Atomic Blue Detections, Endgame), oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/deprecated/windows/proc_creation_win_indirect_cmd.yml
Prof-UCreate-Z-O-SZ – This is the first time a user account has been created in this network zone.
Cntx-FUSB-Outlook – File has a .pst/.ost extension: True\False
Prof-AI-AS-Plt-U – This is the first time this user has shared an AI agent on this platform.
Prof-SA-AS-SE-AS – This is the first time a security alert with this subject triggered from this endpoint.
Cntx-PC-Critical-Parent-SystemEnum – Parent process is a system enumeration tool: True\False
Prof-GMA-U-O-UD – This is the first time a user has been added to a group by a user in this department.
NumDCP-SA-ANC-UD-AN – An abnormal number of unique alerts have triggered for users in this department.
Cntx-PCapplocker-UAC – Process is a known Applocker bypass process: True\False
Prof-GA-RGN-O-RGN – This is the first time this cloud region has been observed for the organization.
Fact-Web-TIRansomware – An HTTP communication attempt has been made to a ransomware associated domain. These events may include both failed and successful traffic.
Fact-PCcsc-AP – The CSC (C# Compiler) process has been spawned by a command line executable or a Microsoft Office process. This sigma rule is authored by Florian Roth (Nextron Systems), Nasreddine Bencherchali (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_csc_susp_parent.yml
NumSP-Web-Bytes-U-BytesStorageOut – An abnormal amount of bytes have been uploaded to file sharing websites for this user.
Prof-RA-R-U-RA – This is the first time this user assumed this role.
Fact-PCwsreset-UAC – The WSReset (Windows Store Reset) process has spawned a child process that it shouldn't normally spawn. This sigma rule is authored by E.M. Anhaus (originally from Atomic Blue Detections, Tony Lambert), oscd.community, Florian Roth and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_uac_bypass_wsreset.yml
NumCP-RegD-EC-U – An abnormal number of registry deletion events have been observed for this user.
Fact-RegW-RunService – Run Services registry keys have been modified.
Prof-MFA-FailureReason-U-FailureReason – This is the first time this user failed to authenticate with MFA authentication with this failure reason.
NumDCP-SA-ANC-U-AN – An abnormal number of unique alerts have triggered for this user.
NumDCP-PLA-LocC-U-LocCity – An abnormal number of unique cities have been observed in physical access events for this user.
Prof-DS-E-O-SE – This is the first time a user in the organization performed an activity on a directory service object from this endpoint.
Prof-CPM-DestD-U-DestD – This is the first time a user from this domain was successfully granted IAM permissions in a GCP policy. IAM policies determine the roles and permissions granted to users on a resource.
NumDCP-FRead-EC-UP-FP – An abnormal number of unique files have been read in this platform for this user.
Prof-SEPwrshell-U-O-U – This is the first time this user executed a PowerShell script.
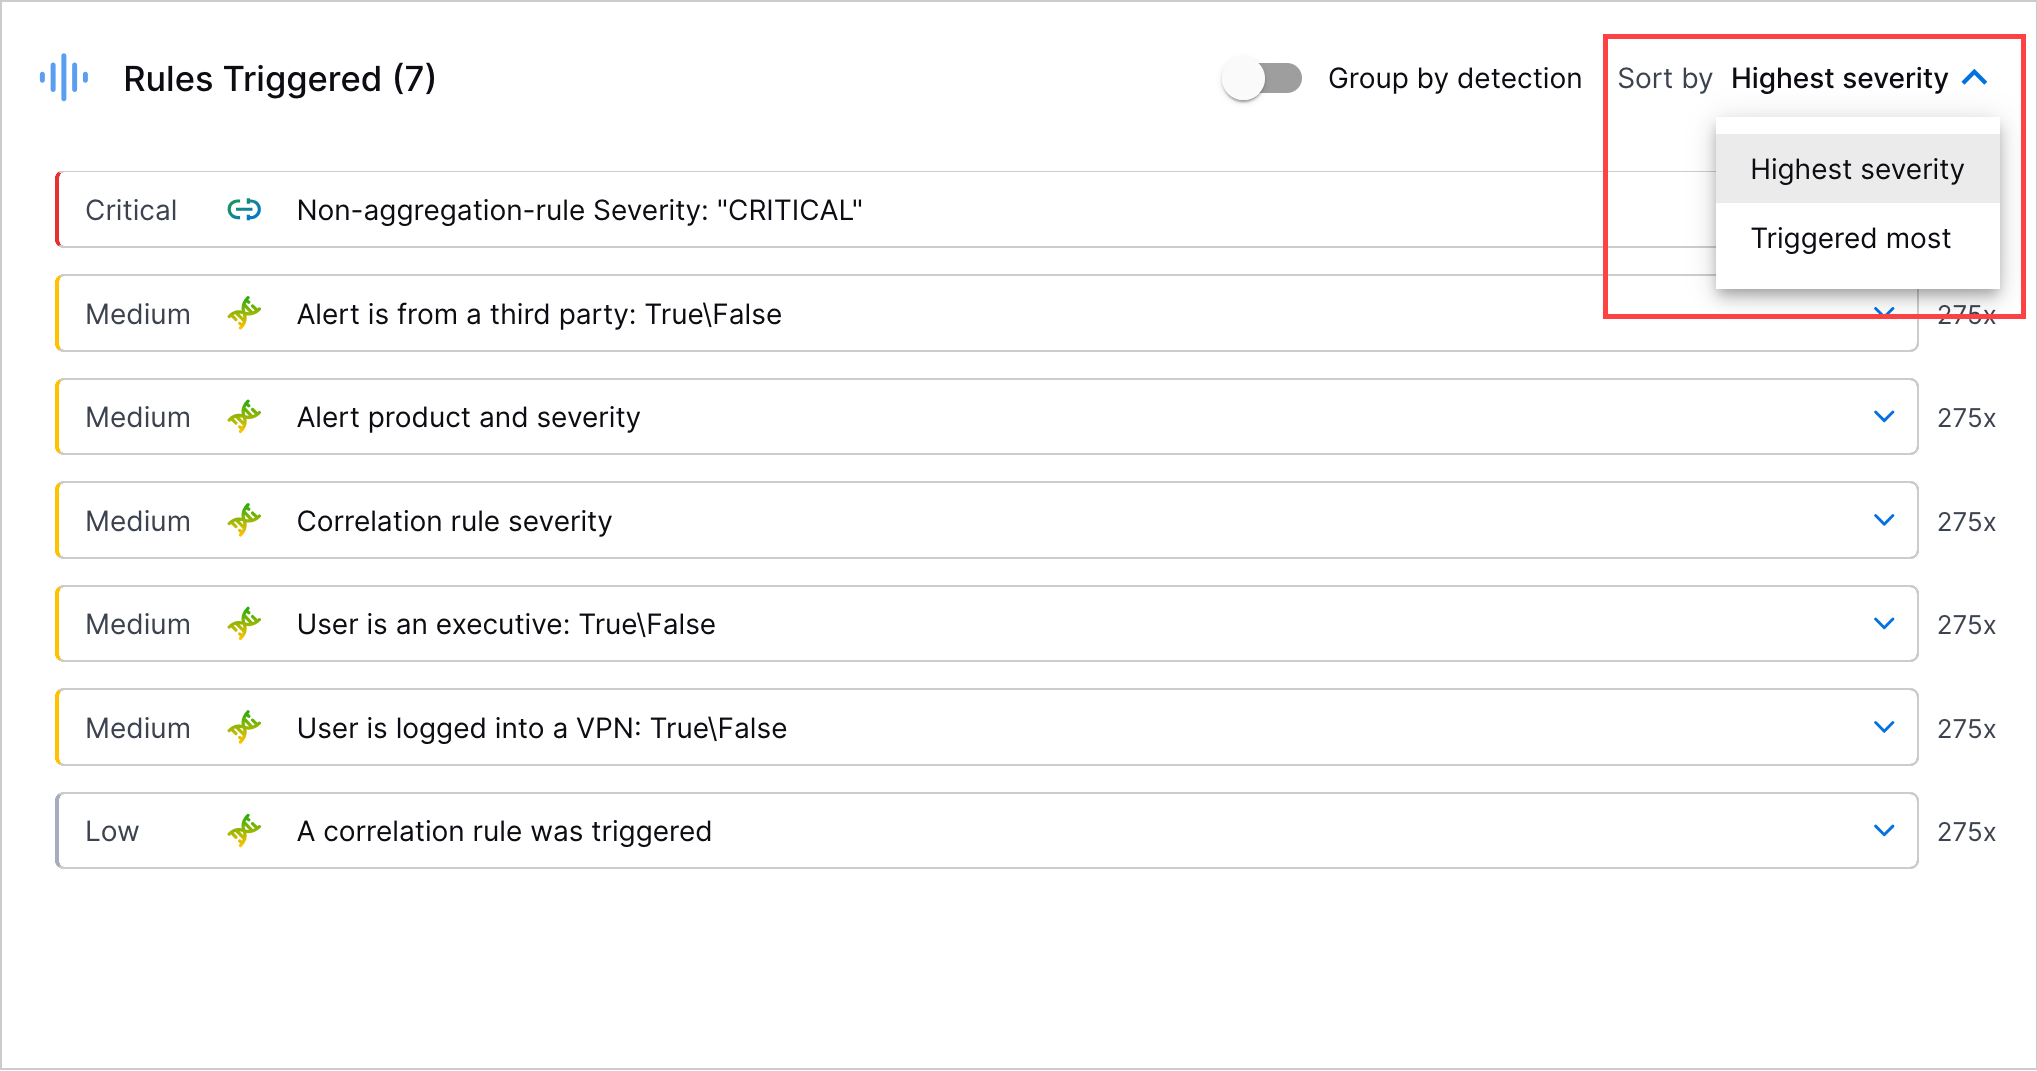
Cntx-SA-AC-ProdSev – Alert product and severity
Fact-FRead-Passwd – The passwd file is a plain text file in Unix-based operating systems, including Linux and macOS, that stores essential user account information. An attacker can try to read it to get information about the users include the passwords
NumSP-Web-Bytes-O-BytesStorageOut – An abnormal amount of bytes have been uploaded to file sharing websites for the organization.
Prof-SA-PN-O-PN – This is the first time a security alert triggered on this process for the organization.
NumDCP-Login-DZC-U-DZ – An abnormal number of unique destination network zones have been observed in login events for this user. These events may include both failed and successful logins.
Prof-DllLoad-Ext-PN-FileExt – This is the first time a DLL image file with this extension was loaded for this process.
Fact-PCsc-SvcMod-PCL – The SC (Service Controller) process has been used to configure a PowerShell service. This sigma rule is authored by Victor Sergeev, oscd.community, Nasreddine Bencherchali (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_sc_service_path_modification.yml
NumDCP-EL-UC-O-U-SE – An abnormal number of unique user names have been observed in endpoint logins for the organization per source endpoint. These events may include both failed and successful communications.
Fact-Fwrite-RCScripts – Adversaries can establish persistence by adding a malicious binary path or shell commands to rc.local, rc.common, and other RC scripts specific to the Unix-like distribution.
Fact-PCGoToMyPC-InstalledAgent – The GoToMyPC remote desktop access agent has been installed.
Cntx-GA-TI-SIP – Source IP is marked by threat intelligence: True\False
Fact-PCnwp-NWP – A Windows system process has been executed from a folder it shouldn't normally execute from. This sigma rule is authored by Florian Roth (Nextron Systems), Patrick Bareiss, Anton Kutepov, oscd.community, Nasreddine Bencherchali and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_system_exe_anomaly.yml
Fact-PCcsws-SExec – The 'wscript.exe' or 'cscript.exe' processes (Windows Script Host) have been used to execute a VBScript shell. These programs can be used to aid in fileless malware execution, a technique that can help evade detection. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_apt_cloudhopper.yml
NumDCP-CA-DAC-U-Disks – An abnormal number of volumes were attached to instances by this user. These events may include both failed and successful attachments.
Prof-GMA-E-O-DE – This is the first time a user has been added to a group on this endpoint.
Fact-PCGoToMyPC-InstalledService – The GoToMyPC remote desktop access service has been installed.
Cntx-PC-Critical-Parent-Crit – Parent process is a known critical command: True\False
NumCP-DSOW-EC-U – An abnormal number of directory service events have been observed for this user. Directory services typically manage various types of objects to organize and administer resources within a network environment.
NumSP-FRead-FS-UP-Bytes – An abnormal amount of file bytes have been read in this platform for this user.
Fact-PCGoToMyPC-StartedService – The GoToMyPC remote desktop access service has been started.
Fact-PCpwrshell-HidExec – The PowerShell process has been executed with a hidden or non-interactive console window. This sigma rule is authored by Florian Roth (Nextron Systems), Daniel Bohannon (idea), Roberto Rodriguez (Fix). The content of this repository is released under the [Detection Rule License (DRL) 1.1](https://github.com/SigmaHQ/Detection-Rule-License). Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_powershell_susp_parameter_variation.yml
Prof-PCnet-U-O-U-netlocalgroup – This is the first time a user account has been added to a group using 'net.exe' for this user.
Prof-ELF-E-U-DE – This is the first time this user has failed to log into this endpoint. The user might have logged in successfully before, but this is the first time a failed login event was observed on the endpoint.
Prof-BPM-U-PBPolicy-O-U – This is the first time this user has successful edited the IAM policy of a bucket in AWS. IAM bucket policies determine the access users and other identities have to the files and objects inside the storage bucket.
Fact-PCcsws-SExec-PP – The 'wscript.exe' or 'cscript.exe' processes (Windows Script Host) were used to execute a script from the user directory or the program data directory. This sigma rule is authored by Margaritis Dimitrios (idea), Florian Roth (Nextron Systems), oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_malware_script_dropper.yml
Prof-RegW-EnvVarPath-O-U – This is the first time this user has modified the PATH environment variable by writing to the registry value 'HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Session Manager\Environment\Path'.
Fact-Web-TITOR-Dom – An HTTP communication attempt has been made to a known TOR web proxy domain. These events may include both failed and successful traffic.
Prof-Login-EmD-Plt-EmD – This is the first time this email domain has been used to successfully log into this platform.
NumCP-AI-CDC-UPLT – An abnormal number of AI conversations have been successfully deleted by this user on this platform.
Prof-AI-PI-O-U-Exec – This is the first time an AI request that attempts to cause the agent to execute a command or a script has been sent by this user.
Fact-PC-SuspFind – Adversaries may enumerate files and directories or may search in specific locations of a host or network share for certain information within a file system. This command searches for files with the setuid (SUID) permission set for the owner.
Prof-EMR-FileExt-UD-FileExt – This is the first time a user in this department has received an email attachment with this extension.
Fact-PCsetspn-SPNDisc – The 'setspn.exe' process has been used to query service principal names. This sigma rule is authored by Markus Neis, keepwatch and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_setspn_spn_enumeration.yml
Fact-PC-DisableHistoryCol – History collection can be disabled in unix shells by modifying the history environment variables. This can help the attacker ot evade detection.
Prof-AL-E-O-SE – This is the first time a user in the organization attempted to log into an application from this endpoint. These events may include both failed and successful logins.
Prof-VPNIn-Rlm-U-Rlm – This is the first time this user attempted to log into a VPN with this realm. These events may include both failed and successful logins.
Prof-GMA-OU-GN-UOU – This is the first time a user in this OU has been added to this group.
Cntx-SA-Ecrit-SE – Source endpoint is critical: True\False
Fact-PCTeamViewer-InstalledAgent – The TeamViewer remote desktop access agent has been installed.
Cntx-Login-LType – Login type
Cntx-GMA-GCrit-Admin – Security group is privileged: True\False
NumCP-FDnld-EC-O – An abnormal amount of file download events have been observed for the organization.
NumDCP-RegW-RPC-ServicesStop-U-RP – An abnormal number of unique services have been stopped by modifying the registry for this user.
Fact-PCvssadmin-SCD – The VSSAdmin (Volume Shadow Copy Service Admin) process has been used to delete a shadow copy. This sigma rule is authored by Florian Roth (Nextron Systems), Michael Haag, Teymur Kheirkhabarov, Daniil Yugoslavskiy, oscd.community, Andreas Hunkeler (@Karneades) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_shadow_copies_deletion.yml
Prof-PCwmic-IR-O-U-usr – This is the first time a user account has been renamed using 'wmic.exe' for this user.
NumCP-PC-SudoCount-U – An abnormal number of 'sudo' (Superuser Do) process executions have been observed for this user.
Fact-PCnetsniff-SniffT – A network sniffing tool has been executed.
Prof-PC-PPN-PN-PPN – This is the first time this parent process has been observed for this matured child process.
Fact-UModify-UACPreAuthDisable – UAC pre-authentication has been disabled for a user account.
Fact-PCrundll32-Meterpreter – The 'rundll32.exe' process has been used to execute a known Meterpreter/Cobalt Strike module. This sigma rule is authored by Teymur Kheirkhabarov, Ecco, Florian Roth and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/builtin/security/win_security_meterpreter_or_cobaltstrike_getsystem_service_install.yml
Prof-RegW-SilentExitMon-O-U – This is the first time this user has modified or created the silent exit configuration of a process by writing a registry key\value under the key 'HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SilentProcessExit'.
Fact-PCIOC-ZxShell – The 'rundll32.exe' process has been used to execute a known 'ZxShell' backdooring software module. This sigma rule is authored by Florian Roth (Nextron Systems), oscd.community, Jonhnathan Ribeiro and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules-emerging-threats/2014/TA/Axiom/proc_creation_win_apt_zxshell.yml
Prof-PCnetsh-U-O-U – This is the first time firewall policies have been enumerated using 'netsh.exe' for this user.
Prof-RA-R-UPlt-RN – This is the first time this user has assigned this role on this platform.
Fact-PCmwc-PExec – The Microsoft Workflow Compiler process has been executed. Microsoft Workflow Compiler may permit the execution of arbitrary unsigned code. This sigma rule is authored by Nik Seetharaman, frack113 and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_lolbin_workflow_compiler.yml
Prof-DSF-AT-U-AT – This is the first time this directory service activity type failed for this user. Directory services typically manage various types of objects to organize and administer resources within a network environment.
Prof-PwdChkout-E-U-SE – This is the first time this user retrieved a password from this endpoint.
Prof-PCwmic-IR-O-U-grp – This is the first time a group has been renamed using 'wmic.exe' for this user.
Prof-SADLP-Tld-Proto-Tld – This is the first time a DLP alert triggered on this domain for this protocol.
Prof-PC-E-O-SE-Modprobe – This is the first time a process execution of a 'modprobe' (Module Probe, a kernel module management tool) command has been observed on this endpoint.
Cntx-PC-Critical-Pentest – Process is a known pentesting tool
Prof-VPNIn-SC-O-SC – This is the first time a user attempted to log into a VPN from this country. These events may include both failed and successful logins.
Prof-PC-PN-Plt-PN – This is the first time this process has been executed in this platform. This feature only models processes from - Windows and Unix commands, pentest tools, system enumeration, account enumeration and network sniffers.
Fact-PCpwrshell-AMSI – The PowerShell process has been used to disable AMSI (Anti Malware Scan Interface) Scanning using AmsiInitFailed. This sigma rule is authored by Markus Neis, @Kostastsale and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_powershell_amsi_init_failed_bypass.yml
NumSP-Web-Bytes-U-BytesStorageIn – An abnormal amount of bytes have been downloaded from file sharing websites for this user.
Prof-Login-E-DE-SZ – This is the first time a successful login has been observed from this network zone to this endpoint.
Fact-PCcertutil-SuspCmd – The CertUtil (Certification Utility) process has been executed with suspicious command line parameters. This sigma rule is authored by Florian Roth (Nextron Systems), juju4, keepwatch and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_certutil_decode.yml, https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_certutil_download.yml, https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_certutil_encode.yml.
NumDCP-VPNln-UC-O-U-SE – An abnormal number of unique user names have been observed in VPN login for the organization per source endpoint. These events may include both failed and successful communications.
Fact-PCbitsadmin-FDnld – The BITSAdmin (Background Intelligent Transfer Service Admin) process has been used to download a file. This sigma rule is authored by Michael Haag, FPT.EagleEye and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_bitsadmin_download.yml
Fact-PCpwrshell-SCC – The PowerShell process has been used to create a shadow copy. This sigma rule is authored by Teymur Kheirkhabarov, Daniil Yugoslavskiy, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_shadow_copies_creation.yml
Cntx-GA-TI-DIP – Destination IP is marked by threat intelligence: True\False
Fact-PCicacls-FPermMod-Everyone – The ICACLs (Integrity Control Access Control Lists) process has been used to grant global permissions on a file.
Cntx-PC-Critical-Sniffer – Process is a sniffing tool: True\False
Fact-Web-TI-MalDom – An HTTP communication attempt has been made to a malicious site category. These events may include both failed and successful traffic.
Fact-PCsc-SuspSP – The SC (Service Controller) process has been executed with suspicious command line parameters.
Fact-PC-ClearComHistory – This can help the attacker ot evade detection.
Prof-GA-Country-U-SCountry – This is the first time an activity has been observed from this country for this user, determined by geolocation lookup.
Cntx-PC-FC-SusDir – Process executed from a known suspicious folder: True\False
Fact-PCcertutil-AP – The CertUtil (Certification Utility) process has been spawned by a command line executable. This sigma rule is authored by Florian Roth (Nextron Systems), Tim Shelton and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_shell_spawn_susp_program.yml
Fact-PCsr-AC – The Sound Recorder process was used to record external audio. This sigma rule is authored by E.M. Anhaus (originally from Atomic Blue Detections, Endgame), oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_soundrecorder_audio_capture.yml
Fact-PCtshark-NetSniff – The TShark process (a network sniffing tool) has been executed. This sigma rule is authored by Timur Zinniatullin, oscd.community, Nasreddine Bencherchali (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_network_sniffing.yml
Prof-SA-AN-SE-RN – This is the first time this correlation rule triggered from this endpoint.
Cntx-SA-Ecrit-DE – Destination endpoint is critical: True\False
Fact-PCtakeown-FO – The 'takeown.exe' process has been used to take ownership of a file or a folder.
NumCP-FUpld-EC-U – An abnormal amount of file upload events have been observed for this user.
Prof-DB-DBOp-UDBN-DBOp – This is the first time a database operation has been observed for this user. A database operation consists of any action in a database query (i.e. SELECT, DROP, UPDATE, etc...).
Fact-RegW-AppShim – A registry key/value has been created under the Shim database registry key 'HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\AppCompatFlags\Custom' or 'HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\AppCompatFlags\InstalledSDB
Prof-RA-R-Plt-RN – This is the first time this role was assigned on this platform.
Prof-CA-SC-O-U – This is the first time this user has successfully created a snapshot of a compute instance.
Prof-Fwrite-U-O-U-Plist – This is the first time a plist file was created by this user.
Fact-PCscrcons-WMI – The 'scrcons.exe' process (WMI script event consumer) has been executed. This sigma rule is authored by Thomas Patzke and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_wmi_persistence_script_event_consumer.yml
Prof-WinSC-U-DE-DU – This is the first time a service permitted to run under this user's credentials was created on this endpoint.
Fact-PCIOC-Archer – The 'rundll32.exe' process has executed a command associated with the Archer malware service. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_malware_fireball.yml
Cntx-GA-SA – User is a service account: True\False
Cntx-EL-ET-Wrkstn – Destination endpoint is a workstation: True\False
Prof-DB-U-DBN-UD – This is the first time a database event in this database has been observed for a user in this department. A database event consists of any event or operation performed on a database. These events may include both failed and successful operations.
Prof-AI-AC-PLT-UD – This is the first time a user in this department has created an AI agent with this platform.
Fact-PCnetsh-FD – The NetSh (Network Shell) process has been used to disable the Windows firewall. This sigma rule is authored by Fatih Sirin and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_netsh_fw_disable.yml
NumDCP-ELF-SEC-DE-SE – An abnormal number of unique endpoints have been observed failing to log into this endpoint.
Fact-CA-Startup-StartupScriptAWS – A startup script was added or modified in an instance in AWS.
Prof-UCreate-DC-U-DC – This is the first time this domain controller has processed a user creation request for this user.
NumDCP-PCCEnum-TC-U-CEnum – An abnormal number of unique credential enumeration tools have been executed for this user.
Fact-PCcreateminidump-ProcMemDump – The CreateMiniDump process (a memory dumping tool) has been executed. This tool is used to dump the LSASS process memory for credential extraction on the attacker's machine. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_hktl_createminidump.yml
Prof-ShA-SE-SN – This is the first time this network share has been accessed from this endpoint.
Prof-VPNIn-SC-U-SC – This is the first time this user attempted to log into a VPN from this country. These events may include both failed and successful logins.
Fact-CPM-PCrit-GCPPublic – A policy has been successfully modified to allow public access to a GCP resource. This activity should be noted since public resources can be read or downloaded by everyone.
Fact-PC-Setfile-HiddenFile – The "setfile" unix process can be used to make files hidden by modifying their attributes, making sure they remain undetected by users. An attacker can create hidden file to evade detection.
NumCP-WebF-EC-U-Id – An abnormal number of HTTP 4xx/5xx error responses has been observed for this user.
Fact-PCcontrol-CPLFExec – The Windows control panel process has loaded control panel items outside of the folders they are loaded from by default. This sigma rule is authored by Kyaw Min Thein, Furkan Caliskan (@caliskanfurkan_) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_control_panel_item.yml
Prof-RA-U-O-U – This is the first time this user assumed a role.
NumCP-PCpwrshell-EC-UD – An abnormal number of PowerShell process executions have been observed for users in this department.
Cntx-GA-AF – Activity failed: True\False
Fact-PC-Chmod-Setuid – The setuid bit was set using chmod, which can cause a file to execute with the privileges of its owner.
Prof-PCnet-U-O-U-netuserdel – This is the first time a user account has been deleted using 'net.exe' for this user.
NumCP-PwdChkout-EC-U-SC – An abnormal number of password retrievals have been observed for this user.
Prof-PCpwrshell-En-O-U – This is the first time a process execution of a PowerShell process with an encrypted command has been observed for this user.
Fact-PC-MshtaScriptExecution – The MsHTA (Microsoft HTML Application) process has been used to execute a script code.
Prof-SA-U-O-UD – This is the first time a security alert triggered for users in this department.
Fact-PCecho-EchoP – The 'echo.exe' process has been used to execute a command associated with Meterpreter and Cobalt Strike's GetSystem system privilege escalation function.
Prof-Web-WebDom-O-U-WebDomIP – This is the first time an HTTP communication attempt directly to an IP address has been observed for this user. These events may include both failed and successful traffic.
Prof-USB-DevId-O-DevId – This is the first time this peripheral device ID has been observed for the organization.
Prof-CA-IE-O-U – This is the first time this user has exported a compute instance. Instance export could be used by an attacker to collect sensitive data that resides inside the organization's virtual machines.
Prof-SA-DP-LE-DP – This is the first time a network alert on this port has been triggered for this destination endpoint.
Fact-PCrundll32-ProcMemDump-1 – The 'rundll32.exe' process has been used to dump process memory using the 'minidump' exported function in 'comsvcs.dll'. This sigma rule is authored by Florian Roth (Nextron Systems), Modexp, Nasreddine Bencherchali (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_rundll32_process_dump_via_comsvcs.yml
Prof-EMR-ED-O-ED – This is the first time a user from the organization has received an email from this email domain.
Prof-RC-Perm-Plt-Perm – This is the first time a role has been created with these permissions on this platform.
Prof-Web-BinURL-O-U – This is the first time an executable file was downloaded during an HTTP session for this user. These events may include both failed and successful traffic.
Fact-PCmwc-mstsc – The MSTSC (Microsoft Terminal Services Client) process has been used to shadow an existing remote desktop session. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_mstsc_rdp_hijack_shadowing.yml
Prof-DS-AT-DSOC-AT – This is the first time this activity has been observed for this directory service object class. Directory services typically manage various types of objects to organize and administer resources within a network environment.
Fact-PC-TempF-Outlook – A process have been executed from an Outlook temporary folder. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_office_outlook_execution_from_temp.yml
Prof-DS-DSOC-O-DSOC – This is the first time a user in the organization performed an activity on a directory service object with this object class.
Prof-STC-E-O-DE – This is the first time a scheduled task has been created on this endpoint.
NumCP-PC-ModprobeCmdC-U – An abnormal number of 'modprobe' (Module Probe, a kernel module management tool) process executions have been observed for this user.
Prof-ShA-SZ-SN – This is the first time this network share has been successfully accessed from this network zone.
Fact-PCdns-SIGRed – The DNS process has spawned a child process that it shouldn't normally spawn.
Prof-DL-U-O-Uplt – This is the first time a kernel module\driver was loaded for this user.
Prof-Login-E-SE-DZ – This is the first time a user on this endpoint successfully logged into this network zone.
Fact-PCSplashtop-StartedService – The Splashtop remote desktop access service has been started.
Prof-UCreate-E-U-DE – This is the first time this user has created a user account on this endpoint.
Prof-DllLoad-Dir-O-FD – This is the first time a DLL image file was loaded from this folder for the organization.
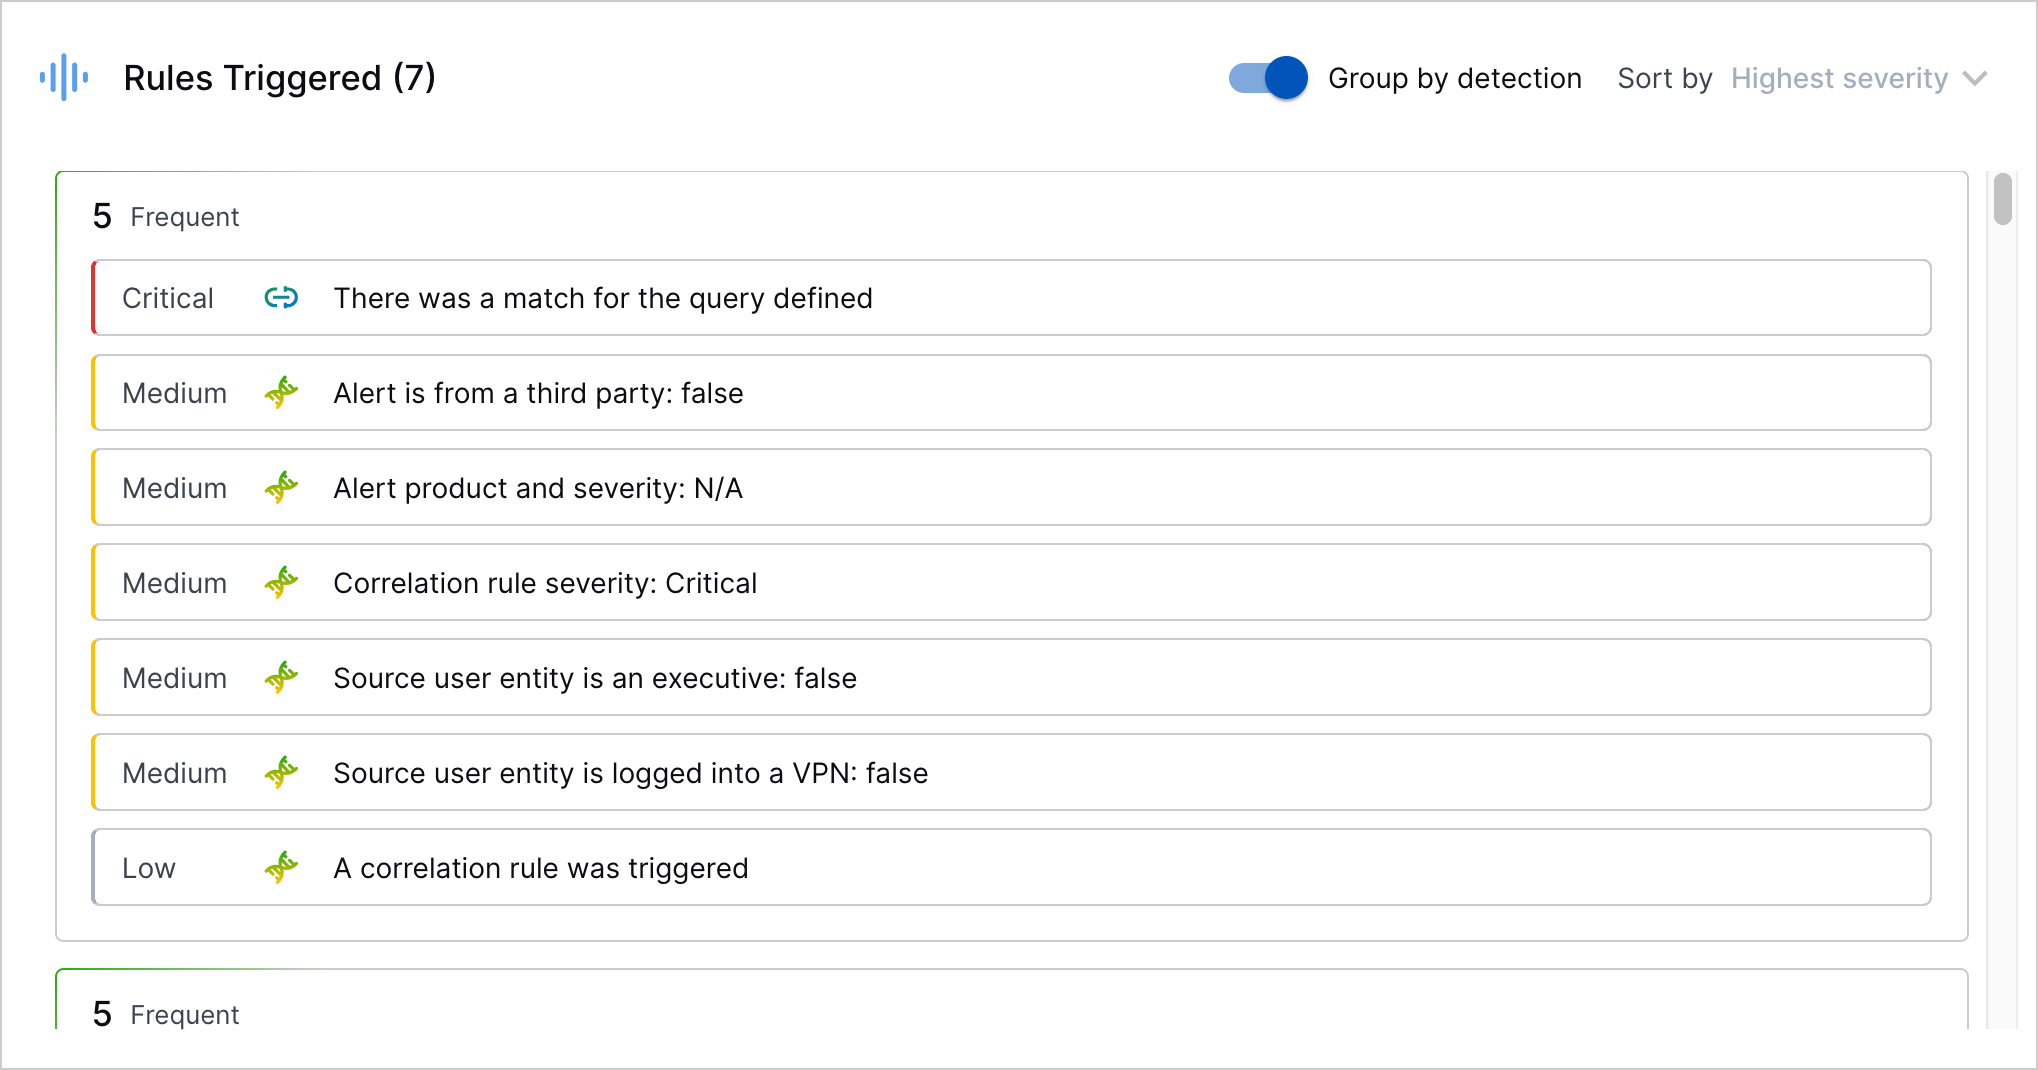
Fact-SA-ET-RN – A correlation rule has been triggered
Fact-FWrite-DExt – A file with an '.exe' extension following a non-executable extension was written to. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_double_extension.yml
Fact-PCrundll32-ADllLoad-Trojan –The 'rundll32.exe' process has loaded a module from the AppData folder. This sigma rule is authored by Florian Roth (Nextron Systems), Jonhnathan Ribeiro, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_apt_sofacy.yml
Prof-FPM-PublicCloud-B-U – This is the first time a cloud storage object was modified to become public in this bucket. By manipulating file permissions to make the object public, attackers can expose the data of important or sensitive files, making them available to read, download or even modify by everyone.
Prof-VPNOut-SDM-U-SD – An abnormal VPN session length has been observed for this user.
NumCP-AI-QC-U – An abnormal number of successful AI requests have been performed by this user. AI requests consist of one or more prompts.
Prof-RegW-AppPaths-O-U – This is the first time this user has modified a registry key\value under the App Paths key '[HKLM/HKCU]\Software\Microsoft\Windows\CurrentVersion\App Paths'.
Prof-PwdChkout-SV-U-SV – This is the first time this user retrieved a password from this safe.
Cntx-EL-UCrit-Exec – User is an executive: True\False
NumCP-PC-KextloadCmdC-U – An abnormal number of 'kextload' (Kernel Extension Load) process executions have been observed for this user.
NumCP-PwdChkout-EC-O-SC – An abnormal number of password retrievals have been observed for the organization.
Fact-PC-DExt – A process with an '.exe' extension following a non-executable extension has been executed. This sigma rule is authored by Florian Roth (Nextron Systems), @blu3_team (idea), Nasreddine Bencherchali (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_double_extension.yml
Prof-DB-DBOp-SZDBN-DBOp – This is the first time a database operation has been observed from this network zone. A database operation consists of any action in a database query (i.e. SELECT, DROP, UPDATE, etc...).
Prof-Auth-U-Okta-AnonVPN – This is the first time an Okta user has used an anonymous VPN to authenticate.
NumCP-PrivUse-EC-U-APC – An abnormal number of administrative privilege access events have been observed for this user.
NumSP-DNSReq-Bytes-SE-Bytes – An abnormal amount of bytes were sent in DNS queries from this endpoint.
Prof-GA-CSVC-UD-SVC – This is the first time this cloud service was observed in events in this platform for users in this department.
Fact-PCrundll32-Cpl – The Windows control panel process has spawned the 'rundll32.exe' process. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_rundll32_susp_control_dll_load.yml
Prof-PCnet-U-O-U-groups – This is the first time local groups have been enumerated using 'net.exe' for this user.
Fact-ELF-SA – A service account failed to log into an endpoint using an interactive Windows logon type. A service account is a user account that belongs to an application rather than an end user.
Prof-UCreate-U-DE-U-SystemAcct – This is the first time this system account has created a user account on this endpoint.
Prof-GA-CSVC-U-SVC – This is the first time this cloud service was observed in events in this platform for this user.
Prof-AI-O-Guardrail-Block – This is the first time a user in the organization has triggered an AI guardrail violation.
Prof-ELNAC-Loc-U-Loc – This is the first time this user has been observed logging into an endpoint using a network access control platform from this network location.
Prof-CA-IC-Publisher-O-Publisher – This is the first time this image publisher has been observed in a successful virtual machine image creation for the organization.
Prof-Login-E-U-SZ – This is the first time a successful login has been observed from this network zone for the this user.
Fact-PCwmic-WebExec – The WMIC (WMI Command Line) process has been used to invoke a remote XSL script. This sigma rule is authored by Markus Neis, Florian Roth. The content of this repository is released under the [Detection Rule License (DRL) 1.1](https://github.com/SigmaHQ/Detection-Rule-License). Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_wmic_squiblytwo_bypass.yml
Fact-PCSplashtop-InstalledAgent – The Splashtop remote desktop access agent has been installed.
Fact-PCpwrshell-AD – The PowerShell process has executed a 'ps1' script from the AppData folder. This sigma rule is authored by Florian Roth (Nextron Systems), Jonhnathan Ribeiro, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_powershell_susp_ps_appdata.yml
NumDCP-FWrite-EC-U-FP – An abnormal number of unique files have been written for this user.
Fact-PCiodine-PExec – The 'iodine.exe' (a DNS tunneling tool) process has been executed. This sigma rule is authored by Daniil Yugoslavskiy, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_dns_exfiltration_tools_execution.yml
Prof-AI-AC-PLT-U – This is the first time this user has created an AI agent with this platform.
NumDCP-PwdChkout-SVC-U-SV – An abnormal number of unique safes have been observed in passwords retrieval events for this user.
Fact-RegW-CodeSigningPolicy – A code signing policy has been modified by writing to the registry key HKCU\Software\Policies\Microsoft\Windows NT\Driver Signing.
Prof-PLA-Loc-U-LocBldg – This is the first time this user has physically accessed this building.
Prof-DBQ-RS-U-RS – An abnormal successful database query response size has been observed in this database for this user.
Fact-PCpsr-Screenshot – The PSR (Problem Steps Recorder) process has been used to take a screenshot. This is a benign event that is still useful to keep track of. This sigma rule is authored by Beyu Denis, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_psr_capture_screenshots.yml
Fact-PCwevtutil-EventTracingDisable – The WEvtUtil (Windows Event Utility) process has been used to disable an ETW (Event Tracing for Windows). This sigma rule is authored by @neu5ron, Florian Roth (Nextron Systems), Jonhnathan Ribeiro, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_etw_trace_evasion.yml
NumSP-EMR-Bytes-DU-Bytes – An abnormal amount of bytes have been received in incoming emails for this user.
Fact-PCsdbinst-SI – The SDBInst (Application Compatibility Database Installer) process has been used to register a shim database. This event is notable as shims can be used to intercept API calls and load malicious DLLs enabling an attacker to run malicious software. This sigma rule is authored by Markus Neis and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_sdbinst_shim_persistence.yml
Prof-RegR-SAM-O-U – This is the first time this user has read a registry value under the SAM registry key.
NumDCP-EL-DEC-O-DE – An abnormal number of unique destination endpoints have been observed in endpoint login events for the organization. These events may include interactive Window logins and other (interactive or not) OS logins, both failed as successful.
Fact-PCpwrshell-Empire – The PowerShell process has been used to execute a command associated with an Empire module.
Cntx-EMS-Outcome – Email sent outcome
Fact-FRead-Shadow – The shadow file is a file in Unix-based operating systems, including Linux and macOS, that stores password-related information for user accounts. It is a crucial component of the system's security as it helps protect user passwords from unauthorized access. An attacker can try to read it to get the passwords of the users.
Fact-EMRC-FwR-ExtDom – An inbox rule has been configured to forward emails to an email address that's in a different domain than the rule's creator.
NumCP-PCpwrshell-EC-O – An abnormal number of PowerShell process executions have been observed for the organization.
Fact-CA-SPM-PublicAWS – A compute snapshot resource in AWS has been made public, granting access to all users.
Prof-GA-E-Plt-SZ – This is the first time an activity from this network zone has been observed for this platform.
Cntx-VPNln-UCrit-Contractor – User is a contractor : True\False
NumSP-DNSReq-Bytes-SZ-Bytes – An abnormal amount of bytes were sent in DNS queries from this network zone.
Prof-RegW-FileAssoc-O-U – This is the first time this user has modified a command of a file assocation handler by modifing its registry configuration.
NumDCP-EL-UC-SE-U – An abnormal number of unique user names have been observed in endpoint logins from this endpoint. These events may include both failed and successful communications.
Cntx-SA-AC-RSev – Correlation rule severity
Prof-EL-EDC-O-SZ – This is the first time an endpoint login event to a domain controller has been observed originating from this network zone for the organization. These events may include both failed and successful logins.
NumCP-PC-InsmodCmdC-DE – An abnormal number of 'insmod' (Install Module) process executions have been observed on this endpoint.
Fact-PCnltest-DomDisc – Windows command line tools to identify domain trust relationships, which may be used during reconnaissance. This sigma rule is authored by E.M. Anhaus, Tony Lambert, oscd.community, omkar72. The content of this repository is released under the [Detection Rule License (DRL) 1.1](https://github.com/SigmaHQ/Detection-Rule-License). Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_dsquery_domain_trust_discovery.yml
Prof-UPwdMod-U-O-U – This is the first time this user has modified the password of another user account.
Cntx-PC-ECrit-Server-SE – Source endpoint is a server: True\False
Prof-AI-UD-Guardrail-Block – This is the first time a user in this department has triggered an AI guardrail violation.
Cntx-PC-Critical-Parent-CredEnum – Parent process is a credential enumeration tool: True\False
Prof-UCreate-U-Plt-U – This is the first time this user has created a user account on this platform.
Prof-SA-AN-SZ-AN – This is the first time this security alert triggered in this network zone.
Prof-UDel-U-O-U – This is the first time this user has deleted a user account.
Fact-PCstunnel-Exfil – The 'stunnel.exe' (a data exfiltration tool) process has been executed. This sigma rule is authored by Daniil Yugoslavskiy, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_exfiltration_and_tunneling_tools_execution.yml
Prof-PC-FPermMod-Cacl-O-U – This is the first time a file or folder permissions have been modified using 'icacls.exe' or 'cacls.exe' for this user.
Fact-PCLogMeIn-InstalledService – The LogMeIn remote desktop access service has been installed.
Prof-VPNIn-E-UD-SE – This is the first time a user in this department attempted to log into a VPN from this endpoint. These events may include both failed and successful logins.
Fact-PCcdb-DSE – The CDB (Console Debugger) process has been used to execute a script. This sigma rule is authored by Beyu Denis, oscd.community, Nasreddine Bencherchali and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_lolbin_cdb.yml
Cntx-EL-UCrit-ADomain – User is a domain account: True\False
Prof-RPM-PR-R-Public – This is the first time this role's permissions were modified to make it public.
Fact-PCpwrshell-AC – PowerShell commands that attempt to access or record audio from the system microphone. This sigma rule is authored by E.M. Anhaus (Atomic Blue Detections, Endgame), oscd.community, Nasreddine Bencherchali (Nextron Systems). The content of this repository is released under the [Detection Rule License (DRL) 1.1](https://github.com/SigmaHQ/Detection-Rule-License). Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_powershell_audio_capture.yml
Fact-Fwrite-LoginHookFile – Adversaries may use a Login Hook to establish persistence executed upon user logon. They can add or insert a path to a malicious script in the com.apple.loginwindow.plist file, using the LoginHook or LogoutHook key-value pair.
NumDCP-SADLP-ProtoC-U-Proto – An abnormal number of unique protocols have been observed in DLP alerts for this user.
Fact-RegE-SAM – The registry key 'HKLM\SAM' or 'HKLM\SYSTEM' has been exported from the registry.
Cntx-FRead-Repo – File is located in a repository: True\False
Fact-PCgup-AF – The Notepad++ updater has been executed from a folder it shouldn't normally execute from. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_gup.yml
NumDCP-EL-UC-DESE-U – An abnormal number of unique user names have been observed in endpoint logins for destination endpoint and source endpoint. These events may include both failed and successful communications.
Fact-EMS-Competition – An email has been sent to an email domain belonging to a competitor.
Fact-PCwindump-NetSniff – The WinDump process (a process dumping tool) has been executed. This sigma rule is authored by Timur Zinniatullin, oscd.community, Nasreddine Bencherchali (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_network_sniffing.yml
Cntx-UCreate-UCrit – User is local: True\False
NumCP-FUpld-EC-O – An abnormal amount of file upload events have been observed for the organization.
Prof-PCroute-NetDisc-U-PN – This is the first time a process execution of 'route.exe' has been observed for this user.
Prof-GCreate-U-P-UD – This is the first time users in this department have created a group on this platform.
Cntx-SA-VPN – User is logged into a VPN: True\False
Prof-SA-AN-O-RN – This is the first time this correlation rule triggered in the organization.
NumCP-PC-DirSearchCount-U – An abnormal number of unix file search process executions have been observed for this user.
Prof-Fwrite-SystemdService-O-U – This is the first time a systemd service file has been modified by this user.
Cntx-GMA-SelfAdd – User added themselves to a security group: True\False
Prof-STC-U-PN – This is the first time a scheduled task has been created and configured to execute this process for this user.
Fact-PCfsutil-JDel – The FSUtil (File System Utility) process has been used to create or delete a journal. This sigma rule is authored by Ecco, E.M. Anhaus, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_fsutil_usage.yml
Prof-DB-U-DBN-U – This is the first time a database event in this database has been observed for this user. A database event consists of any event or operation performed on a database. These events may include both failed and successful operations.
Prof-DllLoad-Dll-O-FN – This is the first time this DLL image file was loaded in the organization.
Prof-STC-O-UD – This is the first time a scheduled task has been created for users in this department.
Fact-PCesentutl-CDbC – The Esentutl (Extensible Storage Engine Utility) process has been used to copy files with credentials data. This sigma rule is authored by Teymur Kheirkhabarov, Daniil Yugoslavskiy, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_copying_sensitive_files_with_credential_data.yml
Prof-SA-DP-O-DP – This is the first time a network alert on this port has been triggered in the organization.
Fact-PCbcdedit-ESP – The BCDEdit (Boot Configuration Data Edit) process has been used to enable test signing.
Cntx-PCquser-ADisc – Local accounts enumerated using quser.exe: True\False
Fact-PCpassworddump-SecurityXploded – The 'passworddump.exe' process (a password dumping tool from the 'SecurityXploded' toolkit) has been executed. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_hktl_secutyxploded.yml
Cntx-GA-UDisabled – User owns a disabled account: True\False
Fact-UI-UOO – A user outside the organization was invited to this platform.
Prof-PC-CmdArgs-InstallUtil-O-EXEParam – This is the first time the 'installutil.exe' process has been executed with this EXE file as a parameter.
Prof-RegW-Services-O-U – This is the first time this user has modified or created a service by writing a registry key\value under the key 'HKLM\SYSTEM\CurrentControlSet\Services'.
NumCP-EMS-EC-U-Id – An abnormal number of outgoing emails have been observed for this user.
Prof-RegW-CORPROFILER-O-U – This is the first time this user has modified or created a registry value for an environment variable associated with the COR_PROFILER.
Prof-Network-ERDP-DE-SE – This is the first time a successful RDP connection has been observed from this source endpoint to this destination endpoint.
Prof-GCreate-U-O-UD – This is the first time for users in this department to create a group for the organization.
Fact-PCsharphound-BloodHound – The 'sharphound.exe' (a network domain enumeration tool) process has been executed.
Prof-EMS-Country-UD-DCountry – This is the first time a user in this department has sent an email to this country, as determined by geolocation lookup.
Prof-GA-Country-O-DCountry – This is the first time an activity has been observed to this country, determined by geolocation lookup.
NumCP-FUpld-EC-UD – An abnormal amount of file upload events have been observed for users in this department.
Prof-PC-PN-PltU-PN – This is the first time this process has been executed in this platform for this user. This feature only models processes from - Windows and Unix commands, pentest tools, system enumeration, account enumeration and network sniffers.
Fact-PCnwp-NWP-PPP – A Windows system process has been spawned by a parent process that's in a folder it shouldn't normally execute from. This sigma rule is authored by vburov and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_proc_wrong_parent.yml
Cntx-PC-Critical-Parent-Shell – Parent process is a shell process
Prof-PrivUse-U-O-U – This is the first time a Windows privileged has been used and invoked from this directory for this process.
Prof-DB-E-UDBN-SIP – This is the first time a successful database event in this database has been observed for this user from this IP address.
Prof-AI-AC-O-U – This is the first time this user has created an AI agent.
Fact-AI-Guardrail-Block – An AI guardrail violation has been observed.
Fact-PC-TsconRDPRedirection – The 'tscon.exe' has been used to redirect RDP traffic.
NumCP-ELF-EC-U-DZ – An abnormal number of failed logins to endpoints in this network zone have been observed for this user.
Prof-DS-E-UD-SE – This is the first time a user in this department performed an activity on a directory service object from this endpoint.
Fact-PCassoc-FAssocCh – The Assoc (File Association) process has been used to change the association of an extension to execution. This sigma rule is authored by Nasreddine Bencherchali (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_change_default_file_association.yml
Fact-PChttptunnel-ExfilTExec – The 'httptunnel.exe' (a data exfiltration tool) process has been executed. This sigma rule is authored by Daniil Yugoslavskiy, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_exfiltration_and_tunneling_tools_execution.yml
Fact-PCping-HexEn – The 'ping.exe' process has been used to ping a hex encoded IP address. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_ping_hex_ip.yml
Fact-PCspctl-DisableGatekeeper – The 'spctl' command has been used to disable the Gatekeeper.
Prof-RegD-Services-O-UD – This is the first time users in this department have deleted a service by deleting a registry key\value under the key 'HKLM\SYSTEM\CurrentControlSet\Services'.
Prof-BPM-Public-O-U – This is the first time this user has attempte to modify the IAM policy or the ACL of an AWS bucket to make it public to all users. These events may include both failed and successful modifications.
NumCP-AI-MC-U – An abnormal amount of AI agent modifications have been observed for a user.
Prof-RA-R-UDPlt-RN – This is the first time this role was assigned by users in this department on this platform.
Prof-SEPwrshell-SN-U-SN – This is the first time this user executed a PowerShell script with this name.
Prof-RCM-U-O-UPlt – This is the first time this user modified or created a role on this platform.
Prof-SA-AN-SE-AN – This is the first time this security alert triggered from this endpoint.
Fact-PCTeamViewer-StartedService – The TeamViewer remote desktop access service has been started.
Prof-DS-E-U-SZ – This is the first time this user performed an activity on a directory service object from this network zone.
Prof-EL-HT-U-HT – This is the first time this user has attempted to log into an endpoint of this type (server, workstation...). These events may include both failed and successful logins.
NumSP-Web-Bytes-U-BytesInPost – An abnormal amount of bytes have been uploaded to the web with POST requests for this user.
NumDCP-FC-EC-U-FP – An abnormal number of unique files have been copied in this platform for this user.
Prof-VPNIn-U-O-UC – This is the first time a user in this country attempted to log into a VPN. These events may include both failed and successful logins.
Cntx-PC-Critical-Parent-Webserver – Parent process is a web server process: True\False
NumCP-DSOW-EC-O – An abnormal number of directory service write events have been observed for the organization. Directory services typically manage various types of objects to organize and administer resources within a network environment.
Prof-EW-DCShadow-SE-O-SE – This is the first time the GC (global catalog) and DRS (directory replication service) service principal names have been added to this matured endpoint. These SPNs are required for the active directory replication process, and can be added to a rogue domain controller to execute a DCShadow attack.
Prof-WinSC-E-U-DE – This is the first time a service creation has been observed on this endpoint for this user.
Cntx-PC-Critical-Shell – Process is a shell process
Prof-CA-IKM-KeyCreateGCP-O-U – This is the first time this user added or modified an SSH key of an instance in GCP. These events may include both failed and successful modifications.
Fact-WinSC-SuspSC-Temp – A service has been created from a temporary internet files directory.
Cntx-SA-PA – Alert is from a third party: True\False
Fact-PCLogMeIn-StartedService – The LogMeIn remote desktop access service has been started.
Fact-RegE-Certs – Registry values related to certificates and private keys have been exported.
Prof-VPNIn-E-UD-DE – This is the first time a user in this department attempted to log into a VPN with this server. These events may include both failed and successful logins.
Fact-PCsvchost-DCOMLaunch – Remote DCOM activation under DcomLaunch service.
Cntx-GA-TIRansomware-SIP – Source IP is marked as a ransomware by threat intelligence: True\False
NumCP-ELF-EC-U-RDP – An abnormal number of failed RDP (remote desktop protocol) logins to this endpoint have been observed for this user.
NumCP-RegD-Services-EC-U – An abnormal number of unique service configurations have been deleted from the registry for this user.
Prof-GA-Plt-U-Plt – This is the first activity observed on this platform for this user.
Prof-MFA-MFADevice-U-MFADevice – This is the first time this user authenticates with MFA authentication using this device. These events may include both failed and successful logins.
Prof-USB-E-U-SE – This is the first time a peripheral device activity has been observed from this endpoint for this user.
Cntx-EL-UCrit-UPriv – User is privileged: True\False
Fact-Web-TIPhish-PhishDom – An HTTP communication attempt has been made to a phishing associated domain. These events may include both failed and successful traffic.
Prof-RegR-LSA-O-U – This is the first time this user has read a LSA secret from the registry.
Prof-GA-Op-Plt-Op – This is the first time this operation has been observed for this platform. Operations can include function types, APIs, application activities and more.
Fact-PCreg-SRH – Attempt to export sensitive Windows registry hives using reg.exe, which may be used to collect credentials or system secrets. This sigma rule is authored by Teymur Kheirkhabarov, Endgame, JHasenbusch, Daniil Yugoslavskiy, oscd.community, frack113. The content of this repository is released under the [Detection Rule License (DRL) 1.1](https://github.com/SigmaHQ/Detection-Rule-License). Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_reg_dumping_sensitive_hives.yml
Fact-PCreg-WDigest – The 'reg.exe' has been used to enable WDigest authentication through the registry.
NumDCP-AL-UC-PltSE-U – An abnormal number of unique user names have been observed in application logins to this platform from this endpoint. These events may include both failed and successful communications.
Prof-EL-EDC-U-SZ – This is the first time an endpoint login event to a domain controller has been observed originating from this network zone for this user. These events may include both failed and successful logins.
Prof-VPNIn-Rlm-UD-Rlm – This is the first time a user in this department attempted to log into a VPN with this realm. These events may include both failed and successful logins.
Fact-PCpwrshell-ELT – The PowerShell process has been used to clear or delete an event log. This sigma rule is authored by Ecco, Daniil Yugoslavskiy, oscd.community, D3F7A5105 and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_eventlog_clear.yml
Fact-PCAnyDesk-InstalledAgent – The AnyDesk remote desktop access service has been installed.
Fact-BPM-Public-Policy – The IAM policy or the ACL of an AWS bucket has been successfully modified to make it public to all users.
Fact-EA-KerberosNotPreAuth – A user has successfully authenticated against an endpoint via Kerberos authentication with preauthentication 0.
Prof-USwtch-U-U-DU – This is the first time this user has performed an account switch to this account.
Prof-ShA-U-SN – This is the first time this network share has been accessed by this user.
Cntx-PC-ECrit-Server-DE – Destination endpoint is a server: True\False
NumDCP-FUSB-FPC-U-FP – An abnormal number of unique files has been written to peripheral storage devices for this user.
Fact-PCpwrshell-En-SuspEnc – The PowerShell process has been used to execute a command associated with the ChromeLoader malware. This sigma rule is authored by Florian Roth (Nextron Systems), Markus Neis, Jonhnathan Ribeiro, Daniil Yugoslavskiy, Anton Kutepov, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_powershell_base64_encoded_cmd.yml
NumCP-AppLF-EC-U – An abnormal number of application login failures have been observed for this user.
Prof-VPNIn-E-U-DE – This is the first time this user attempted to log into a VPN with this server. These events may include both failed and successful logins.
Cntx-EL-ECrit-CS – Destination endpoint is critical: True\False
NumSP-EMS-Bytes-U-Bytes – An abnormal amount of bytes have been sent in outgoing emails for this user.
Prof-RegW-IFEO-O-U – This is the first time this user has modified or created the Image File Execution Options of a process by writing to the registry value 'Debugger' under the key 'HKLM\SOFTWARE{\Wow6432Node}\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\<executable>'.
Prof-RegR-SAM-O-UD – This is the first time users in this department have read a registry value under the SAM registry key.
Prof-PC-PN-DE-PN – This is the first time this process has been executed on this endpoint. This feature only models processes from - Windows and Unix commands, pentest tools, system enumeration, account enumeration and network sniffers.
Fact-PC-RemoteExecAdminShare – A remote process has been executed and redirected to an admin share. This activity can be related to the execution of Impacket.
Prof-MPermMod-U-O-U – This is the first time this user has modified permissions in a mailbox.
Fact-FCopy-Outlook-FExt – A file ending in a '.pst'/'.ost' extension has been copied.
Prof-SA-E-U-SE – This is the first time a security alert triggered from this endpoint for this user.
NumCP-EScrn-EC-U – An abnormal number of screenshot events have been observed for this user.
Cntx-ShA-PrivU – User is privileged: True\False
Fact-PC-Shell-Base64 – Identifies base64 being decoded and passed to a Linux shell
Fact-PCwmic-ELT – The WMIC (WMI Command Line) process has been used to clear or delete an event log. This sigma rule is authored by Ecco, Daniil Yugoslavskiy, oscd.community, D3F7A5105 and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_eventlog_clear.yml
Prof-DS-AT-U-AT – This is the first time this directory service activity has been observed for this user. Directory services typically manage various types of objects to organize and administer resources within a network environment.
Prof-USB-U-O-U – This is the first time a peripheral device activity has been observed for this user.
Prof-DB-E-UDBN-SZ – This is the first time a successful database event in this database has been observed for this user from this network zone.
Fact-PCcsi-AP – PowerShell starting the C# Interactive Console (csi.exe), which may be used to execute code in an unusual or hidden way. This sigma rule is authored by Michael R. (@nahamike01). The content of this repository is released under the [Detection Rule License (DRL) 1.1](https://github.com/SigmaHQ/Detection-Rule-License). Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_use_of_csharp_console.yml
NumSP-VPNOut-Bytes-U-Bytes – An abnormal amount of bytes have been uploaded in VPN session for this user.
Prof-GMA-U-DE-U – This is the first time this system account has added a user to a group on this endpoint.
Cntx-PCplink-Exfil – Process is 'plink.exe': True\False
Prof-PCnet-U-O-U-netlocalgroupadmin – This is the first time a user account has been added to the administrators group using 'net.exe' for this user.
Fact-EMS-SrcCode – An email containing a source code file attachment has been sent.
Fact-PCcrackmapexec-CrackMapExecWin – The 'crackmapexec.exe' (a penetration testing tool) process has been executed. This sigma rule is authored by Markus Neis and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_apt_dragonfly.yml
Fact-Web-TI-RepDom – An HTTP communication attempt has been made to a bad reputation domain. These events may include both failed and successful traffic.
Fact-PCbcdedit-DisRec – The BCDEdit (Boot Configuration Data Edit) process has been used to disable Windows recovery mode. This sigma rule is authored by E.M. Anhaus (originally from Atomic Blue Detections, Endgame), oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_bcdedit_boot_conf_tamper.yml
Prof-DBQ-RS-SZ-RS – An abnormal successful database query response size has been observed for this source network zone.
NumCP-RegD-Services-EC-DE – An abnormal number of unique service configurations have been deleted from the registry on this device.
NumDC-Git-RepoC-U-Object – An abnormal number of unique repository endpoints where secrets are generally stored, which may indicate unauthorized enumeration or insider reconnaissance activity. Repository name is parsed into the object field which is being counted here.
Prof-GA-Brwsr-UD-Brwsr – This is the first time this web browser has been observed for users in this department.
Fact-PCbitsadmin-AbP – The 'bitsadmin.exe' process has been spawned by a command line executable. This sigma rule is authored by Florian Roth (Nextron Systems), Tim Shelton and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_shell_spawn_susp_program.yml
Prof-CA-IRC-O-U – This is the first time this user executed a remote command on an instance. These events may include both failed and successful executions.
Fact-RegD-RDPCon – The RDP connection history has been cleared via the registry.
Prof-VPNIn-U-O-UD – This is the first time a user in this department attempted to log into a VPN. These events may include both failed and successful logins.
Prof-PrivUse-U-O-UD – This is the first time a Windows privileged has been used and invoked for users in this department.
Cntx-FA-FCrit-SrcExecutable – Source file is an executable: True\False
Fact-PCjava-JavaRD – The Java process has been executed with remote debugging allowed for more than just the localhost. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_vul_java_remote_debugging.yml
Prof-RegD-Services-O-U – This is the first time this user has deleted a service by deleting a registry key\value under the key 'HKLM\SYSTEM\CurrentControlSet\Services'.
NumDCP-AL-UC-Plt-U-SE – An abnormal number of unique user names have been observed in application logins to this platform per source endpoint. These events may include both failed and successful communications.
Fact-PCntdsutil-NTDS – The 'ntdsutil.exe' (NT Directory Service Utility) process has been executed. This sigma rule is authored by Thomas Patzke and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_ntdsutil_usage.yml
Fact-CA-IPM-PublicAWS – A compute image resource in AWS has been made public, granting access to all users.
Prof-BC-U-O-U – This is the first time this user has successfully created a cloud storage bucket.
Fact-FWrite-SystemCADirs – A file was written in a System CA (Certificate Authority) directory.
Cntx-PC-Critical-CredEnum – Process is a credential enumeration tool: True\False
Fact-PCwbadmin-CD – The WBAdmin (Windows Backup Admin) process has been used to delete a backup catalog.
Prof-PC-O-Pdir – This is the first time a process execution has been observed from this directory.
Prof-USB-DevId-U-DevId – This is the first time this peripheral device ID has been observed for this user.
Prof-DllLoad-Ext-O-FileExt – This is the first time a DLL image file with this extension was loaded for the organization.
Fact-RA-WDigest – The WDigest authentication protocol, which uses clear-text credential caching, has been enabled via the registry.
Prof-Login-E-U-DZ – This is the first time this user successfully logged into this network zone.
NumDCP-PCHEnum-TC-U-HEnum – An abnormal number of unique host enumeration tools have been executed for this user.
Fact-FWrite-SSHConfigFile – The sshd_config file was written to.
Cntx-Web-UCrit-Priv – User is privileged: True\False
Fact-RegW-OfficeTest – An Office test file has been modified by writing to the registry key HKCU\Software\Microsoft\Office test\Special\Perf.
Fact-RegE-LSA – The registry key 'HKLM\SECURITY\Policy\Secrets' has been exported from the registry.
Fact-RegW-AppInit – An AppInit DLL registry configuration has been modified or created under the registry key 'HKEY_LOCAL_MACHINE\Software\Microsoft\Windows NT\CurrentVersion\Windows' or 'HKEY_LOCAL_MACHINE\Software\Wow6432Node\Microsoft\Windows NT\CurrentVersion\Windows'
Fact-PCbcdedit-BootEM – bcdedit.exe usage (e.g., delete, deletevalue, import, safeboot, network) tied to boot configuration tampering which may indicate attempts to damage the system or maintain persistence. This sigma rule is authored by @neu5ron. The content of this repository is released under the [Detection Rule License (DRL) 1.1](https://github.com/SigmaHQ/Detection-Rule-License). Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_bcdedit_susp_execution.yml
Prof-CA-IPM-AddMember-O-U – This is the first time a user has successfully modified the attributes of a compute image in AWS and shared it with a user/group.
Fact-PCreg-AutorunMod – The 'reg.exe' process has been used to modify an AutoRun registry key. This sigma rule is authored by Victor Sergeev, Daniil Yugoslavskiy, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_reg_direct_asep_registry_keys_modification.yml
NumCP-ELF-EC-U-SE – An abnormal number of failed endpoint logins from this endpoint have been observed for this user.
Cntx-VPNln-UCrit-Vendor – User is a vendor: True\False
Prof-SA-Elbl-DZ-Dlbl – This is the first time a security alert triggered on a server for this destination network zone.
Fact-PCpwrshell-BitsJob – The PowerShell process has been used to execute a BITS (Background Intelligent Transfer Service) transfer. This sigma rule is authored by Endgame, JHasenbusch (ported to sigma for oscd.community) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules-deprecated/windows/proc_creation_win_powershell_bitsjob.yml
Prof-EMR-ED-UD-ED – This is the first time a user in this department has received an email from this email domain.
Fact-PCwhoami-SysPerm – The 'whoami.exe' process has been executed by the system user.
Fact-PCDotNet-CommandLine – This .NET supporting process was created with an URL in the commandline.
NumDCP-FRead-EC-SA-FP – An abnormal number of unique files have been read in this storage account for this user.
Cntx-PC-Critical-SystemEnum – Process is a system enumeration tool: True\False
Prof-FWrite-UMWorkerProcess-PN-FN – This is the first time this file was created by the 'umworkerprocess.exe' process.
Prof-SA-AN-UD-RN – This is the first time this correlation rule triggered for users in this department.
NumCP-PwdChkout-EC-UD-SC – An abnormal number of password retrievals have been observed for users in this department.
Fact-PCwevtutil-EventTracingClear – The WEvtUtil (Windows Event Utility) process has been used to clear an ETW (Event Tracing for Windows). This sigma rule is authored by @neu5ron, Florian Roth (Nextron Systems), Jonhnathan Ribeiro, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_etw_trace_evasion.yml
Prof-DS-E-U-SE – This is the first time this user performed an activity on a directory service object from this endpoint.
Fact-RegW-EventLogDisabled – The Event Log service has been disabled via the registry.
Prof-STC-O-U – This is the first time a scheduled task has been created for this user.
Fact-PC-SysP – The 'rundll32.exe' process has been used to execute a command associated with CVE-2023-23397.
Fact-PCappcmd-ModIns – The 'appcmd.exe' (IIS Application Command Line) process has been used to install an IIS native-code module.
Prof-PC-PPN-PPN-PN – This is the first time this child process has been observed for this matured parent process.
Cntx-PC-FC-PDir – Process executed from a temporary directory: True\False
Prof-PC-PN-PltSZ-PN – This is the first time this process has been executed in this platform from this network zone. This feature only models processes from - Windows and Unix commands, pentest tools, system enumeration, account enumeration and network sniffers.
Prof-PC-PN-PltUD-PN – This is the first time this process has been executed in this platform for users in this department. This feature only models processes from - Windows and Unix commands, pentest tools, system enumeration, account enumeration and network sniffers.
NumSP-DNSReq-Bytes-O-Bytes – An abnormal amount of bytes were sent in DNS queries from endpoints in the organization.
Prof-EMR-ED-U-ED – This is the first time this user has received an email from this email domain.
Fact-FCopy-Outlook-FDir – A file from the Outlook folder has been copied to a non-Outlook folder.
Prof-PwdChkout-U-O-U – This is the first time this user retrieved a password.
Prof-DSF-AT-UD-AT – This is the first time this directory service activity type failed for users in this department. Directory services typically manage various types of objects to organize and administer resources within a network environment.
Prof-VPNIn-U-O-U – This is the first time this user attempted to log into a VPN. These events may include both failed and successful logins.
Prof-SADLP-Proto-U-Proto – This is the first time a DLP alert triggered on this protocol for this user.
Prof-PC-U-O-U-Insmod – This is the first time a process execution of a 'insmod' (Install Module) command has been observed for this user.
Fact-PCschtasks-TM – The SchTasks (Scheduled Tasks) process has been used to modify the user account configuration of a scheduled task.
Fact-BPM-Public-AccessBlock – The public access block of a bucket or an account in AWS has been successfully modified to remove public access prevention. This activity enables the bucket or the entire account to become public to all users.
Prof-FPM-PublicCloud-P-U – This is the first time this user modified a cloud storage object to become public. By manipulating file permissions to make the object public, attackers can expose the data of important or sensitive files, making them available to read, download or even modify by everyone.
Prof-AL-E-U-SE – This is the first time this user attempted to log into an application from this endpoint. These events may include both failed and successful logins.
Fact-STC-SP – A scheduled task has been configured to execute the PowerShell process.
Prof-WinSC-E-O-DZ – This is the first time a service creation has been observed in this network zone.
Fact-PCmsiexec-WebExec – The MsiExec process (Windows Installer) has been used to execute a remote script using a web addresses parameter. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_msiexec_web_install.yml
NumDCP-EL-DEC-SE-DE – An abnormal number of unique destination endpoints have been observed in successful endpoint login events from this endpoint. These events may include interactive Window logins and other (interactive or not) OS logins.
Prof-PLA-Loc-U-LocCity – This is the first time this user has physically accessed a building in this city.
NumCP-RuleDel-EC-U – An abnormal number of security rules deletion events have been observed for this user.
Fact-RegW-TrustProvider – A trust provider component has been modified via the registry.
Cntx-ShA-NamedPipe – Share is a known named pipe: True\False
Fact-PCat-IJob – The 'at.exe' process has been used to execute an interactive scheduled task. This sigma rule is authored by E.M. Anhaus (originally from Atomic Blue Detections, Endgame), oscd.community, and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/62d4fd26b05f4d81973e7c8e80d7c1a0c6a29d0e/rules/windows/process_creation/proc_creation_win_at_interactive_execution.yml
Prof-CPM-Resource-O-R – This is the first time an IAM policy of a resource in this directory has been successfully modified in GCP. IAM policies determine the roles and permissions granted to users on a resource.
Fact-PCpwrshell-ADS – The PowerShell process has been used to execute a PowerShell script from an ADS (Alternate Data Stream). This sigma rule is authored by Sergey Soldatov, Kaspersky Lab, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_powershell_run_script_from_ads.yml
Prof-GA-RGN-U-RGN – This is the first time this cloud region has been observed for this user.
Fact-PCpwrshell-Base64En – The PowerShell process has been used to decode a Base64 string using 'frombase64string'. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_powershell_frombase64string.yml
Fact-PCeqnedt32-EE – The 'eqnedt32.exe' (EquationEditor) process has been executed. This is a known built in tool used by attackers due to its ability for exploitation. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_exploit_cve_2017_11882.yml
NumDCP-EL-UC-DE-U-SE – An abnormal number of unique user names have been observed in endpoint logins to this endpoint per source endpoint. These events may include both failed and successful communications.
Fact-PCfltmc-SysmonDU – The FltMC (Filter Manager Control) process has been used to unload the Sysmon driver. This sigma rule is authored by Kirill Kiryanov, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_sysmon_driver_unload.yml
NumDC-RA-U-RAC – An abnormal number of role-assume requests have been observed for this user. These events can include both successful and failed assumed roles.
Prof-DllLoad-Ext-SE-FileExt – This is the first time a DLL image file with this extension was loaded on this endpoint.
Prof-PCca-U-O-U – This is the first time root certificate has been installed on a Linux machine using 'update-ca-certificates' or 'update-ca-trust' for this user.
NumDCP-RegR-RPC-Cert-U-RP – An abnormal number of unique certificates and private keys related registry values have been read by this user.
Fact-PCLogMeIn-InstalledAgent – The LogMeIn remote desktop access agent has been installed.
Fact-PCpwrshell-Base64En-Hidden – The PowerShell has been used to execute a known malicious encoded command. This sigma rule is authored by John Lambert (rule) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_powershell_hidden_b64_cmd.yml
Prof-CPM-UCreate-O-U – This is the first time this user created or modified an IAM policy on this cloud platform. IAM policies determine the roles and permissions granted to users on a resource. These events may include both failed and successful creations\modifications.
Prof-STC-O-PN – This is the first time a scheduled task has been created and configured to execute this process for the organization.
Prof-UCreate-U-O-UD – This is the first time a user in this department has created a user account.
Fact-PCcsws-AP – A Windows Script Host process ('cscript.exe' or 'wscript.exe') has been spawned by the RegSvr (Register Server) process. This sigma rule is authored by Florian Roth (Nextron Systems), oscd.community, Tim Shelton and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_regsvr32_anomalies.yml
Prof-USB-E-O-SE - This is the first time a peripheral device activity has been observed from this endpoint.
Prof-RegW-SafeBoot-O-U – This is the first time this user has modifed the safe mode boot configuration by writing to a registry value/key under the registry key HKLM\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal.
Fact-PCrundll32-ADllLoad-Susp – The 'rundll32.exe' process has executed an exported module function using an ordinal number. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_rundll32_by_ordinal.yml
Prof-USB-E-UD-SE – This is the first time a peripheral device activity has been observed from this endpoint for users in this department.
NumCP-VPNlnF-EC-O-U-30Days – An abnormal number of failed VPN logins have been observed for the organization by this user in 30 days.
Prof-EMS-FileExt-O-FileExt – This is the first time a user in the organization has sent an email attachment with this extension.
Prof-USB-DevId-SE-DevId – This is the first time this peripheral device ID has been observed from this endpoint.
Fact-FWrite-SELinuxConfigFile – The SELinux (Security-Enhanced Linux) configuration file was written to.
Prof-Login-E-O-SZ – This is the first time a successful login has been observed from this network zone for the organization.
Fact-PCoffice-Regsvr32 – A Microsoft Office process has spawned the RegSvr (Registration Service) process. This sigma rule is authored by Florian Roth (Nextron Systems), oscd.community, Tim Shelton and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_regsvr32_anomalies.yml
Fact-Web-TITOR-Url – An HTTP communication attempt has been made to a URL containing '/tor/server'. These events may include both failed and successful traffic.
Fact-EL-UnauthorizedWindowsRDP – An unauthorized user has attempted and failed a Remote Desktop Protocol (RDP) login to a Windows endpoint.
NumCP-Auth-MfaEC-U – An abnormal number of Multi-Factor Authentication (MFA) authentication events for this user have been observed. These events may include both failed and successful authentications to an MFA service.
Prof-DS-AT-SE-AT – This is the first time this directory service activity has been observed from this endpoint. Directory services typically manage various types of objects to organize and administer resources within a network environment.
Prof-MFA-AuthMethod-U-AuthMethod – This is the first time this user authenticates with MFA authentication using this authentication method. These events may include both failed and successful logins.
Cntx-ShA-AdminShare – Share is an admin share: True\False
NumSP-FRead-FS-B-Bytes – An abnormal amount of file bytes have been read in this bucket for this user.
Cntx-ELF-LF-BadCred – Login failed due to bad credentials: True\False
Prof-Login-E-UD-DZ – This is the first time a user in this department successfully logged into this network zone.
Prof-ULck-U-O-U – This is the first time this user has locked a user account.
Prof-CPM-URevertAWS-O-U – This is the first time this user has successfully changed the default policy version of a policy in AWS. Policies in AWS are the documents that dictate what permissions are granted to identities and resources.
Prof-Network-Country-DP-SCountry – This is the first time a successful network connection has been observed from this country, determined by geolocation lookup, to the organization with this port.
Fact-PCLsass-ProcDumpLsass – The 'procdump.exe' process has been used to dump the LSASS process. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_sysinternals_procdump_lsass.yml
Prof-DS-A-UDSOT-A – This is the first time this activity has been observed on this directory service object class for this user. Directory services typically manage various types of objects to organize and administer resources within a network environment.
Prof-AL-MFA-U-MFA – This is the first time this user has logged into an application without using multi factor authentication (MFA).
Prof-GMA-U-O-U – This is the first time a user has been added to a group by this user.
Prof-SA-E-SZ-SE – This is the first time a security alert triggered from this endpoint in this network zone.
NumCP-AI-U-Guardrail-Block – An abnormal amount of AI guardrail violations have been observed for a user.
NumCP-PC-CritCmdC-O – An abnormal number of critical command executions have been observed for the organization.
Prof-GA-OS-U-OS – This is the first time this operating system has been observed for this user.
NumDCP-EL-DEC-U-DE – An abnormal number of unique destination endpoints have been observed in endpoint login events for this user. These events may include interactive Window logins and other (interactive or not) OS logins, both failed as successful.
Fact-PCrundll32-PwrshellDll-PPN – The PowerShell process has been used to spawn 'rundll32.exe' and execute a DLL from a temporary folder.
Prof-GA-Country-DZ-SCountry – This is the first time an activity has been observed from this country to this network zone, determined by geolocation lookup.
NumDCP-FRead-FS-U-DE – An abnormal number of unique destination endpoints have been observed in file read events for this user.
Fact-CPM-PCrit-AWSAdmin – A policy with critical administrative permissions has been successfully created or attached to an identity in AWS. Policies in AWS are the documents that dictates what permissions are granted to identities and resources.
Cntx-Network-Protocol – Network protocol
Prof-Web-WebDom-O-Tld – This is the first time a successful HTTP communication to this top level domain has been observed for the organization.
Fact-Web-ShellUserAgent – An HTTP communication attempt has been made with a user-agent associated with a command shell. These events may include both failed and successful traffic.
Prof-FA-SCFA-O-UD – This is the first time source code file activity (by file extension) has been observed for users in this department. File activity could include read, delete, write or any other type of file related operations.
Prof-WinSC-E-DE-DZ – This is the first time a service creation has been observed on this endpoint for this destination network zone.
NumDCP-FRead-EC-B-FP – An abnormal number of unique files have been read in this bucket for this user.
Fact-RegW-AppCert – An AppCert DLL registry configuration has been modified or created under the registry key 'HKEY_LOCAL_MACHINE\System\CurrentControlSet\Control\Session Manager'
Fact-RegW-RootCert – A root certificate has been installed via the registry.
Fact-PCmshta-JsExec – The MsHTA (Microsoft HTML Application) process has been used to execute javascript. This sigma rule is authored by E.M. Anhaus (originally from Atomic Blue Detections, Endgame), oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_mshta_javascript.yml
Prof-FWrite-AuthorizedKeys-O-U – This is the first time an 'authorized_keys' file has been modified by this user.
NumCP-DL-EC-UPlt – An abnormal number of kernel module or drivers have been loaded for this user.
NumCP-DL-EC-SE – An abnormal number of kernel module or drivers have been loaded on this endpoint.
NumDCP-GA-OpC-UPlt-FOp – An abnormal number of unique failed operations have been observed in this platform for this user.
NumCP-DB-DBOpC-U – An abnormal number of database operation events were observed for this user - this can include both unique and non-unique operations. A database operation consists of any action in a database query (i.e. SELECT, DROP, UPDATE, etc...). These events may include both failed and successful operations.
Prof-Fwrite-AuditRule-O-U – This is the first time an audit rule file has been modified by this user.
Cntx-SA-UCrit – User is an executive: True\False
Fact-WinSC-SuspSC-Param – A service has been created with suspicious execution command parameters.
Prof-PCIOC-IOCPenT-U-PenT – This is the first time a process execution of a known pentesting tool has been observed for this user.
NumCP-FDel-EC-U – An abnormal number of file deletion events have been observed for this user.
Prof-FDel-U-O-U-LogFile – This is the first time a log file has been deleted by this user.
NumCP-AI-QC-UO – An abnormal number of successful AI requests for the organization have been performed by this user. AI requests may consist of one or more prompts.
Cntx-EL-UCrit-SA – User is a service account: True\False
Prof-RPM-U-O-UPlt – This is the first time this user modified the permissions of a role on this platform.
Fact-PCdir-UDisc – The 'dir.exe' process has been used to list users by enumerating the users folder.
Cntx-Web-WDCrit-FS – Web domain is a file sharing domain: True\False
NumCP-RegD-EC-DE – An abnormal number of registry deletion events have been observed on this device.
NumCP-PC-ChownCount-U – An abnormal number of 'chown' (Change Owner) process executions have been observed for this user.
NumCP-ELF-EC-U-DE – An abnormal number of failed endpoint logins to this endpoint have been observed for this user.
Prof-BPM-U-PBACL-O-U – This is the first time this user has successful edited the ACL policy of a bucket in AWS.
Fact-LogCl-LogClear-AT – An audit log has been cleared.
Prof-Login-Plt-U-Plt – This is the first time this user has attempted to log into this platform. These events do not include endpoint events and may include both failed and successful logins.
Prof-SA-PN-UD-PN – This is the first time an alert triggered on this process for users in this department.
Fact-PCdctask64-Zoho – The ZOHO 'dctask64.exe' process has been used to perform process injection. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_dctask64_proc_inject.yml
Prof-SA-E-UD-SE – This is the first time a security alert triggered from this endpoint for users in this department.
Prof-VPNIn-E-U-SE – This is the first time this user attempted to log into a VPN from this endpoint. These events may include both failed and successful logins.
Prof-PCMsbuild-E-O-DE – This is the first time the 'msbuild.exe' process has been used to build and execute a project on this endpoint.
NumCP-AI-QC-WID – An abnormal number of successful AI requests has been observed for this workspace. AI requests may consist of one or more prompts.
Cntx-USwtch-UCrit – User is privileged: True\False
Prof-PC-CmdArgs-Msbuild-O-CsprojParam – This is the first time the 'msbuild.exe' process has been used to build this C# project.
NumCP-PC-InsmodCmdC-U – An abnormal number of 'insmod' (Install Module) process executions have been observed for this user.
NumCP-PC-ChmodCount-U – An abnormal number of 'chmod' (Change Mode) process executions have been observed for this user.
Prof-PC-E-NetUserAdd-O-DZ – This is the first time a user account has been created using 'net.exe' on this network zone.
NumCP-EMR-EC-DU – An abnormal number of incoming emails have been observed for this user.
Fact-PCcmdkey-UDisc – The CMDKey (Credential Manager Command Line) process has been used to enumerate cached credentials. This sigma rule is authored by jmallette, Florian Roth (Nextron Systems), Nasreddine Bencherchali (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_cmdkey_recon.yml
NumCP-SEPwrshell-CmdInvC-O-InvC – An abnormal number of PowerShell command invocations have been observed for the organization.
Prof-RegW-U-DetailsLen – An abnormal registry details length has been observed for this user.
NumDCP-VPNln-UC-O-U-SIP – An abnormal number of unique user names have been observed in VPN login for the organization per source IP. These events may include both failed and successful communications.
Fact-PCdsq-DomDisc – The DSQuery (Directory Service Query) process has been used to discover domain trusts. This sigma rule is authored by E.M. Anhaus, Tony Lambert, oscd.community, omkar72 and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_dsquery_domain_trust_discovery.yml
Prof-RegW-COM-U-CLSID – This is the first time this user has modified the registry path to a COM class with this CLSID.
Cntx-PC-Critical-Parent-MSOffice – Parent process is a Microsoft Office process: True\False
Prof-EMS-FileExt-UD-FileExt – This is the first time a user in this department has sent an email attachment with this extension.
Cntx-PCwmic-ADisc – Local accounts enumerated using wmic.exe in on endpoint: True\False
Prof-DS-DSOC-UD-DSOC – This is the first time a user in this department performed an activity on a directory service object with this object class.
Prof-GA-Plt-UD-Plt – This is the first activity observed on this platform for users in this department.
Prof-USwtch-U-O-U – This is the first time this user has switched accounts.
Prof-PC-U-O-U-Modprobe – This is the first time a process execution of a 'modprobe' (Module Probe, a kernel module management tool) command has been observed for this user.
Fact-Fwrite-HiddenFile – Creating a file that starts with ".". File that starts with "." is a hidden file. An attacker can create hidden file to evade detection.
Prof-CA-SPM-AddMember-O-U – This is the first time this user has successfully modified the attributes of a compute snapshot in AWS and shared it with a user/group.
Cntx-EL-ECrit-DC – Destination endpoint is a Domain Controller: True\False
NumCP-FDnld-EC-UD – An abnormal amount of file download events have been observed for users in this department.
Fact-DNS-DomQ-Sunburst – A DNS query has been observed requesting a domain associated with the SUNBURST malware.
Prof-UCreate-U-O-U – This is the first time this user has created a user account.
NumCP-VPNlnF-EC-U – An abnormal number of vpn login failures have been observed for this user.
NumSP-DBQ-RS-U-RS – An abnormal database query response size has been observed for this user. These events may include both failed and successful queries.
Prof-Fwrite-E-O-DE-Xdg – This is the first time a XDG autostart file was created on this endpoint.
Prof-SA-AN-O-AN – This is the first time this security alert triggered in the organization.
Cntx-Web-ECrit-DC – Endpoint is a Domain Controller: True\False
Prof-FA-FDir-DE-NTDSDir – This is the first time a NTDS access has been observed in this folder on this endpoint. NTDS activities could include database attach or detach.
Prof-LogCl-U-O-U – This is the first time an audit log has been cleared by this user.
Prof-EL-E-UD-DE – This is the first time a user from this department attempted to log into this endpoint. These events may include both failed and successful logins.
Fact-MPermMod-UCrit – A user has modified the mailbox permissions of an executive user.
Fact-AI-PI-ShowSystemPrompt – An AI request attempting to display the AI system prompt has been sent.
Prof-STC-PP-TN-PP – This is the first time a scheduled task has been created and configured to execute this process for this task name.
Prof-FUpld-E-U-SE – This is the first time this user has uploaded a file from this endpoint.
Prof-RegA-PP-O-PP – This is the first time this process has performed a registry activity.
Fact-PCschtasks-DA – The SchTasks (Scheduled Tasks) process has been used to deactivate a scheduled defragmentation task. This sigma rule is authored by Florian Roth (Nextron Systems), Bartlomiej Czyz (@bczyz1) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_apt_slingshot.yml
NumCP-AI-CSC-UPLT – An abnormal number of AI conversations have been successfully shared by this user on this platform.
Cntx-PLA-Outcome – Physical access failed: True\False
Prof-AI-U-Guardrail-Block – This is the first time this user has triggered an AI guardrail violation.
Prof-UCreate-U-Plt-UD – This is the first time users in this department have created a user account on this platform.
Prof-UCreate-E-O-SE – This is the first time a user account was created from this endpoint.
Prof-Login-E-DZ-SZ – This is the first time a successful login has been observed from this source network zone to this destination network zone.
Prof-PCnet-U-O-U-user – This is the first time local user accounts have been enumerated using 'net.exe' for this user.
Prof-AuditPolicyMod-U-O-U – This is the first time this user has performed an audit policy modification. These events may include both failed and successful modifications.
Prof-EMR-FileExt-O-FileExt – This is the first time a user in the organization has received an email attachment with this extension.
Fact-PCforfiles-IC – The 'forfiles.exe' process has spawned a child process. This sigma rule is authored by E.M. Anhaus (originally from Atomic Blue Detections, Endgame), oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_lolbin_forfiles.yml
Fact-FWrite-EtcLldSo – The /etc/ld.so.preload file, if present, allows users to add additional shared libraries that will be loaded before the standard libraries. This can be useful for various purposes, such as implementing custom libraries, applying system-wide modifications, or debugging and profiling applications. Attackers could use this file to force the loading of their own malicious libraries, enabling them to modify system behavior, escalate privileges, or intercept sensitive data.
Prof-CA-DA-O-U – This is the first time this user has successfully attached a volume to an instance.
Fact-FA-Sudoers – The /etc/sudoers file is a critical configuration file in Unix-based operating systems. It controls the access and privileges granted to users and groups to execute commands with elevated privileges (root or superuser privileges) using the sudo command. An attacker can try to read this file to know what user he should get access to, or he can try to write to this file and give a user he have access to these privileges.
Prof-GMA-GN-O-GN – This is the first time a user has been added to this group.
Prof-UCreate-E-O-DE – This is the first time a user account was created on this endpoint.
Fact-PCIOC-Mimikatz-PN –The Mimikatz process has been executed.
Fact-PCtaskmgr-SysPerm – The task manager process has been executed by the system user. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_taskmgr_localsystem.yml
Prof-AI-TI-O-TN – This is the first time this AI agent tool has been invoked.
Prof-PC-U-O-USudo – This is the first time a process execution of a 'sudo' (Superuser Do) command has been observed for this user.
Prof-Fwrite-U-O-U-KernelExtExt –This is the first time a kernel extension file was created on MacOS system by this user.
Fact-PCwmiprvse-FireEye –The WMIPrvSe (WMI Provider Host) process has been used to execute a command associated with FireEye Pentesting.
NumCP-Git-EC-U – An abnormal amount of GitHub API access events have been observed for this user.
Fact-PCsetenforce-DisableSELinux – The 'setenforce' command has been used to disable the SELinux (Security-Enhanced Linux).
Prof-STC-TN-O-TN – This is the first time a scheduled task with this name has been created.
Cntx-Web-WDCrit-IP – Web domain is an IP address: True\False
NumSP-FRead-FS-SA-Bytes – An abnormal amount of file bytes have been read in this storage account for this user.
Cntx-PCwhoami-ADisc – Local accounts enumerated using whoami.exe on endpoint: True\False
NumDCP-WebF-WebDomC-U-WebDom – An abnormal number of unique domains have been observed in failed HTTP events for this user.
Prof-PCvssadmin-SCC-O-SE – This is the first time a shadow copy was created using 'vssadmin.exe' from this endpoint.
NumDCP-FDel-U-DE – An abnormal number of unique remote destination endpoints have been observed in file deletion events on this endpoint for this user.
Cntx-VPNln-UCrit-SA – User is a service account: True\False
Fact-PCdnscat-DNSExfil – The DNScat (a DNS tunneling tool) process has been executed. This sigma rule is authored by Daniil Yugoslavskiy, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_dns_exfiltration_tools_execution.yml
Prof-PCipconfig-NetDisc-U-PN – This is the first time a process execution of 'ipconfig.exe' has been observed for this user.
NumDC-ShA-ShareC-U-DS – An abnormal number of unique network shares have been accessed for this user.
NumCP-PC-ModprobeCmdC-DE – An abnormal number of 'modprobe' (Module Probe, a kernel module management tool) process executions have been observed on this endpoint.
Prof-SA-AN-UD-AN – This is the first time this security alert triggered for users in this department.
Fact-RegW-ChromeExt – A Chrome extension has been installed via the registry.
NumCP-MPermMod-EC-U – An abnormal number of mailbox permission modifications have been observed for this user.
Prof-FDnld-E-O-SE – This is the first time a file has been downloaded to this endpoint.
Fact-PCsc-SvcMod-Ingt – The SC (Service Controller) process has been used to change a service binary path or failure command configuration with medium integrity level executed. This sigma rule is authored by Teymur Kheirkhabarov and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_sc_change_sevice_image_path_by_non_admin.yml
NumDCP-Auth-TgsEC-U-Sn – An abnormal number of Ticket Granting Services (TGS) were observed for this user. In Kerberos authentication, a Ticket Granting Ticket (TGT) is a user authentication token issued by the Key Distribution Center (KDC) to be used to request from the Ticket Granting Service (TGS) access tokens for specific resources/systems joined to the domain. This event is notable since it may indicate use of stolen credentials.
Prof-PC-O-COD – This is the first time a process execution of an Office application has opened a remote document from this web domain.
Cntx-PCqwinsta-ADisc – Local accounts enumerated using qwinsta.exe on endpoint: True\False
Fact-PC-LoginHookFile – Adversaries may use a Login Hook to establish persistence executed upon user logon. The plist can be modified using the defaults command-line utility. This behavior is the same for logout hooks where a script can be executed upon user logout.
Cntx-FA-ECrit-CS – Destination endpoint is critical: True\False
Fact-PCregsvr32-SuspExec – The RegSvr (Registration Service) process has been used to download/install/register a new DLL that is hosted on web, on this endpoint. This sigma rule is authored by Florian Roth (Nextron Systems), oscd.community, Tim Shelton and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_regsvr32_anomalies.yml
NumDCP-EL-UC-DE-UUnknown – An abnormal number of unique unknown user names have been observed in failed logins to this endpoint.
Prof-PC-CmdArgs-InstallUtil-O-DLLParam – This is the first time the 'installutil.exe' process has been executed with this DLL file as a parameter.
Prof-SA-AN-U-AN – This is the first time this security alert triggered for this user.
Cntx-PC-Critical-Crit – Process is a known critical command: True\False
Prof-CPM-Resource-U-R – This is the first time an IAM policy of a resource in this directory has been successfully modified by this user in GCP. IAM policies determine the roles and permissions granted to users on a resource.
Prof-STC-TN-UD-TN – This is the first time a scheduled task with this name has been created for users in this department.
Prof-DS-DSOC-U-DSOC – This is the first time this user performed an activity on a directory service object with this object class.
Prof-DB-E-UDBN-SE – This is the first time a successful database event in this database has been observed for this user from this endpoint.
Prof-SA-E-O-SZ – This is the first time a security alert triggered in this network zone.
NumDCP-EL-UC-DE-U – An abnormal number of unique user names have been observed in logins to this endpoint. These events may include both failed and successful logins.
Fact-PCschtasks-TC – The SchTasks (Scheduled Tasks) process has been spawned by a command associated with the 'PowerSploit' or 'Empire' attack tools. This sigma rule is authored by Markus Neis, @Karneades and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_hktl_powersploit_empire_default_schtasks.yml
Prof-GA-Brwsr-O-Brwsr – This is the first time this web browser has been observed for the organization.
Prof-WinSC-E-O-DE – This is the first time a service creation has been observed on this endpoint.
Fact-PCcmstp-UAC – The CMSTP (Connection Manager Profile Installer) has been used to silently install a service profile for all users on an endpoint. This sigma rule is authored by E.M. Anhaus (originally from Atomic Blue Detections, Endgame), oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_uac_bypass_cmstp.yml
Prof-PC-PN-Pdir – This is the first time a process execution has been observed from this directory for this process.
Cntx-VPNln-UCrit-Exec – User is an executive: True\False
Prof-PLA-Loc-U-LocDoor – This is the first time this user has physically accessed this door.
Prof-PC-CmdArgs-Regsvr32-O-SCTParam – This is the first time the 'regsvr32.exe' process has been executed with this SCT file as a parameter.
Prof-UCreate-E-U-SE – This is the first time this user has created a user account from this endpoint.
NumDCP-FWrite-AuditRule-U-DE – An abnormal number of unique endpoints where this user modified the audit.rules file in Unix system.
Fact-PC-Visudo – The /etc/sudoers file is typically edited using the visudo command, which provides a safe way to make changes to the file and prevents multiple simultaneous edits, reducing the risk of syntax errors that could lock users out of administrative access. An attacker can try to read this file to know what user he should get access to, or he can try to write to this file and give a user he have access to these privileges.
Cntx-PC-ECrit-CS-SE – Source endpoint is critical or a Domain Controller: True\False
Prof-FUpld-E-O-SE – This is the first time a file has been uploaded from this endpoint.
Prof-ELNAC-E-U-SMac – This is the first a network access control login event has been observed coming from this MAC address for this user. These events may include both failed and successful logins.
Prof-EL-NTLM-O-SE – This is the first time a successful NTLM login has been observed from this endpoint.
Prof-GA-Mime-O-Mime – This is the first time this MIME type has been observed for the organization. These events do not include network or endpoint platforms.
Prof-RA-U-Plt-U – This is the first time a role has been assigned by this user on this platform.
Fact-PCsocat-Exfil – The 'socat.exe' (a data exfiltration tool) process has been executed. This sigma rule is authored by Daniil Yugoslavskiy, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_exfiltration_and_tunneling_tools_execution.yml
NumSP-FUSB-Bytes-U-Bytes – An abnormal amount of file bytes have been written to peripheral storage devices for this user.
NumCP-FDnld-EC-U – An abnormal amount of file download events have been observed for this user.
NumCP-UPwdMod-O – An abnormal amount of password reset events were observed for this user.
Prof-FDnld-E-U-SE – This is the first time a file has been downloaded to this endpoint for this user.
NumCP-SEPwrshell-WebReq-O-WebReq – An abnormal number of PowerShell web requests have been observed for the organization.
Fact-PCdevtool-BinExec – The DevToolsLauncher process has deployed a process. This sigma rule is authored by Beyu Denis, oscd.community (rule), @_felamos (idea) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_devtoolslauncher.yml
Prof-DB-DBOp-UDDBN-DBOp – This is the first time a database operation has been observed for a user in this department (i.e. "HR", "Finance", etc...). A database operation consists of any action in a database query (i.e. SELECT, DROP, UPDATE, etc...)
Prof-PC-U-O-U-Kextload –This is the first time a process execution of a 'kextload' (Kernel Extension Load) command has been observed for this user.
Prof-AI-AC-O-AT –This is the first time a user in the organization has created an AI agent.
Fact-PCTeamViewer-InstalledService – The TeamViewer remote desktop access service has been installed.
NumDCP-SA-ANC-SE-AN – An abnormal number of unique alerts have triggered from this endpoint.
Prof-AI-TI-UTN-FN – This is the first time this AI agent tool function has been invoked by this user.
Prof-GA-PrivU-PltOp-PrivU – This is the first time this successful operation has been performed on this platform by a non-privileged user. Operations can include function types, APIs, application activities and more.
Prof-DL-E-O-SE – This is the first time a kernel module\driver was loaded on this endpoint.
Prof-AuditPolicyMod-E-O-SE – This is the first time an audit policy modification has been observed from this endpoint. These events may include both failed and successful modifications.
Prof-WinSC-E-UD-DE – This is the first time a service creation has been observed on this endpoint for users in this department.
Prof-FS-T-U-IT – This is the first time an item shared of this type (file, folder, etc) has been observed for this user.
NumDCP-AL-UC-Plt-U-SIP – An abnormal number of unique user names have been observed in application logins to this platform per source IP. These events may include both failed and successful communications.
Fact-PCauditctl-DeleteRules – The 'auditctl' command has been used to delete the audit rules.
Fact-RegW-Netshell – A NetShell helper DLL has been registered or modified by writing the registry key 'HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\NetSh'.
Prof-SEPwrshell-CmdInv-U-CmdInv – This is the first time this user executed a PowerShell script with this command.
Cntx-AuditPolicyMod-ECrit – Endpoint is critical: True\False
NumCP-DNSResp-NXC-O-NX – An abnormal number of DNS queries to NX domains have been observed for the organization.
Fact-PC-Chflags-HiddenFile – The "setfile" unix process can be used to make files hidden by modifying their attributes, making sure they remain undetected by users. An attacker can create hidden file to evade detection.
Prof-EL-E-U-SE – This is the first time this user attempted to login from this endpoint. These events may include both failed and successful logins.
Prof-EMS-FileExt-U-FileExt – This is the first time this user has sent an email attachment with this extension.
Fact-PCfodhelper-UAC – The 'fodhelper.exe' has spawned a child process. This sigma rule is authored by E.M. Anhaus (originally from Atomic Blue Detections, Tony Lambert), oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_uac_bypass_fodhelper.yml
Prof-USB-DevId-UD-DevId – This is the first time this peripheral device ID has been observed for users in this department.
Fact-U-PrivMM – A non-privileged user has been observed accessing an attribute of a privileged directory service user account.
Prof-PC-E-O-SE-Insmod – This is the first time a process execution of a 'insmod' (Install Module) command has been observed on this endpoint.
Prof-GCreate-U-P-U – This is the first time this user has created a group on this platform.
Fact-FWrite-2018APT – The 'ds7002.lnk', which is related to a known attack, was written to.
Cntx-PCwsmprovhost-RP-PN – Process is 'wsmprovhost.exe': True\False
Prof-AI-AC-O-UD – This is the first time a user in this department has created an AI agent.
Prof-GCreate-U-O-U – This is the first time for this user to create a group for the organization.
Fact-PCdllhost-UACCOM – The 'dllhost.exe' process has been used to bypass UAC using COM objects. This sigma rule is authored by Nik Seetharaman, Christian Burkard (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_cmstp_com_object_access.yml
NumCP-DSOW-EC-UD –An abnormal number of directory service write events have been observed for users in this department. Directory services typically manage various types of objects to organize and administer resources within a network environment.
Fact-DllLoadWmiprvse-Exe – The 'wmiprvse.exe' (WMI Provider Service) process has been observed loading a 'cmd.exe' or a 'powershell.exe' image.
Prof-FWrite-AuthorizedKeys-O-UD – This is the first time an 'authorized_keys' file has been modified by users in this department.
Prof-VPNIn-E-O-SE – This is the first time a user attempted to log into a VPN from this endpoint. These events may include both failed and successful logins.
Fact-RegW-GlobalDotName – The registry value GlobalDotName has been created.
Prof-DS-E-O-SZ – This is the first time a user in the organization performed an activity on a directory service object from this network zone.
Prof-PC-Sysvol-O-UD – This is the first time a SYSVOL domain group policy has been accessed by a process for users in this department.
Prof-SA-AN-U-RN – This is the first time this correlation rule triggered for this user.
Prof-PCpwrshell-En-O-PP – This is the first time a process execution of PowerShell with an encrypted command has been observed for this parent process.
Prof-EMS-Country-U-DCountry –This is the first time this user has sent an email to this country, as determined by geolocation lookup.
Prof-PCnet-U-O-U-netuser – This is the first time a user account has been enabled or disabled using 'net.exe' for this user.
Prof-CPM-UAttachAWS-O-U – This is the first time this user attached a policy to an identity (user, group and role) in AWS. Policies in AWS are the documents that dictate what permissions are granted to identities and resources. These events may include both failed and successful attachments.
Cntx-LogCl-ECrit-CS – Endpoint is critical: True\False
Fact-CPM-PCrit-GCPAdmin –A cloud resource policy in GCP has been successfully modified and included critical administrative permissions. IAM policies determine the roles and permissions granted to users on a resource.
Prof-SEPwrshell-wmi-O-U – This is the first time this user executed a PowerShell script with WMI commands.
Fact-PChh-HtmlExec – The HH (HTML Help) process has loaded a '.chm' (Compiled HTML) file. This sigma rule is authored by E.M. Anhaus (originally from Atomic Blue Detections, Dan Beavin), oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_hh_chm_execution.yml
Fact-PCAnyDesk-StartedAgent – The AnyDesk remote desktop access service has been started.
NumCP-AppAuthF-EC-U – An abnormal number of application authentication failures have been observed for this user.
Prof-AI-AC-O-PLT – This is the first time a user in the organization has created an AI agent with this platform.
Prof-WinSC-PP-SN-PP – This is the first time this service was created with this command process path.
Fact-PCsvchost-NoArg – The SvcHost (Service Host) process has been executed without any command line arguments. This sigma rule is authored by David Burkett, @signalblur and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_svchost_execution_with_no_cli_flags.yml
Fact-PCiexplorer-IHttp – The 'consent.exe' (Windows UAC consent dialogue) process has spawned the 'iexplorer.exe' (Internet Explorer) process with system permissions. This sigma rule is authored by Florian Roth (Nextron Systems) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_exploit_cve_2019_1388.yml
Fact-AI-PI-Base64 – An AI request with a base64 string has been sent. While not inherently malicious, Base64 encoding in an AI request may indicate prompt obfuscation.
Prof-PwdChkout-U-O-UD – This is the first time a user in this department retrieved a password.
Prof-PrivUse-E-U-SE – This is the first time a Windows privileged has been used and invoked from this endpoint for this user.
Prof-DS-Attr-U-Attr – This is the first time this privileged user accessed this directory service attribute.
Prof-LogCl-E-O-DE –This is the first time an audit log has been cleared on this endpoint.
Prof-SA-DP-DZ-DP – This is the first time a network alert on this port has been triggered for this destination network zone.
Prof-GA-Country-SZ-DCountry – This is the first time an activity has been observed to this country for this network zone, determined by geolocation lookup.
Cntx-PCwsmprovhost-RP-PPN – Parent process is 'wsmprovhost.exe': True\False
Fact-PCbcdedit-DisRec-BootSP – The BCDEdit (Boot Configuration Data Edit) process has been used to Windows error recovery. This sigma rule is authored by E.M. Anhaus (originally from Atomic Blue Detections, Endgame), oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_bcdedit_boot_conf_tamper.yml
Fact-PC-Chmod-Setgid – The setgid bit was set using chmod, which can cause a file to execute with the privileges of its group.
NumDCP-VPNln-UC-SE-U – An abnormal number of unique user names have been observed in VPN login from this endpoint. These events may include both failed and successful communications.
Prof-FA-SCFA-O-U – This is the first time source code file activity (by file extension) has been observed for this user. File activity could include read, delete, write or any other type of file related operations.
Fact-PCLsass-Lsass – The WERFault (Windows Error Reporting Fault) process has been used to dump the LSASS process. This sigma rule is authored by sigma and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_lsass_dump.yml
Cntx-PC-Critical-Parent-Pentest – Parent process is a known pentesting tool
Prof-GA-Country-O-SCountry – This is the first time an activity has been observed from this country, determined by geolocation lookup.
Fact-PCIOC-Mimikatz – The PowerShell process has been used to execute a Mimikatz command.
Prof-PC-U-COD – This is the first time a process execution of an Office application has opened a remote document from this web domain for this user.
Prof-UKeyCreate-U-O-U – This is the first time this user has generated an access key for a user account.
Prof-AI-TI-U-TN – This is the first time this AI agent tool has been invoked by this user.
Fact-RegW-ControlPanel – A control panel item has been registered by writing to a registry key/value under HKCU\Software\Microsoft\Windows\CurrentVersion\Control Panel\Cpls.
Fact-PCmklink-SCA – The 'mklink.exe' process has been used to create a symbolic link to a shadow copy. This sigma rule is authored by Teymur Kheirkhabarov, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_shadow_copies_access_symlink.yml
Prof-EMS-AC-U-A – An abnormal number of email attachments have been observed in an outgoing email for this user.
Fact-PCappcmd-IIS – The 'appcmd.exe' (IIS Application Command Line) process has been used to disable IIS HTTP logging .
Prof-GMA-E-O-SZ – This is the first time a user has been added to a group from this network zone.
NumSP-Web-Bytes-UD-BytesStorageOut – This is the first time a user has been added to a group from this network zone.
Prof-RegR-LSA-O-UD – This is the first time users in this department read have read a LSA secret from the registry.
Prof-EL-E-U-DE – This is the first time this user attempted to log into this endpoint. These events may include both failed and successful logins.
Fact-PCopenwith-Exec – The OpenWith process has been used to execute a program. This sigma rule is authored by Beyu Denis, oscd.community (rule), @harr0ey (idea) and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_openwith.yml
Fact-AI-PI-IgnoreInsruct – An AI request attempting to cause the agent to ignore instructions has been sent.
NumCP-DNSResp-NXC-SE-NX – An abnormal number of DNS queries to NX domains from this endpoint have been observed.
NumCP-PCpwrshell-EC-U – An abnormal number of PowerShell process executions have been observed for this user.
Prof-SA-E-O-SE – This is the first time a security alert triggered from this endpoint.
NumCP-VPNlnF-EC-O-U-1Day – An abnormal number of failed VPN logins have been observed for the organization by this user in a day.
Prof-PC-E-NetUserAdd-O-DE – This is the first time a user account has been created using 'net.exe' on this endpoint.
Fact-PCwmic-SCC – The WMIC (WMI Command Line) process has been used to create a shadow copy. This sigma rule is authored by Teymur Kheirkhabarov, Daniil Yugoslavskiy, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_shadow_copies_creation.yml
NumDCP-RegW-RPC-ServicesStop-DE-RP – An abnormal number of unique services have been stopped by modifying the registry on this endpoint.
Fact-WebMtgM-RmPwd – A meeting has been modified to remove the meeting password.
Fact-CA-Startup-StartupScriptGCP –A startup or shutdown script have been added or modified in a instance in GCP.
NumSP-SADLP-Bytes-U-Bytes – An abnormal amount of outgoing bytes have been recorded in DLP alerts for this user.
Fact-RegW-SIP – A SIP component has been modified via the registry.
NumDCP-PLA-LocC-U-LocDoor – An abnormal number of unique doors have been observed in physical access events for this user.
Prof-RegW-Services-O-UD – This is the first time users in this department have modified or created a service by writing a registry key\value under the key 'HKLM\SYSTEM\CurrentControlSet\Services'.
Prof-DS-E-UD-SZ – This is the first time a user in this department performed an activity on a directory service object from this network zone.
Cntx-GMA-ULocal – User is local: True\False
Fact-Web-TI-IOC – An HTTP communication attempt has been made to a known malicious URL. These events may include both failed and successful traffic.
Prof-UCreate-Dom-U-DDom – This is the first time this user has created a user account on this domain.
Fact-FRead-Lssas – A process has directly read from the memory space of 'lsass.exe'.
Prof-EMS-Country-O-DCountry – This is the first time a user in the organization has sent an email to this country, as determined by geolocation lookup.
Prof-RegR-Certs-U-RP – This is the first time this user has read this certificate\private key related registry value.
Prof-PrivUse-E-SE-SZ – This is the first time a Windows privileged has been used and invoked from this endpoint and from this network zone.
Fact-PCbginfo-VBExec – The BgInfo (Background Information) process has used a .bgi file to bypass application whitelisting. This is notable as this method allows blindly trusted signed binaries to write code which can be leveraged to run malicious actions. This sigma rule is authored by Beyu Denis, oscd.community and is licensed under Detection Rule License (DRL), https://github.com/SigmaHQ/sigma/blob/master/LICENSE.Detection.Rules.md. Reference: https://github.com/SigmaHQ/sigma/blob/master/rules/windows/process_creation/proc_creation_win_susp_bginfo.yml
Cntx-USwtch-DUCrit – Dest user is privileged: True\False
Prof-RegW-UAC-O-U – This is the first time this user has modified or created a registry key\value under the UAC configuration key 'HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System'.
Fact-PC-DisableAuditd –Auditd service was disabled.