- Onboard Cloud Collectors
- Shareable Service Accounts
- Add Accounts for AWS Cloud Collectors
- Add Accounts for Cisco Duo Cloud Collector
- Add Accounts for Google Cloud Collectors
- Add Accounts for Microsoft Cloud Collectors
- Add Accounts for Okta Cloud Collectors
- Add Accounts for Salesforce Cloud Collectors
- Add Accounts for Splunk Cloud Collectors
- Add Accounts for Trend Micro Cloud Collectors
- Add Accounts for Wiz
- Abnormal Security Cloud Collector
- Anomali Cloud Collector
- AWS CloudTrail Cloud Collectors
- AWS CloudWatch Cloud Collector
- AWS CloudWatch Alarms Cloud Collector
- AWS GuardDuty Cloud Collector
- AWS S3 Cloud Collector
- AWS Security Lake Cloud Collector
- AWS SQS Cloud Collector
- Azure Activity Logs Cloud Collector
- Azure Blob Storage Cloud Collector
- Azure Log Analytics Cloud Collector
- Azure Event Hub Cloud Collector
- Azure Storage Analytics Cloud Collector
- Azure Virtual Network Flow Cloud Collector
- Box Cloud Collector
- Broadcom Carbon Black Cloud Collector
- Cato Networks Cloud Collector
- ChatGPT Enterprise Cloud Collector
- Cisco Duo Cloud Collector
- Cisco Meraki Cloud Collector
- Cisco Secure Endpoint Cloud Collector
- Cisco Umbrella Cloud Collector
- Cloudflare Cloud Collector
- Cribl Cloud Collector
- CrowdStrike Cloud Collectors
- Cylance Protect (now Arctic Wolf) Cloud Collector
- DataBahn Cloud Collector
- Dropbox Cloud Collector
- GCP Cloud Logging Cloud Collector
- GCP Pub/Sub Cloud Collector
- GCP Security Command Center Cloud Collector
- Gemini Enterprise Cloud Collector
- GitHub Cloud Collector
- Gmail BigQuery Cloud Collector
- Google Workspace Cloud Collector
- Google Security Operations Cloud Collector
- LastPass Cloud Collector
- Microsoft Copilot Integration
- Microsoft Defender XDR (via Azure Event Hub) Cloud Collector
- Microsoft Entra ID Context Cloud Collector
- Microsoft Entra ID Logs Cloud Collector
- Microsoft 365 Exchange Admin Reports Cloud Collector
- Supported Sources from Microsoft 365 Exchange Admin Reports
- Migrate to the Microsoft 365 Exchange Admin Reports Cloud Collector
- Prerequisites to Configure the Microsoft 365 Exchange Admin Reports Cloud Collector
- Configure the Microsoft 365 Exchange Admin Reports Cloud Collector
- Troubleshooting the Microsoft 365 Exchange Admin Reports Cloud Collector
- Recover Stopped Log Ingestion for Microsoft 365 Exchange Admin Reports Cloud Collector
- Microsoft 365 Management Activity Cloud Collector
- Microsoft Security Alerts Cloud Collector
- Microsoft Sentinel (via Event Hub) Cloud Collector
- Mimecast Cloud Collector
- Mimecast Incydr Cloud Collector
- Netskope Alerts Cloud Collector
- Netskope Events Cloud Collector
- Okta Cloud Collector
- Okta Context Cloud Collector
- OpenAI Cloud Collector
- Palo Alto Networks Cortex Data Lake Cloud Collector
- Palo Alto Networks XDR Cloud Collector
- Phishing Email Inbox Cloud Collector
- PingOne Identity Cloud Collector
- Progress ShareFile Cloud Collector
- Proofpoint On-Demand Cloud Collector
- Proofpoint Targeted Attack Protection Cloud Collector
- Qualys Cloud Collector
- Recorded Future Cloud Collector
- Recorded Future Context Cloud Collector
- Rest API Cloud Collector
- S2W Threat Intelligence Cloud Collector
- Salesforce Cloud Collector
- Salesforce EventLog Cloud Collector
- SentinelOne Alerts Cloud Collector
- SentinelOne Cloud Funnel Cloud Collector
- SentinelOne Threats Cloud Collector
- SentinelOne Cloud Collector
- ServiceNow Cloud Collector
- Slack Cloud Collector
- Snowflake Cloud Collector
- Sophos Central Cloud Collector
- Splunk Cloud Collector
- STIX/TAXII Cloud Collector
- Symantec Endpoint Security Cloud Collector
- Tenable Cloud Collector
- Trend Vision One Cloud Collector
- Trellix Endpoint Security Cloud Collector
- Vectra Cloud Collector
- Webhook Cloud Collectors
- Wiz API Cloud Collector
- Workday Cloud Collector
- Zoom Cloud Collector
- Zscaler ZIA Cloud Collector
- Shareable Service Accounts
Scenarios that Require Specific Configuration
Some Cribl logs require additional configuration in order to be parsed effectively in Exabeam. To ensure these logs reach the appropriate Exabeam parsers, the necessary steps must be performed in Cribl Stream. Follow the links in the scenarios listed below for information about the required configurations:
Collecting Data from a Splunk Source – Configure a pipeline in your Cribl Stream connection that extracts a specific subset of the
_rawfield of a Cribl log file.Adding Metadata Fields – Configure default and custom metadata fields to be ingested in the expected format with Cribl raw logs. Correct configuration ensures the metadata can be accurately parsed and mapped for use in downstream applications.
Targeting Parsers that Require Augmented Metadata – Configure a pipeline in your Cribl Stream connection that includes a
Maskfunction with a regex replace statement that inserts the necessary metadata key-value pairs into the_rawfield of Cribl log files.
Collecting Data from a Splunk Source
To collect Cribl logs from a Splunk source, a specific subset of information in the _raw field of the log is required. In order for Splunk data to be collected and parsed appropriately in Exabeam, this subset of information must be extracted and used to replace the original _raw field in the log.
To streamline this extract and replace process, Exabeam provides a JSON code snippet. When included in a pipeline, this JSON code creates an Eval function that filters for the required information in the _raw field, extracts it, and overwrites the original field with the result.
To implement this configuration:
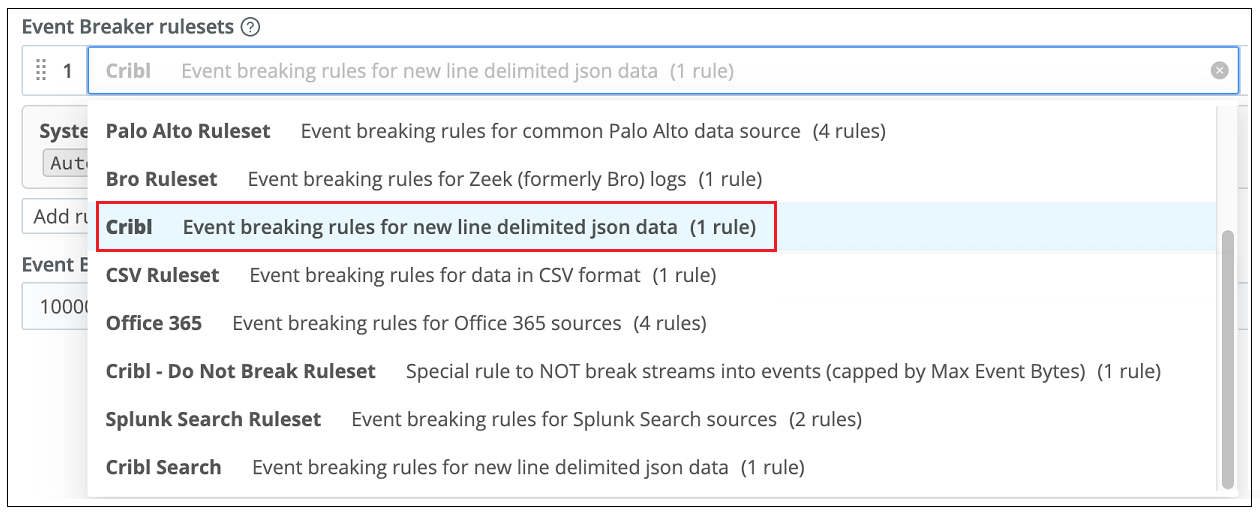
Open your Splunk Search source and navigate to the Configuration screen. Click Event Breakers and use the Ruleset drop down to switch from the default Splunk ruleset to the Cribl ruleset called Cribl Event breaking rules for line delimited json data. Save the change.
Copy the following JSON code snippet and save it.
{
  "id": "Splunk_Search_Extract_Raw",
  "conf": {
    "output": "default",
    "streamtags": [],
    "groups": {},
    "asyncFuncTimeout": 1000,
    "functions": [
      {
        "filter": "result != null && result._raw != null",
        "conf": {
          "add": [
            {
              "disabled": false,
              "name": "_raw",
              "value": "result._raw"
            }
          ]
        },
        "id": "eval",
        "description": "Update Splunk search results (broken as JSON) to overwrite _raw with result._raw"
      }
    ]
  }
}
In your Cribl Stream worker group, navigate to Processing -> Pipelines.
Create a new pipeline using the Import from File option. See Adding Pipelines in the Cribl documentation.
Navigate to where you saved the JSON code in Step 2 and select the file. Click Import and then Save.
In Cribl Stream, navigate to Routing and select QuickConnect or Data Routes to route data to a specific destination based on the standard your organization uses.
Create a connection between your Splunk source on the left and your Exabeam destination on the right. See QuickConnect in the Cribl documentation.
Note
If you have multiple Exabeam destinations configured, make sure you select the one associated with the appropriate Cribl Cloud Collector.
When the Connection Configuration dialog box is displayed, click the Pipeline option. The Add Pipeline to Connection dialog box opens.
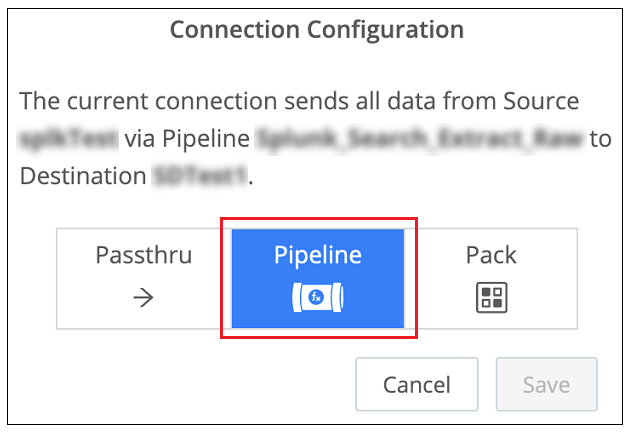
Select the radio button next to the pipeline you created in Step 4 and click Save. The pipeline is added to the connection between your Splunk source and your Exabeam destination.
When the pipeline configuration is complete, verify that Splunk data is collected successfully in your Cribl Cloud Collector and that the collected logs are parsed correctly in downstream Exabeam services.
Adding Metadata Fields
If you want to add specific metadata fields to your Cribl message logs and ensure that they are correctly extracted and mapped to Exabeam target fields, some configuration is required. Two types of metadata fields are supported for ingestion:
Default metadata fields – These fields are available natively in Exabeam but require configuration on the Cribl side to ensure the logs are ingested in the expected format. This type of metadata includes fields like
siteidandhostname. When these fields are mapped in Exabeam, they appear with them_prefix:m_siteid,m_hostname.Custom metadata fields – These fields can be configured based on any field you want to include as metadata in a Crible message log. This type of metadata requires configuration on both the Crible side and the Exabeam side. In Exabeam, a custom metadata field must be configured in the Advanced Settings section of a Cribl Cloud Collector. In the Cribl source, a field with the same name must be configured in the expected format for ingestion by the cloud collector. When these fields are mapped in Exabeam, they appear with the
m_logtags_prefix. Examples:m_logtags_department,m_logtags_servertype.
Expected Log Format
The sample below shows the expected format for log message containing both default and custom metadata. The table below the sample log explains each instance of metadata in the log.
{"message":
        {"@timestamp": "2026-01-27T12:30:01.279Z",
        "collector_type": "cribl-logs",
        "collector_name": "exa-cribl-logs-SDTest1",
        "collector_id": "9922583e-660c-42d9-aea6-9f5d8fb9b48a",
        "message": "RAW MESSAGE GOES HERE",
        "timezone_offset": "+0200",
        "hostname": "test-cc-hostname",
        "forwarder": "test-forwarder",
        "siteid": "123123",
        "logtags":
                {
                "department":"HR",
                "servertype":"PCI",
                },
        "origin":
                {"hostname": "ngsc-si-windows-2022-core",
                "@timestamp": "2026-01-27T12:30:01.279Z",
                "path": "C://Program Files/logs.txt"
                }
        }
}
Metadata Type | Source Field | Mapped Field | Raw Log Example | Description |
|---|---|---|---|---|
Identifier Fields | The metadata fields above the | |||
Default Fields | These metadata fields are available by default in Exabeam but may require configuration in Cribl to ensure they are ingested as metadata by the cloud collector. When these fields are ingested, they are mapped to Exabeam fields with an | |||
|
| +0200 | Specifies the time zone of the location where the log was collected. It serves as a fallback if the correct time zone cannot be parsed directly from the raw log. It can be configured in the optional Advanced Settings when creating a cloud collector. | |
|
| test-cc-hostname | Specifies the host where the collector that ingested the log is deployed. | |
|
| test-forwarder | Specifies the Syslog host from which a syslog message was sent. | |
|
| 123123 | Specifies a unique site ID for data segregation purposes. It ensures that log access adheres to any configured data access permissions. | |
Logtag Fields | These fields are custom metadata fields and they must be included in the | |||
Origin Fields | In cases where logs are being sent from an external source to a central log collection location, this group of metadata fields provides specific information about the external source. For example, if a Windows Event collector sends logs to a Site Collector, the origin metadata fields describe the Window Event collector. When these fields are ingested, they are mapped to Exabeam fields with an | |||
|
| ngsc-si-windows-2022-core | Specifies the source host where the external collector is installed. In the example above, the origin | |
|
| 2026-01-27T12:30:01.279Z | Specifies the date and time the log was sent from the external host. | |
|
| C://Program Files/logs.txt | Specifies the exact file path if a log was collected from a location with multiple files. | |
Configuring Metadata Fields
If you want to add any of the default or origin metadata fields to your Cribl logs so they will be ingested by a Cribl Cloud Collector, some configuration on the Cribl side is necessary. Follow the procedure to Configure Cribl Stream to Output to Cloud Storage Destinations. This procedure ensures that metadata fields are included as expected in the raw log structure described above and that they will be available for parsing in Exabeam. On the Exabeam side, these types of metadata fields are already supported and available for use.
If you want to add custom metadata fields to your Cribl logs, follow the Exabeam procedure to Configure the Cribl Cloud Collector and add the following steps before you click Install to create the collector:
Note
Modifying an existing Cribl cloud collector to add custom metadata fields is not currently supported. Custom metadata can only be incorporated when you configure a new Cribl cloud collector from scratch.
In the Configuration panel, below the collector Name, click the down arrow to expand the optional Advanced Settings section.
In the Custom Metadata Fields section, enter a field name that you want to include as metadata. You can enter any field as long as an identically named field is configured in Cribl for inclusion in log messages.
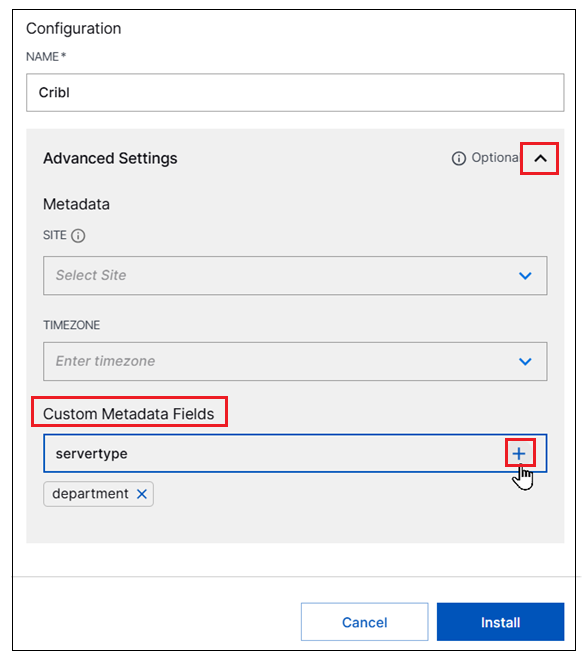
Click the plus icon to add the field.
Add up to ten custom metadata fields and click the plus icon after entering each one.
To complete the configuration on the Cribl sie, follow the procedure to Configure Cribl Stream to Output to Cloud Storage Destinations. Ensure that the same fields are included in the expected in the raw log structure described above.
Targeting Parsers that Require Augmented Metadata
Some Exabeam parsers require a specific metadata key-value pair to be present in log messages that are ingested from Cribl. This metadata must be present in the _raw field of a Cribl log file in order for the log to be evaluated by the appropriate Exabeam parser. To determine if you are using parsers that require augmented metadata, and to find the exact conditions that must be added to outgoing logs, see the table in Parsers that Require Augmented Metadata.
One method for augmenting Cribl logs with the required metadata, is to create a pipeline and apply it to the connection between the source and your Exabeam destination. Add a Mask function to the pipeline that includes Regex statements that will insert the required exact conditions into outgoing logs. The steps below outline this procedure. However, depending on the source you are using, additional filtering logic is sometimes required. Consult your Cribl representative for help in such cases.
To implement this method of augmenting log metadata:
In your Cribl Stream worker group, navigate to Processing -> Pipelines.
Create a new pipeline using the Create Pipeline option. See Adding Pipelines in the Cribl documentation.
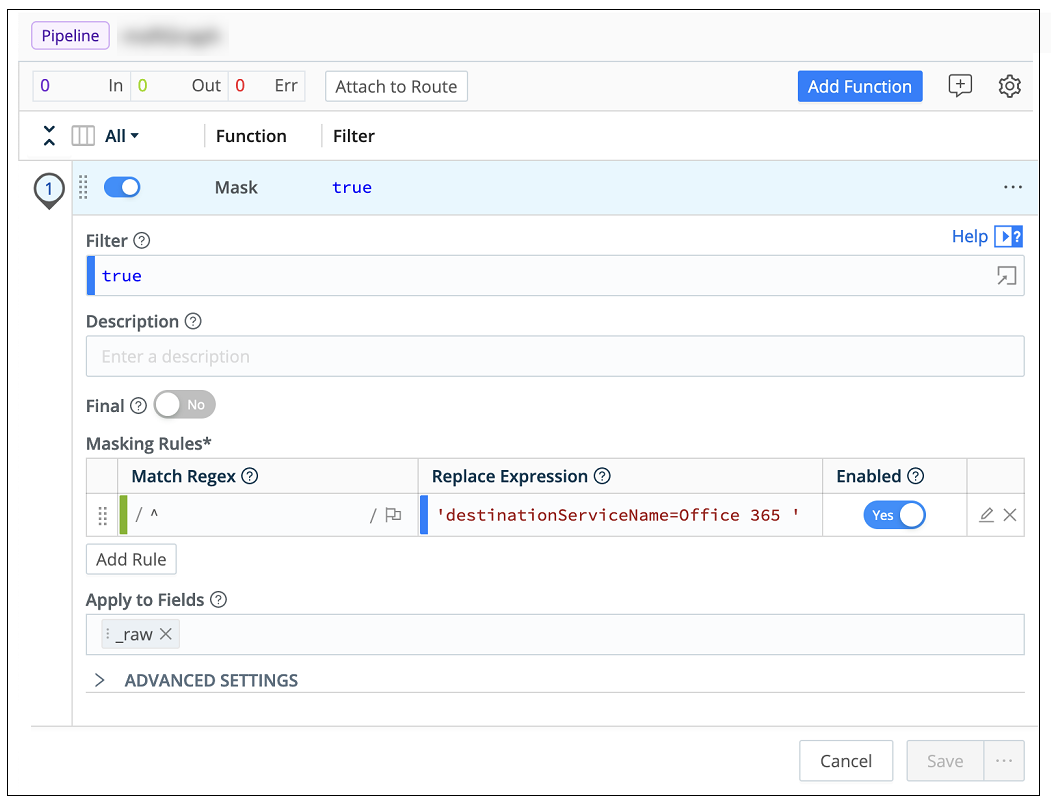
Open the new pipeline and add a standard Mask function to it. Configure the following information:
Match Regex statement – Add a Regex expression that will find the start of the log message.
Replace Expression – Enter the exact condition required for a specific parser designed for a specific vendor and product. To find the exact condition, see the table in Parsers that Require Augmented Metadata.
The image below shows an example of a configured Mask function. For more information, see Function/Mask in the Cribl documentation.
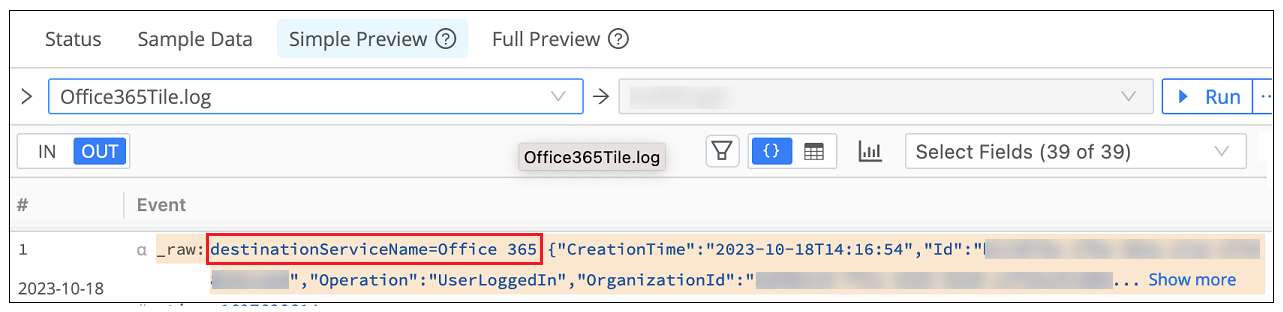
To verify that the exact condition is added properly to the front of outgoing logs, use the Simple Preview to check the outgoing message. It should look similar to the example below.
Save the pipeline configuration.
Navigate to Routing -> QuickConnect.
Create a connection between a specific source on the left and your Exabeam destination on the right. See QuickConnect in the Cribl documentation.
When the Connection Configuration dialog box is displayed, click the Pipeline option
Select the radio button next to the pipeline you just created and click Save. The pipeline is added to the connection between your source and your Exabeam destination.
When the pipeline configuration is complete, verify that data from the relevant source is collected successfully in your Cribl Cloud Collector and that the collected logs are parsed correctly in downstream Exabeam services. If the data is not parsed as expected, you might need add further logic to the pipeline. Consult your Cribl representative for help.
Parsers that Require Metadata Augmentation
This table lists Exabeam parsers, by vendor and product, that require augmentation in a Cribl log message in order for the log to be evaluated by the appropriate parser. For example, in order for a Cribl log message to be parsed by the Amazon AWS CloudTrail parser (amazon-awscloudtrail-sk4-app-activity-aws), the log message must contain a key/value pair in the form of the following exact condition: 'destinationServiceName=AWS'.
Vendor | Product | Exabeam Parser | Exact Condition |
|---|---|---|---|
Amazon | AWS CloudTrail |
|
|
|
| ||
AWS CloudWatch |
|
| |
|
| ||
Bitglass | Bitglass CASB |
|
|
BlackBerry | BlackBerry Protect |
|
|
Box | Box Cloud Content Management |
|
|
|
| ||
|
| ||
Cisco | Cisco Meraki MX applicance |
|
|
Cisco Umbrella |
|
| |
|
| ||
|
| ||
|
| ||
Duo Access |
|
| |
|
| ||
|
| ||
|
| ||
Citrix | Citrix Gateway |
|
|
Citrix ShareFile |
|
| |
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
Cloudflare | Cloudflare Insights |
|
|
|
| ||
Cloudflare WAF |
|
| |
Delinea | Centrify Zero Trust Privilege Serivices |
|
|
Egnyte | Egnyte |
|
|
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
GitHub | GitHub |
|
|
GCP CloudAudit |
|
| |
Google Cloud Platform |
|
| |
|
| ||
Google Workspace |
|
| |
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
Illumio | Illumio Core |
|
|
LastPass | LastPass |
|
|
|
| ||
|
| ||
|
| ||
Microsoft | Azure AD Activity Logs |
|
|
Azure Monitor |
|
| |
|
| ||
|
| ||
|
| ||
|
| ||
M365 Audit Logs |
|
| |
Microsoft 365 |
|
| |
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
Microsoft CAS |
|
| |
Microsoft Defender for Endpoint |
|
| |
|
| ||
Microsoft DNS Log |
|
| |
|
| ||
Network Security Group Flow Logs |
|
| |
Mimecast | Mimecast Secure Email Gateway |
|
|
|
| ||
|
| ||
|
| ||
|
| ||
Netskope | Netskope Security Cloud |
|
|
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
|
| ||
Okta | Okta Adaptive MFA |
|
|
|
| ||
OneLogin | OneLogin |
|
|
Ping Identity | PingOne |
|
|
|
| ||
|
| ||
Salesforce | Salesforce |
|
|
|
| ||
|
| ||
ServiceNow | ServiceNow |
|
|
Slack | Slack |
|
|
Symantec | Symantec Advanced Threat Protection |
|
|
Symantec CloudSOC |
|
| |
|
| ||
Symantec Web Security Service |
|
| |
|
| ||
|
| ||
|
| ||
|
| ||
Tenable.io | Tenable.io |
|
|
VMware | Carbon Black CES |
|
|
|
| ||
Carbon Black EDR |
|
| |
|
| ||
Zoom | Zoom |
|
|
|
|